Frequently Asked Questions and Troubleshooting in ETM Identity
The following are some of the commonly asked questions and their troubleshooting solutions:
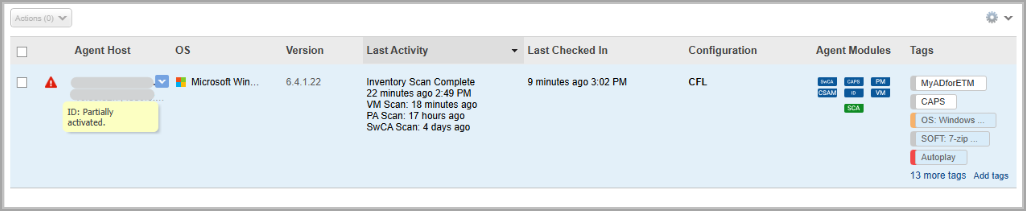
Why does the Cloud Agent UI show Error: ID Partially Activated?
You may see the ID Partially Activated message on the Cloud Agent UI. The agent shows as partially activated because the Policy Audit module is not enabled for the host asset. This behavior is expected and by design. If you activate ETM Identity and its dependent modules are not present, the Cloud Agent UI displays this warning.
Since ETM Identity now includes its own misconfiguration detections, the Partially Activated warning icon no longer indicates the status of ETM Identity. Even when this warning appears, ETM Identity remains enabled and functions as expected.
Why is the ID Misconfigurations tab no longer available?
After UAI migration, you no longer see the dedicated ID Misconfigurations tab. The Misconfigurations tab now includes misconfigurations that were previously displayed under the ID Misconfigurations tab. As a result, the dedicated ID Misconfigurations tab has been removed. This change provides a single view of all detected misconfigurations.
If the Policy Audit (PA) module is also enabled, the Misconfigurations tab will display all misconfigurations from both Policy Audit and ETM Identity.
Why are misconfigurations not displayed after UAI migration?
After a UAI migration, misconfigurations do not appear automatically. You must run a full scan first. After the scan completes, the detected misconfigurations appear in the Misconfigurations tab. If you do not run a full scan, the tab may remain empty because no Misconfigurations data has been collected.
How do I trigger a full scan after UAI migration?
To trigger a full scan:
- Go to the Cloud Agent application.
- Deactivate the ETM Identity application.
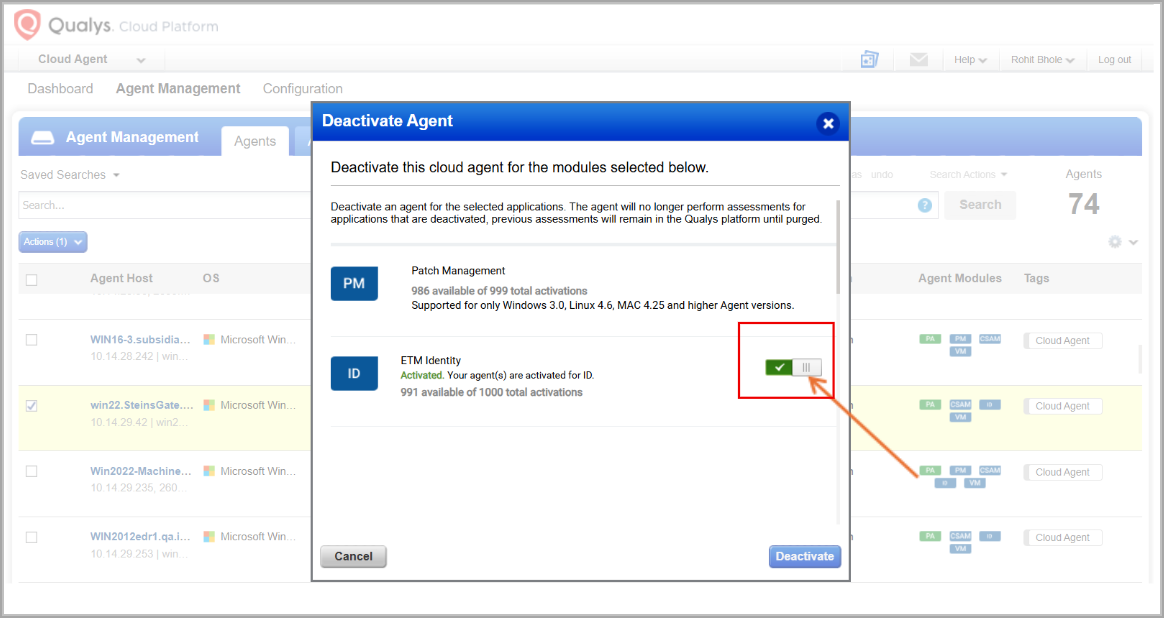
- Wait approximately 20 to 25 minutes.
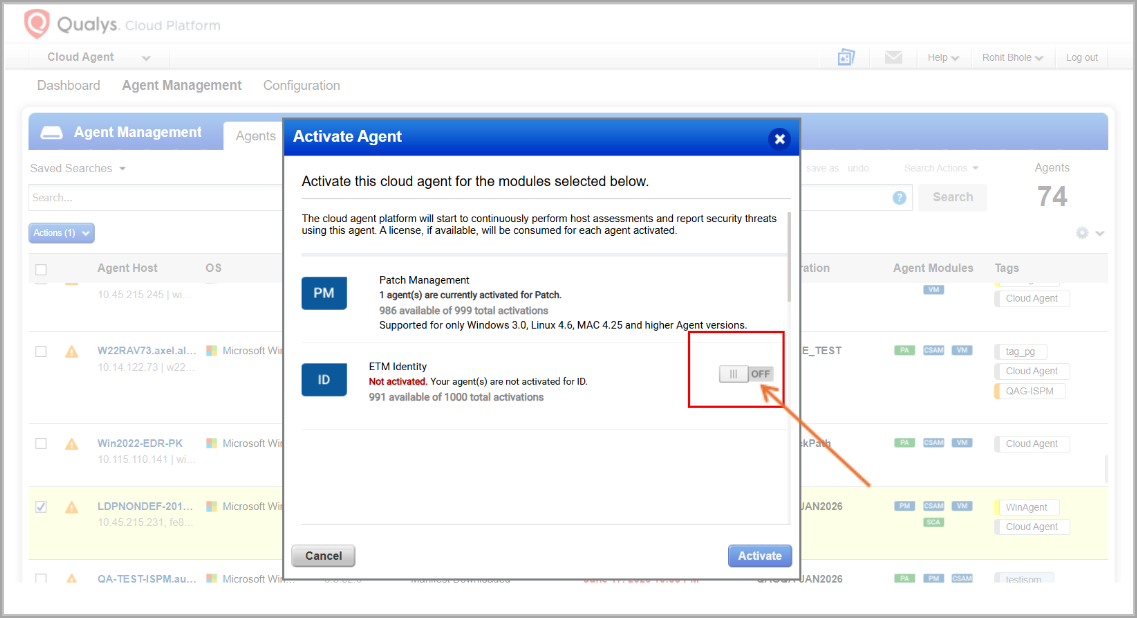
- Re-enable the ETM Identity application.
The module reactivation triggers a full scan.
Why is the Configuration tab unavailable, and how do I assign an ACS score?
The Configuration tab is available only in the asset inventory from Qualys environments. In these environments, default system-created groups are automatically assigned ACS scores. For example, Domain Admins (a Tier 0 group) is assigned an ACS score of 5 by default.
For UAI-enabled tenants, the Configuration tab is not available. Instead, use Dynamic Tags to assign ACS scores. By default, all groups are assigned an ACS score of 2, but you can create dynamic tags rule to assign higher or lower ACS scores as needed.
Why is a TruRisk™ score not displayed for some users?
TruRisk™ Score is the overall risk score assigned to the asset based on the following contributing factors:
- Asset Criticality Score (ACS)
- Qualys Detection Score (QDS) for each misconfiguration
- Auto-assigned weighting factor (w) for each criticality level of the misconfiguration
If a user has no misconfigurations, Qualys cannot calculate a TruRisk score. In this case, the application displays a dash (-) instead of a score.
After Qualys detects misconfigurations for the user, the TruRisk™ score is calculated and displayed.
TruRisk Formula
Here is the TruRisk calculation formula used to calculate the TruRisk score of managed and unmanaged assets:
ARS = {[ACS * External] * [MaxDetectionScore * g(MaxDetectionScore) ] } + numCriticalDetections * WtCrit + numHighDetections * WtHigh + min(numMediumDetections,2000) * WtMed + min(numLowDetections,2000) * WtLow] Final ARS = MIN(ARS, 1000)
Where,
- ACS - Asset Criticality Score,
- External - If the asset is External (Internet Facing), the score gets 20% higher weight if Asset is Internet Facing,
- MaxDetectionScore - Highest value of Detection Score among all detections (range 1-100)
- g(MaxDetectionScore) - To prioritize among detections g_value is introduced, which is 1.3 if there are critical Detections, 1.2 if there are High detections and 1 if there are Medium and Low detections.
- numCriticalDetections - Number of Critical Detections (number of Detections detected with the Detection score greater than 89).
- numHighDetections - Number of High Detections (Number of Detections detected with Detection score between 70-89).
- numMediumDetections - Number of Medium Detections (Number of Detections detected with Detection score between 40-69).
- numLowDetections - Number of Low Detections (Number of Detections detected with Detection score less than 40).
- We are capping the number of counts for Medium and Low to 2000 to avoid the score going very high.
- WtCrit, WtHigh, WtMed, WtLow are contributions from each criticality bin; current weights are 0.80, 0.15, 0.03, 0.02, respectively.
- Final ARS score will be capped to 1000.
Why can't I set up Active Directory, Microsoft Entra ID and Okta connectors?
Active Directory, Microsoft Entra ID and Okta connectors are currently available only for UAI-enabled tenants. If your tenant is inventorized by Qualys application, you cannot configure these connectors.