ETM Release 1.13
September 24, 2026
This release introduces Attack Path in Risk Management, letting you see how an attacker could chain findings across connected assets to reach your most critical ones. It also brings industry-specific threat intelligence to findings through TruLens and multiple scanner selection to TruConfirm scans.
New Feature
Trace Attack Paths to Your Critical Assets
What's New for You
You can now use the new Attack Path tab in Risk Management to see the routes an attacker could take through your environment to reach a critical asset, and the findings that make each step possible.
Prerequisite
This feature is available on request; contact Qualys Support or your Technical Account Manager (TAM) to activate it for your account.
Currently, this feature is supported for accounts with UAI subscriptions.
Risk Management now includes an Attack Path tab, next to the Risk Management tab. An attack path shows how an attacker who gains a foothold on one asset can move through a sequence of connected assets and reach a high-value target, instead of looking at each vulnerability or misconfiguration in isolation.
Individual findings rarely tell you how much risk you actually carry. A medium-severity issue on an internet-facing virtual machine can matter far more than a critical issue on an isolated asset, because it is the first step in a chain that ends at a business-critical target. Attack Path closes that gap by correlating asset relationships, exposure, and findings into a single, prioritized view of exploitable routes.
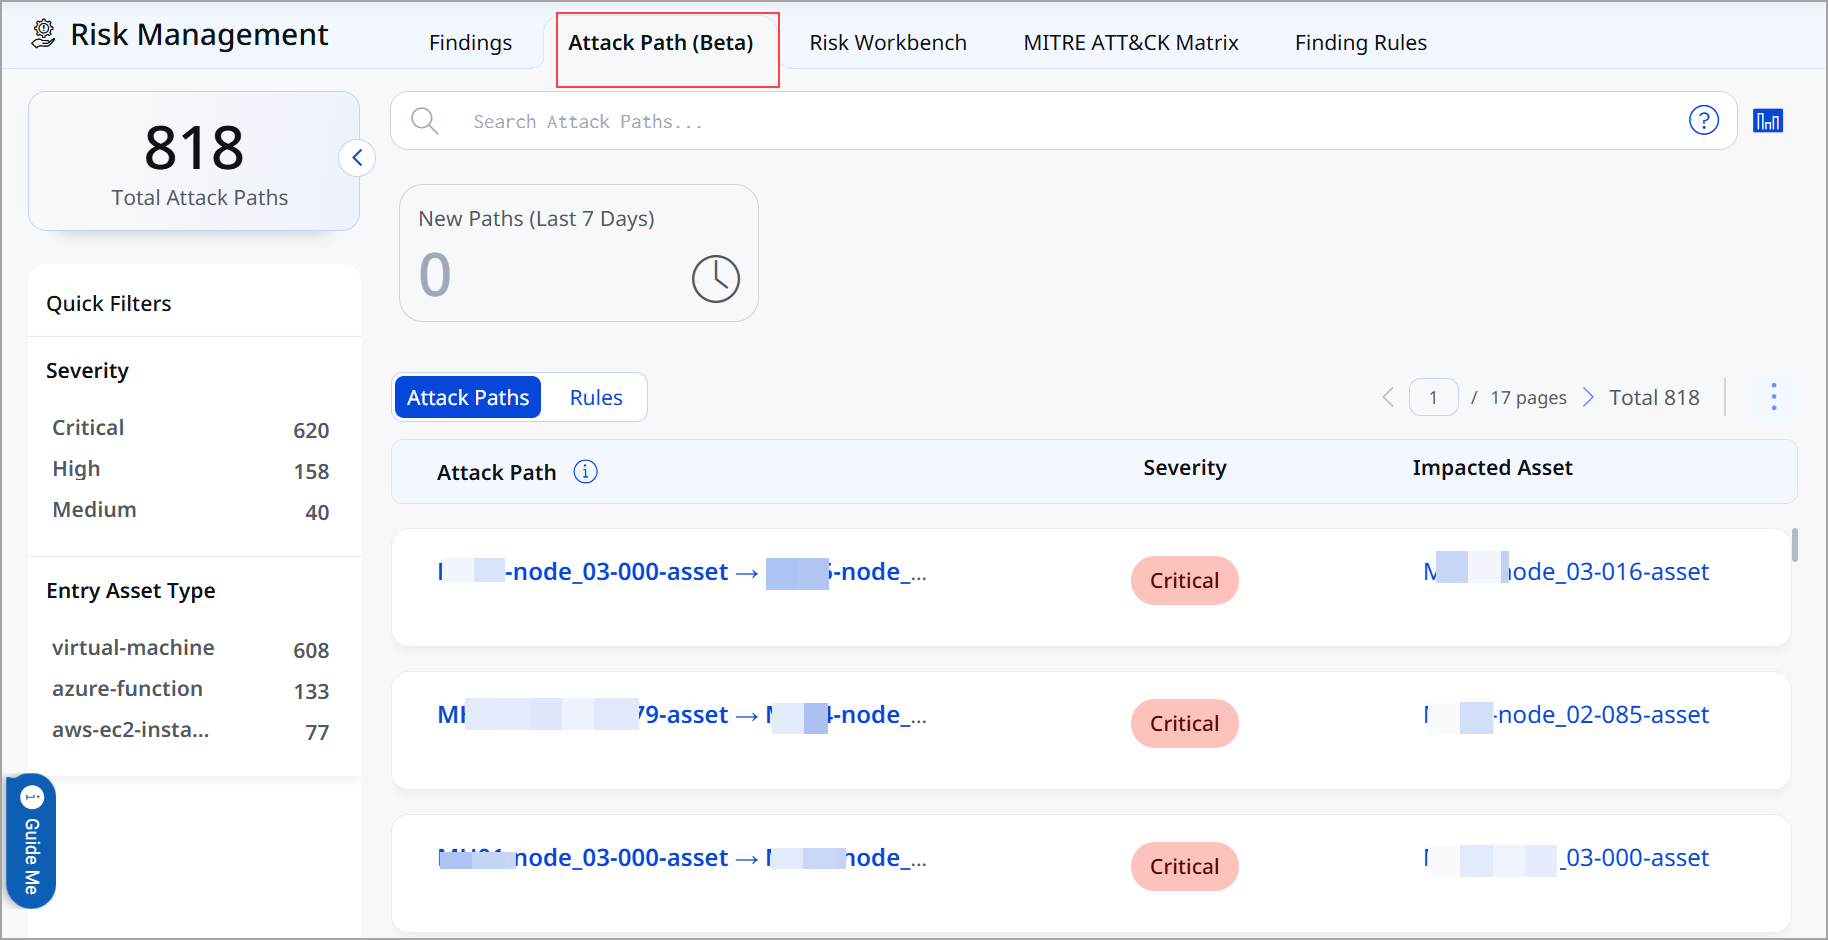
For example, an attacker might use an internet-facing virtual machine as the entry point to a business-critical asset, moving through a series of connected assets to get there. Instead of reviewing every finding on that virtual machine in isolation, you can open the attack path to see exactly which findings make each step possible, then remediate the one finding that breaks the chain and closes off the entire route to your critical asset.
The Attack Paths view lists every path detected in your account with its severity and impacted asset. Use Quick Filters to narrow the list by Severity, Entry Asset Type (such as aws-ec2-instance, virtual-machine, or azure-function), and Impact Area (such as Crown Jewel). The New Paths card shows how many attack paths were detected in the last seven days, so you can focus on what has changed recently.
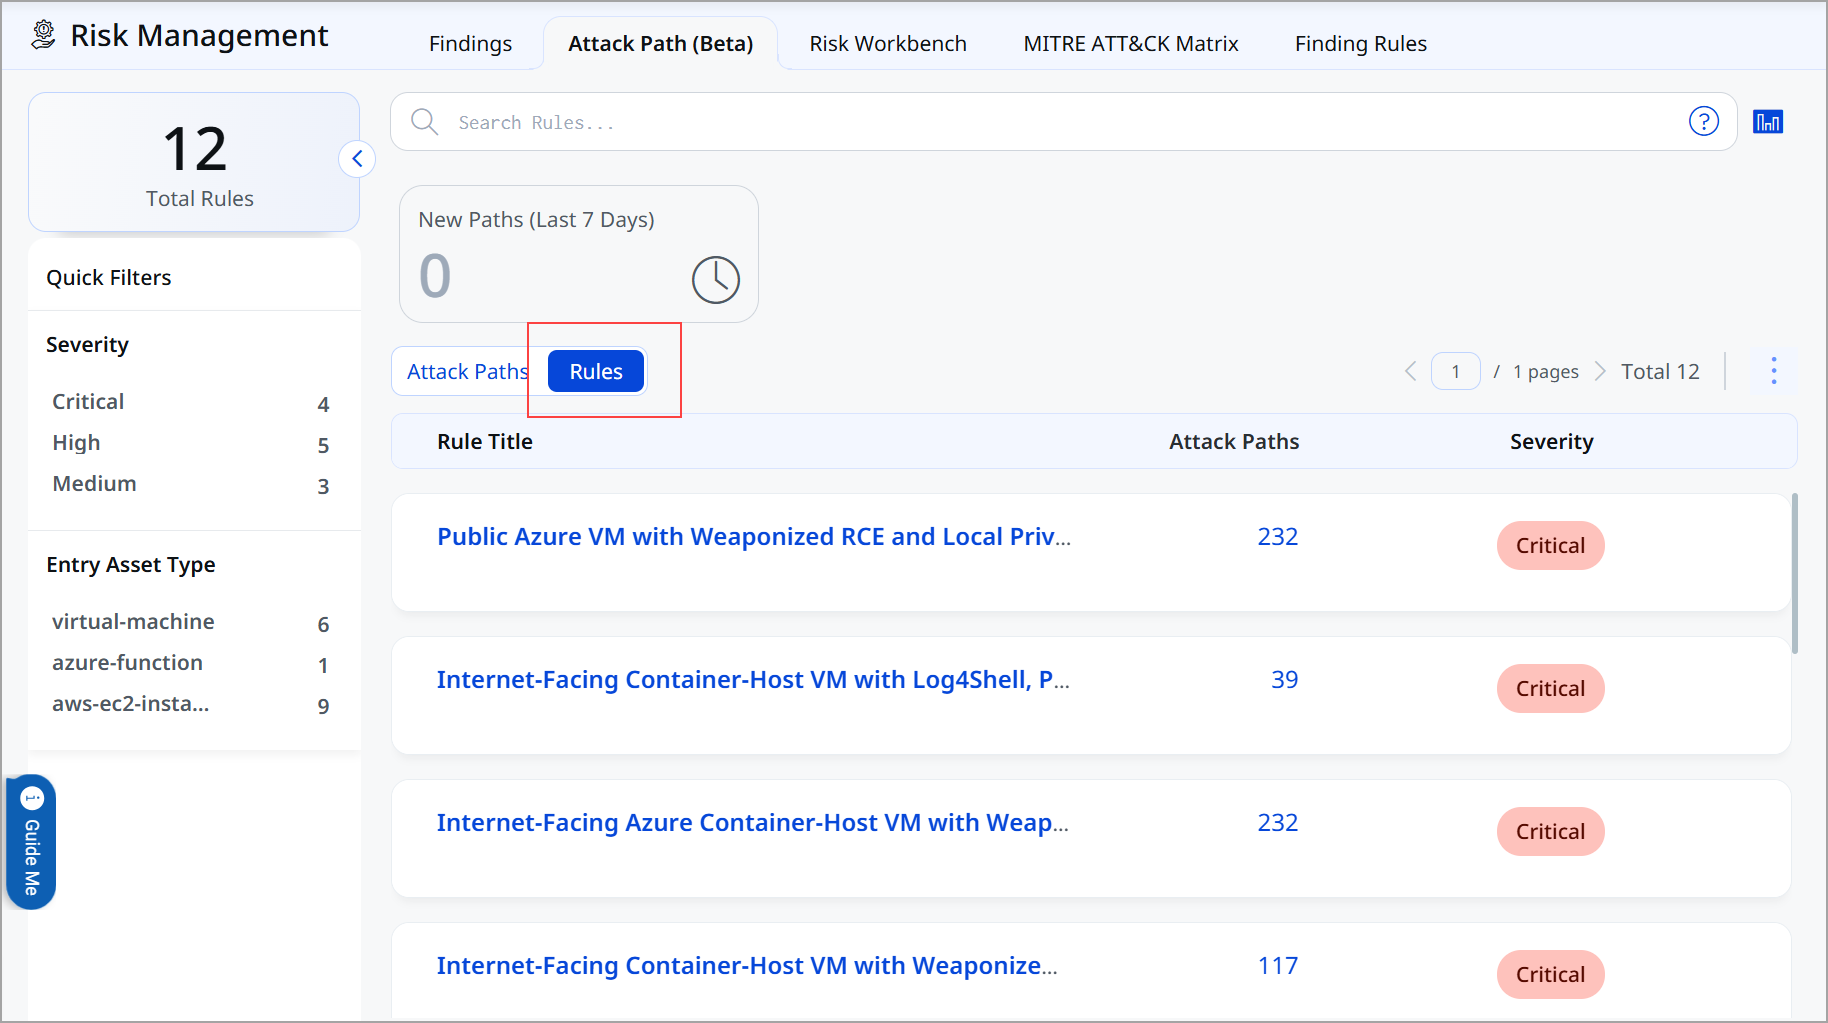
Switch to the Rules view to see the detection rules behind these paths. Rules are authored by the Qualys Threat Research team using defined criteria across assets and findings, and each rule shows the number of attack path instances it has detected in your account along with its severity. Click the count to open the matching attack paths directly.
Open a rule to see its Description, Contributing Factors (the risk dimensions across your attack surface that satisfy the rule), Rule Overview (the scope and impact of the rule), and Mitigation (recommended actions to reduce the risk), followed by the individual attack path instances detected for that rule.
The Rules view lists only the rules that are currently detected in your account, so the count you see reflects your environment rather than the full catalog.
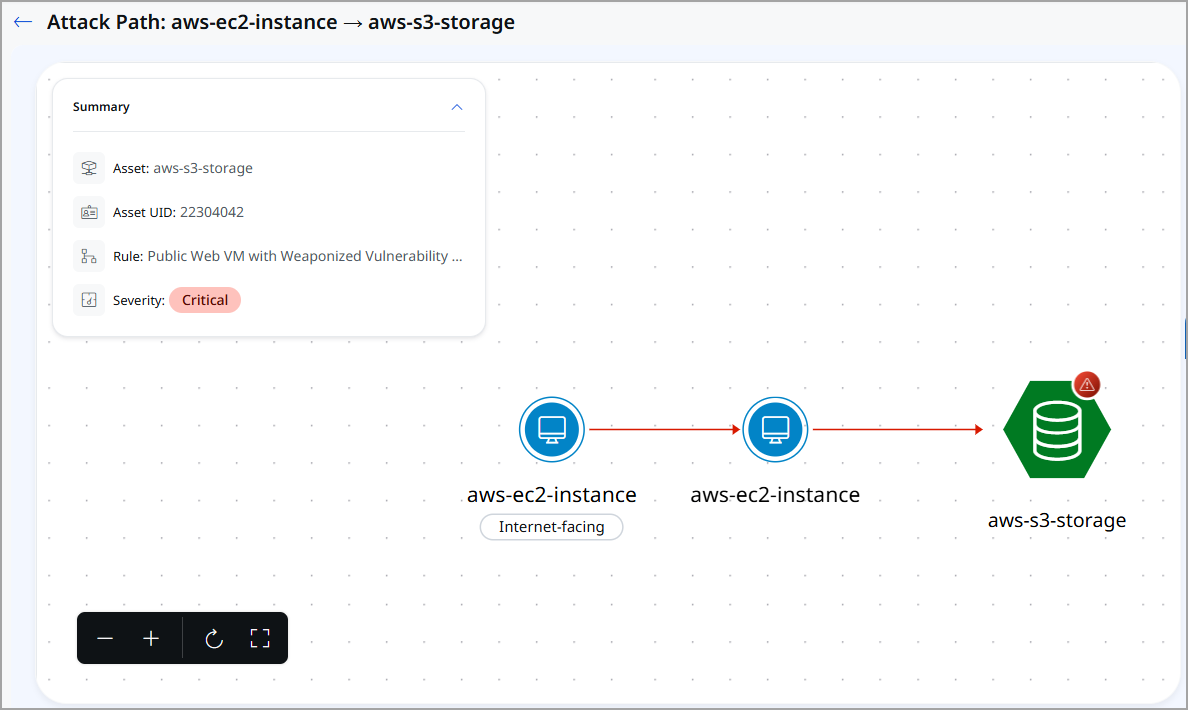
Click any attack path to open its visualization. The graph shows the entry point on the left, the final target on the right, and the nodes in between. A node whose asset carries the highest asset criticality score is marked as a Crown Jewel so you can immediately tell when a path ends at a business-critical asset.
Click a node to open its details, including the asset's TruRisk™ score, associated findings, and its other vulnerabilities grouped by severity. Click a vulnerability count to open the filtered vulnerability list in a new tab. If the same asset appears in more than one path, use the shared attack path option on the node to pivot to the Attack Paths list filtered to that asset.
Select the edge between two nodes to see the MITRE ATT&CK Tactics and Techniques associated with that step, so you can describe the movement in language your detection and response teams already use.
Attack Path is available to users with the required permissions. In this release, attack paths are presented for investigation and prioritization; remediation actions are not launched from the attack path graph.
Attack paths span both host assets, such as virtual machines and cloud compute instances, and non-host assets, such as storage, containers, and serverless functions, based on the criteria defined in each rule.
The following are the key aspects of Attack Path:
| Attack Path Visualization | See the full chain from entry point to final target, with node and edge details that explain why each step is possible. |
| Research-Backed Rules | Detect paths using rules authored by the Qualys Threat Research team, each with contributing factors, scope, impact, and recommended mitigation. |
| Crown Jewel Identification | Identify at a glance when a path terminates at a business-critical asset, so you can prioritize the paths that matter most. |
| MITRE ATT&CK Context | View the tactics and techniques associated with each step between nodes. |
| Quick Filters and Search | Narrow attack paths by severity, entry asset type, and impact area, or search attack paths and rules using QQL. |
| New Paths Tracking | Track the attack paths detected in the last seven days to stay focused on recent changes in your exposure. |
| Cross-Path Pivoting | Investigate an asset that appears in multiple attack paths by pivoting from the node to the filtered attack path list. |
Attack Path is best suited for Security Operations, Vulnerability Management, and Cloud Security teams who need to understand exploitable routes to critical assets rather than isolated findings, and for security leaders who need to explain exposure in terms of business impact.
For more information, refer to ETM Online Help.
New Feature
Prioritize Remediation Using CISA BOD 26-04
What's New for You
You can now prioritize remediation in ETM the way CISA Binding Operational Directive (BOD) 26-04 requires, by asset exposure, CISA Known Exploited Vulnerabilities (KEV) status, exploit automation, and technical impact, rather than by severity score alone.
Prerequisite
CISA BOD 26-04 support is a subscription-level feature. Contact Qualys Support or your Technical Account Manager (TAM) to have it enabled for your subscription.
Two New Risk Factors in Your Findings
ETM now supports two CISA-published risk factors alongside your existing finding data:
- Technical Impact: Whether exploitation gives an adversary Total Control, Partial Control, or an Unknown level of control over the affected asset.
- Automatable: Whether an adversary can automate every step needed to exploit the vulnerability, expressed as Yes or No.
Asset exposure and CISA KEV status already exist in ETM.
Track Remediation SLAs
ETM calculates a remediation SLA for each finding from its risk factors. An SLA profile is a named set of remediation rules that defines how many days a finding is allowed before remediation is due, and the action it requires, either Remediate or Forensic Triage. Each finding is assigned the SLA profile that matches its risk factors, and you can search findings by the assigned profile name using finding.remediationSla.profile.
The Technical Impact and Automatable columns are available on the Findings listing, the TruLens listing, and the KnowledgeBase. Both columns are hidden by default. To display them, click Settings > Columns, and then select the checkboxes.
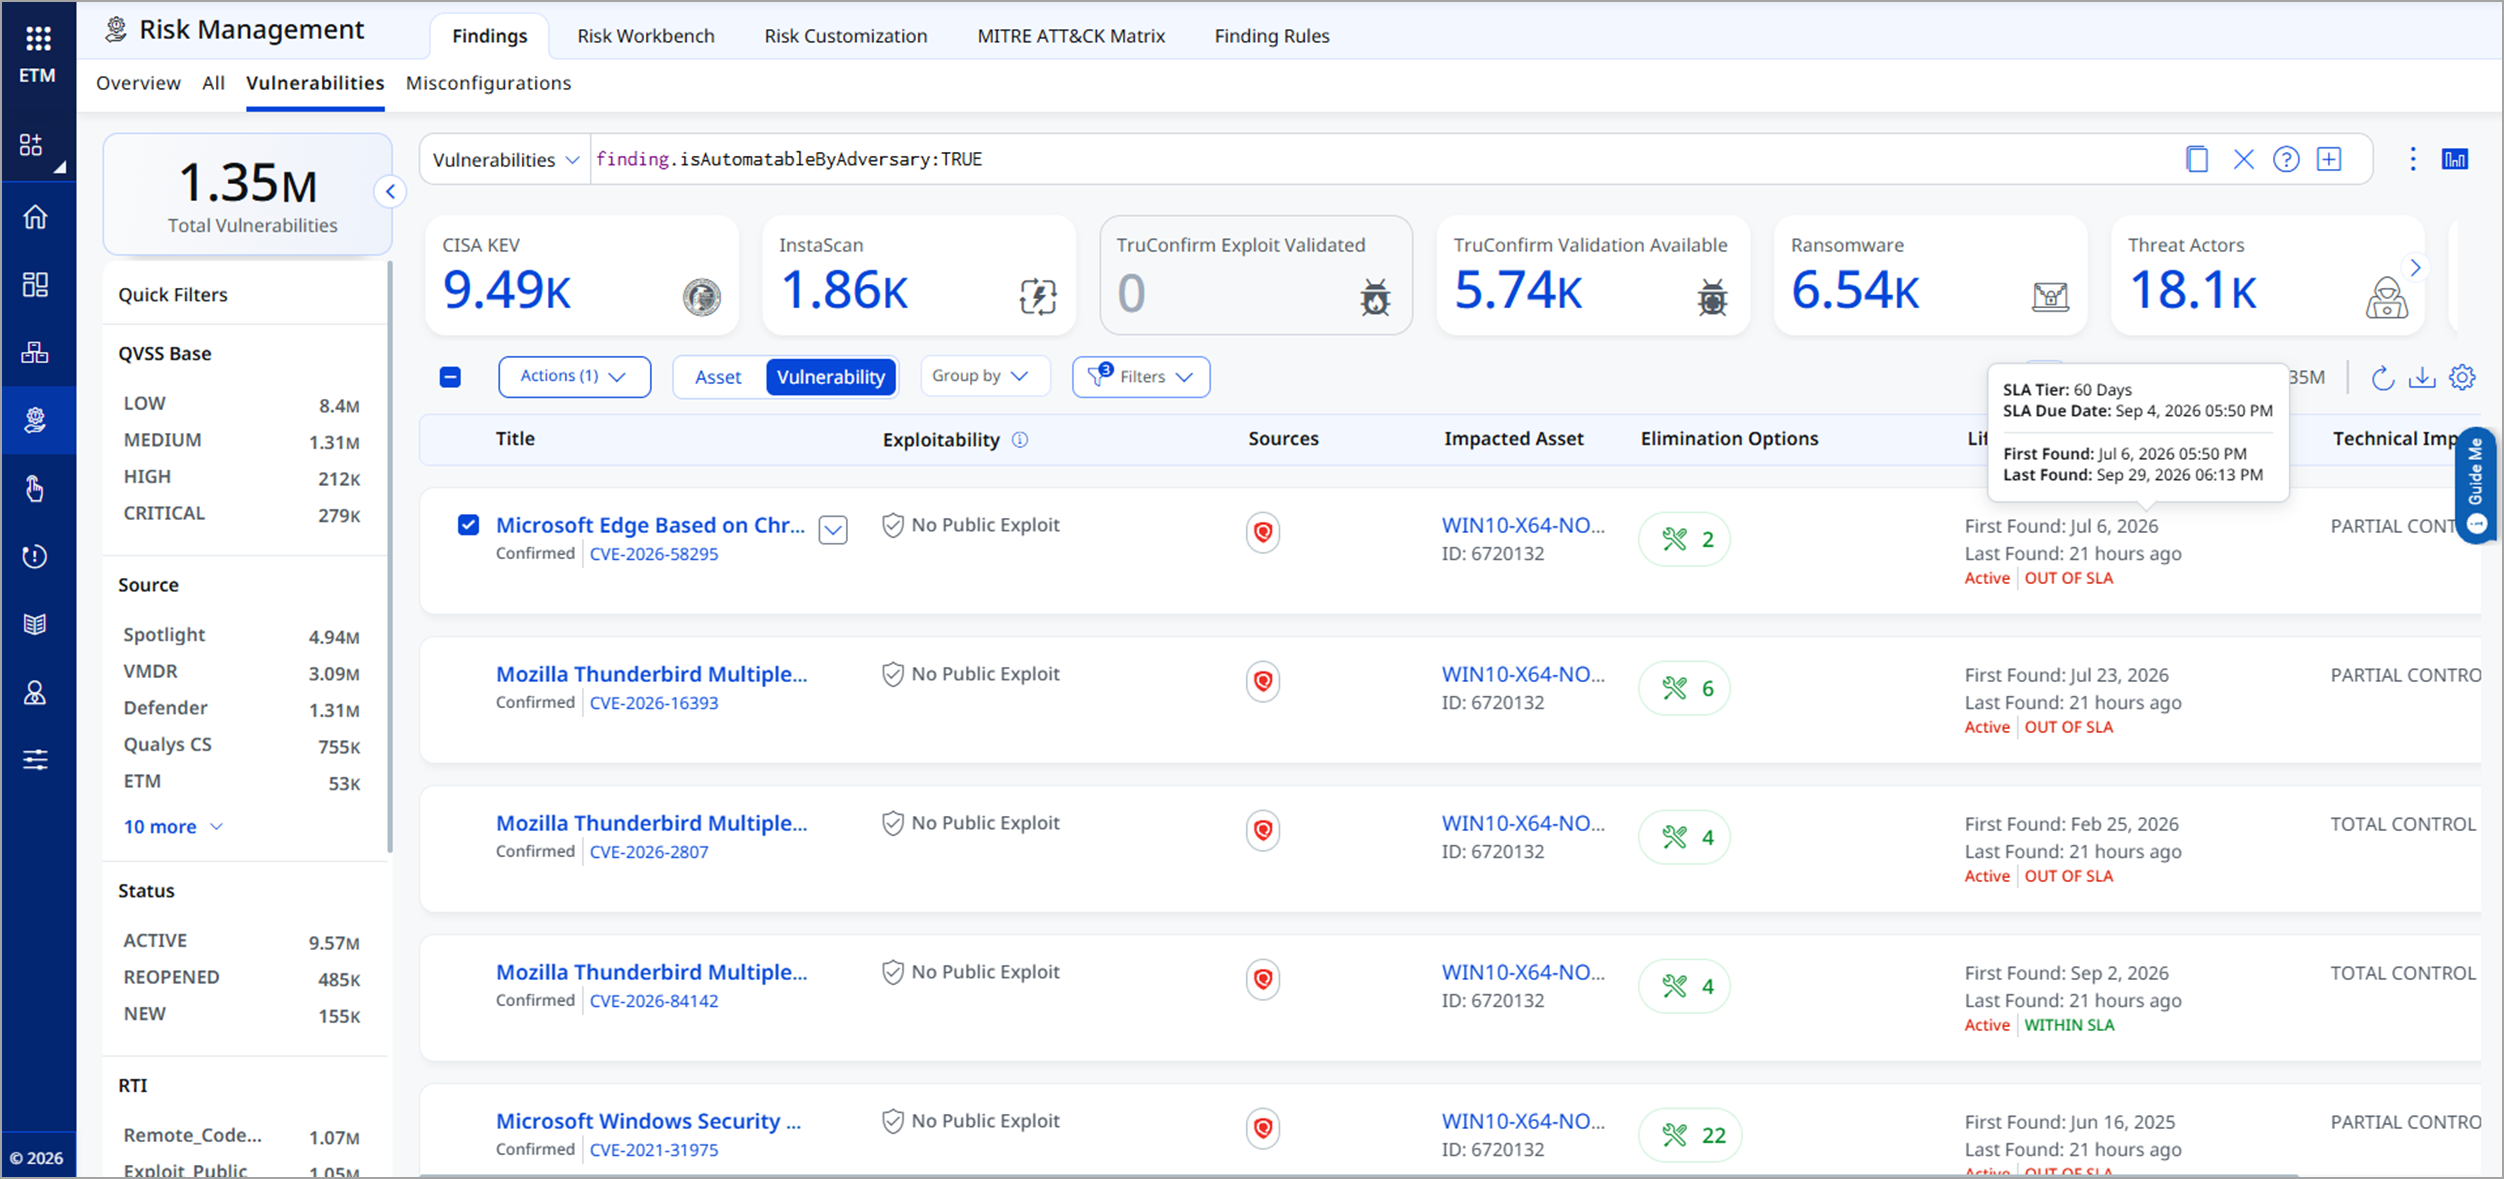
SLA Tier in the Lifecycle Tooltip
The existing Lifecycle column tooltip on the Findings listing now shows the SLA Tier, the SLA days, and the calculated SLA due date in addition to First Found and Last Found.
Dashboard Widgets for CISA BOD 26-04 Tokens
Build count, bar, table, pie, and trend widgets on the CISA BOD 26-04 tokens. Group a bar, table, or pie widget by Technical Impact, Automatable, Remediation SLA, or SLA Status. To know more about tokens, refer to CISA BOD 26-04 Tokens.
To learn more about the feature, refer to the CISA BOD 26-04 Overview.
To view, search, and filter CISA BOD 26-04 Attributes for Findings, refer to CISA BOD 26-04 Attributes.
Enhancement
TruLens Enhancements
What Changed For You
You can now use TruLens to access threat intelligence specific to your industry. This includes information about trending CVEs (Common Vulnerabilities and Exposures) and threat actors relevant to your sector. You can check the status of threat actors, find out where CVEs are discovered, and see counts of risks linked to MITRE ATT&CK techniques. This way, the CVEs and threats you focus on are directly relevant to you, supporting CISA BOD 26-04.
Prerequisite
This feature is available on request; contact Qualys Support or your Technical Account Manager (TAM) to activate it for your account.
Trending CVEs for Your Industry
What Changed For You
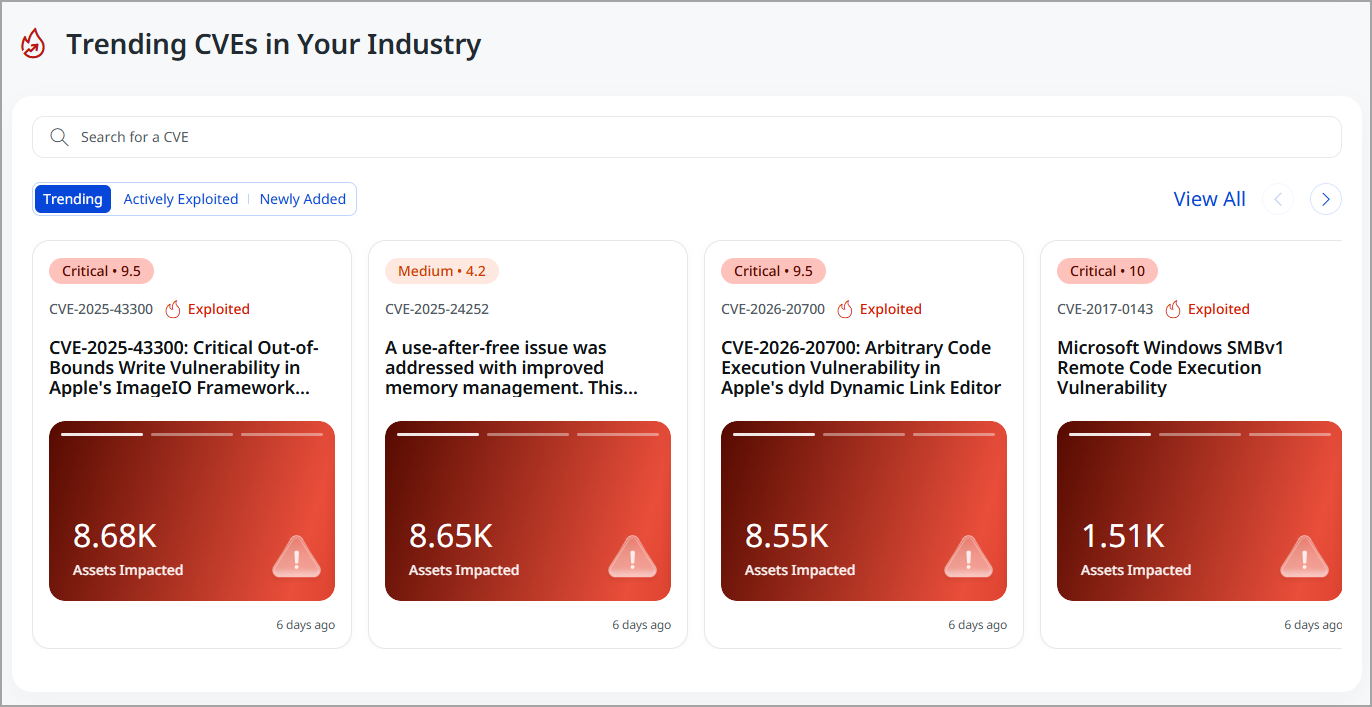
You can now see trending CVEs for your own industry instead of a generic trending list, so the threats you review first are the ones affecting organizations like yours.
The trending CVE list on the Overview page is now scoped to the industry configured in your subscription profile. The section is labeled Trending CVEs in your industry, replacing the earlier environment-based label, and the underlying list is filtered on your industry automatically. No configuration is required.
When you click View All, the industry context carries through to the CVE list in the KnowledgeBase, including the counts and pivots, so the drill-down stays consistent with what you saw on the Overview page. If you open the KnowledgeBase directly instead of navigating from the Overview page, the list is not scoped to your industry.
The trending criteria have also been tightened. A CVE now appears in the trending list only when it has at least one trending industry associated with it and its last trending date falls within the previous 30 days. This removes CVEs that were previously listed on the strength of a trend date alone, without any industry context behind them.
On the CVE details page, the Affected Industries section is renamed to Industries and now lists the trending industries for that CVE. Industries that are currently trending are marked with a trend indicator, and your own industry is highlighted so you can tell at a glance whether the CVE is trending in your sector.
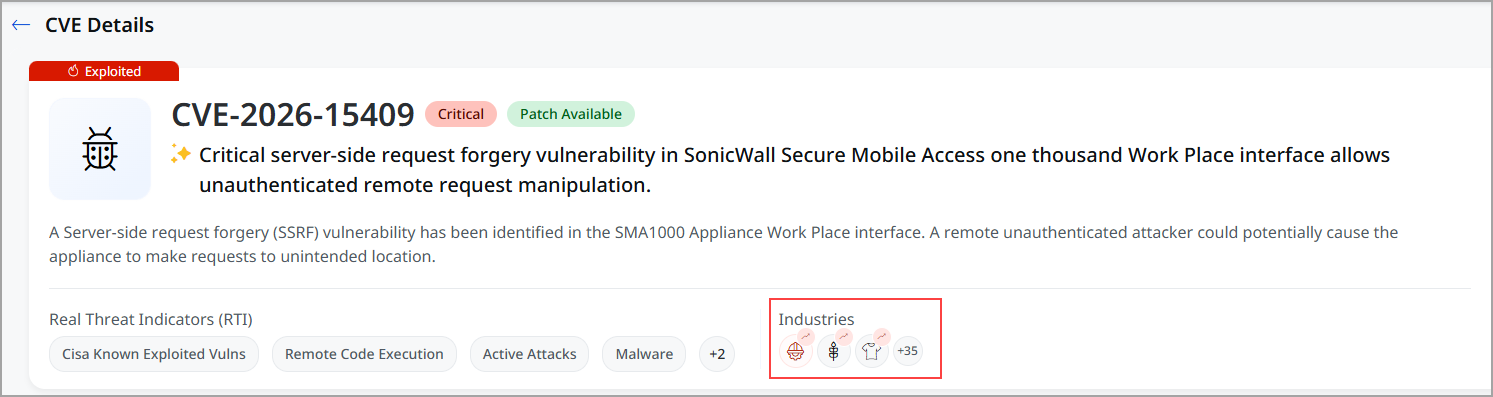
This corrects earlier behavior, where the section was labeled as Affected Industries but the underlying data described impacted and trending industries rather than confirmed affected ones.
The CVE listing also supports searching by industry using QQL, with auto-suggestions for all supported industries, so you do not have to guess the exact industry string. The search applies across the tabs of the CVE page.
The following are the key aspects of trending CVEs by industry:
| Industry-Scoped Trending | See trending CVEs for the industry in your subscription profile, applied automatically on the Overview page. |
| Consistent Drill-Down | Carry the industry context from the Overview page into the CVE list, counts, and pivots when you click View All. |
| Industries on CVE Details | Review the trending industries for a CVE, with your own industry highlighted. |
| Refined Trending Criteria | Include a CVE in the trending list only when it has a trending industry and has trended within the last 30 days. |
| QQL Search by Industry | Filter the CVE list by industry using QQL with auto-suggestions for supported industries. |
Trending Threat Actors Targeting Your Industry
What Changed For You
You can now see the threat actors trending against your industry, and switch between trending and all threat actors from a new set of tabs in TruLens.
The Overview page now shows Trending Threat Actors Targeting Your Industry, using the industry from your subscription profile. The summary returns the total and impacted threat actor counts for that industry, so the card reflects adversaries currently active against your sector rather than a general list.
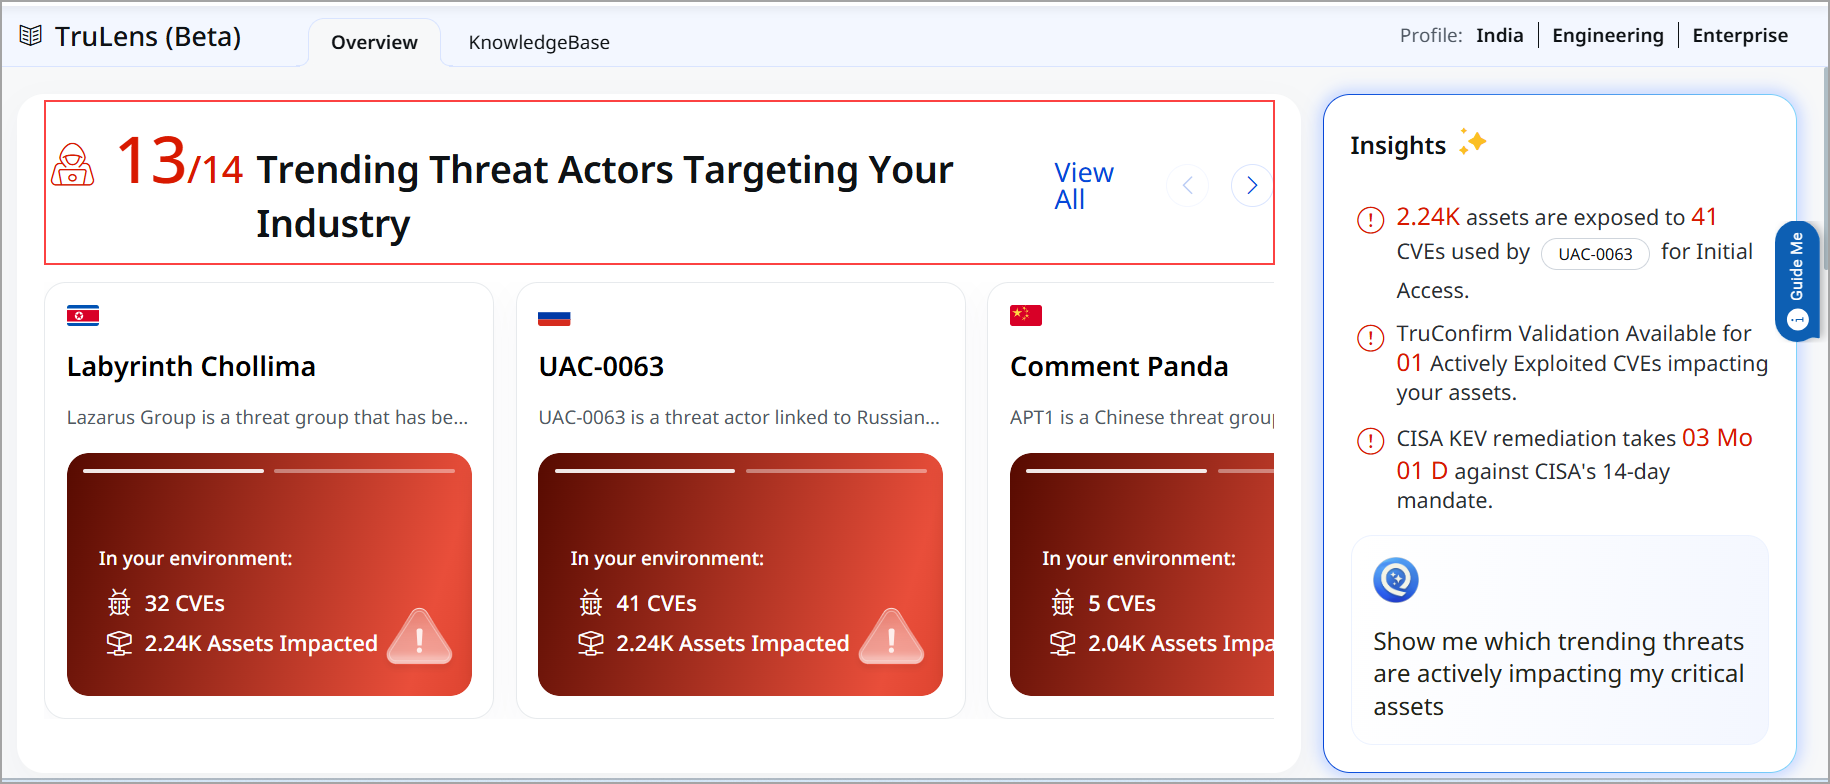
The Threat Actors page in the KnowledgeBase now has two tabs: Trending and All. The Trending tab lists only threat actors that have at least one trending industry, while All shows the full list. Counts and pivots follow the selected tab, so the numbers you see always match the list in view.
When you click View All from the Overview page, the industry filter is applied for you. When you open the Threat Actors page directly from the KnowledgeBase, you land on the All tab.
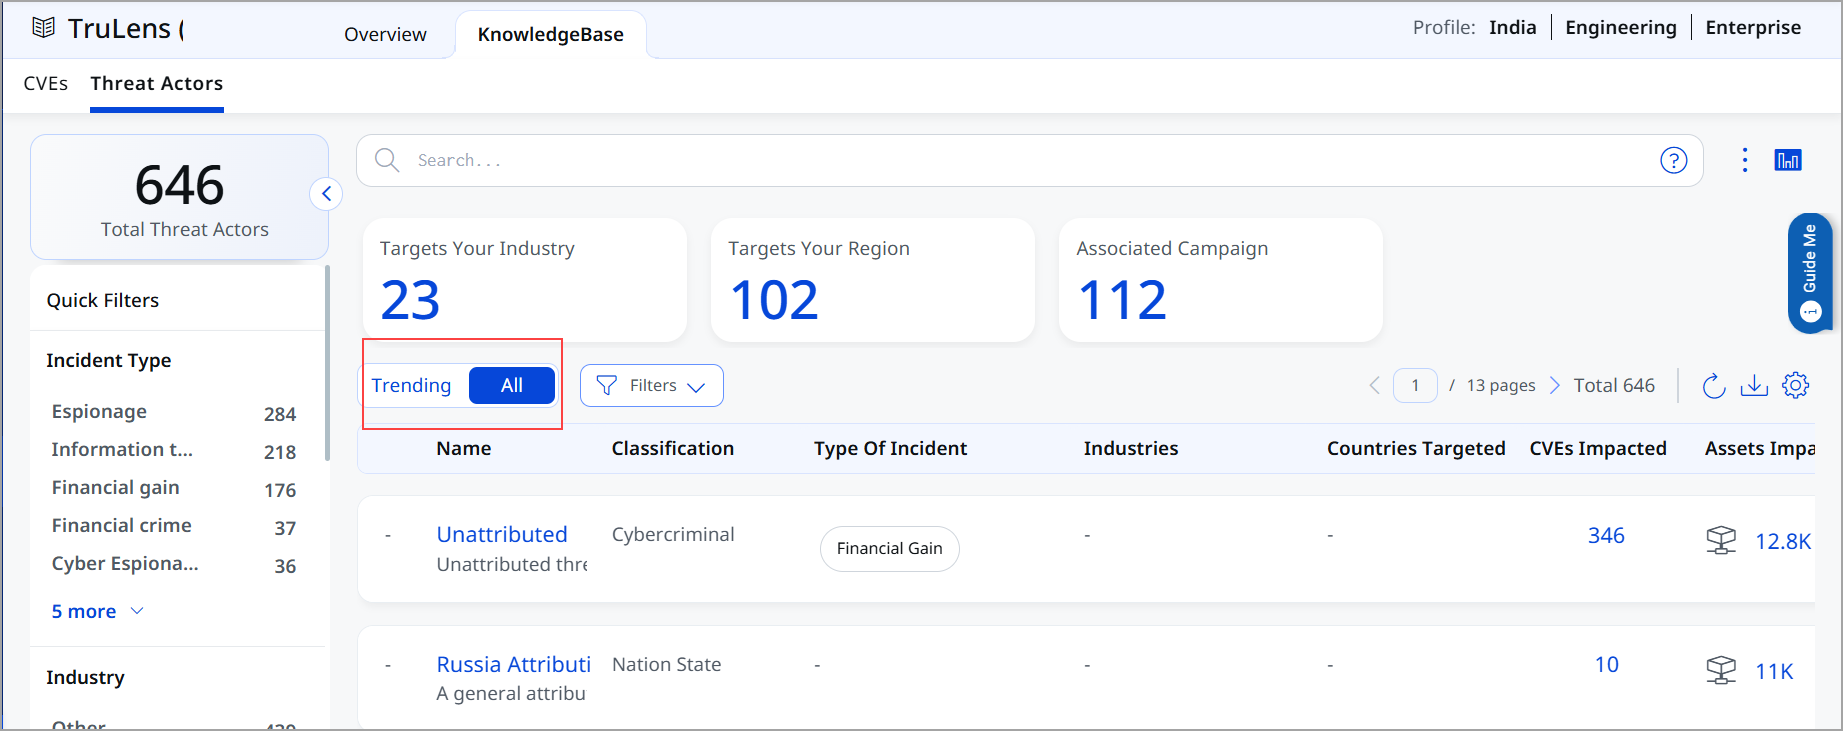
If no threat actor in your account has a trending industry associated with it, the Trending tab returns an empty list.
QQL support is also improved on this page. You can search threat actors by trending industry, and the existing targeted-industry search now offers auto-suggestions for the supported industries instead of requiring a free-text value, which avoids empty results caused by an unrecognized industry string.
The following are the key aspects of trending threat actors by industry:
| Industry-Scoped Threat Actors | See the threat actors trending against your industry, with total and impacted counts, on the Overview page. |
| Trending and All Tabs | Switch between trending threat actors and the complete list, with counts and pivots following your selection. |
| Search by Industry | Filter threat actors by trending industry or targeted industry using QQL, with auto-suggestions for both. |
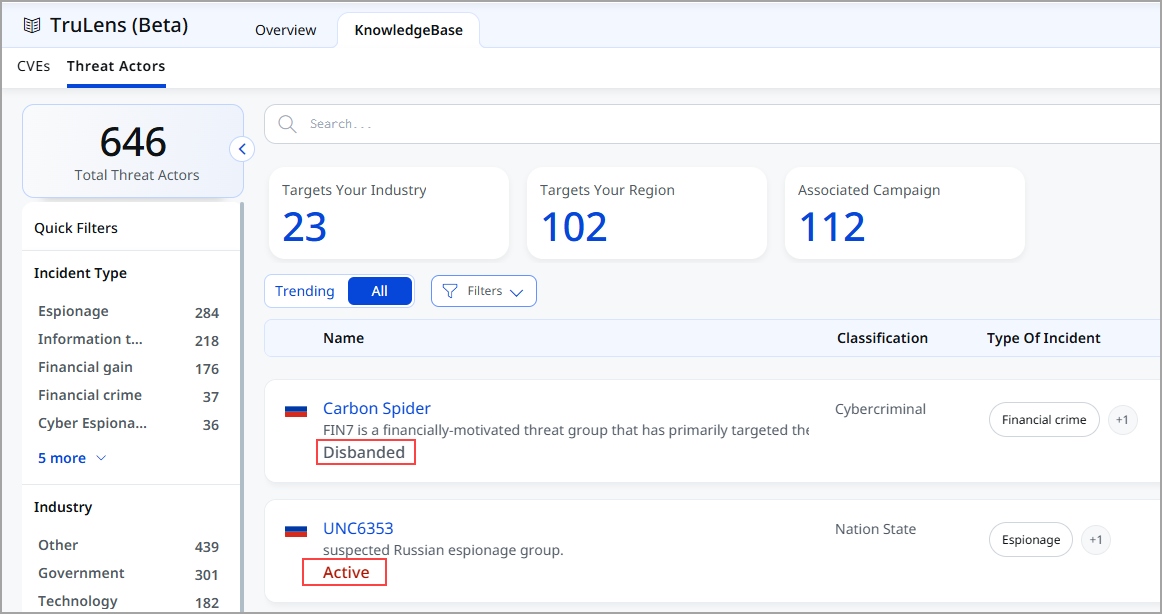
View Threat Actor Status
What Changed For You
You can now see whether a threat actor is active, dormant, or disbanded directly in the threat actor list and details, and filter on that status.
Threat Actor Status is now shown on the Threat Actors listing page and on the threat actor details page. The supported statuses are Active, Dormant, and Disbanded, which lets you discount adversaries that are no longer operating and concentrate your analysis on the ones that are.
Status is displayed only when it is available for a threat actor. When no status is reported, the status section is not shown on the details page and the column is left blank in the listing, so an absent status is never presented as a definite state.
You can also search threat actors by status using QQL, with the supported status values offered as auto-suggestions.
Visibility of CVE Source
What Changed For You
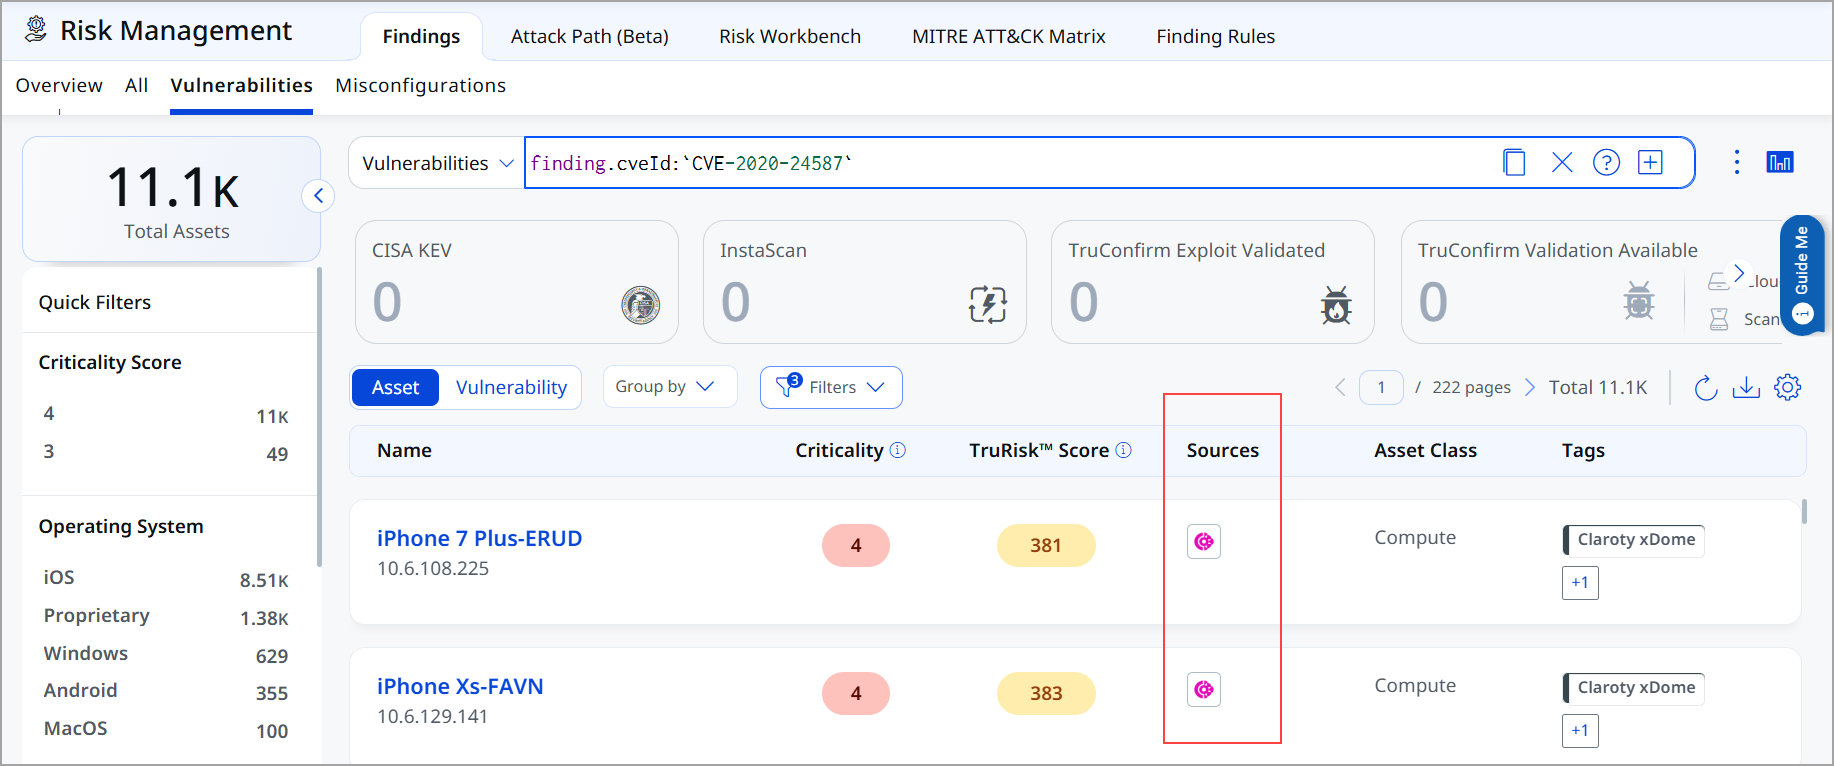
You can now see where a CVE was discovered, shown as a source indicator on the CVE list and CVE details page. QQL search is supported on the CVE listing, and the CVE Details page includes this CVE source field.
CVE listings now show where the information about each vulnerability came from. This is indicated by a source icon on both the listing and the details page. This helps you quickly see the origin of the information, which is important when deciding how much to trust a specific detection. The CVE listing updates with new threat intelligence data instead of relying on a set list, so new sources are included as they become available. If a source does not have a dedicated icon yet, a default icon still shows the source.
You can search the CVE list by source using QQL. The source is entered as a text value.
Risk Finding Counts in the MITRE ATT&CK Tab
What Changed For You
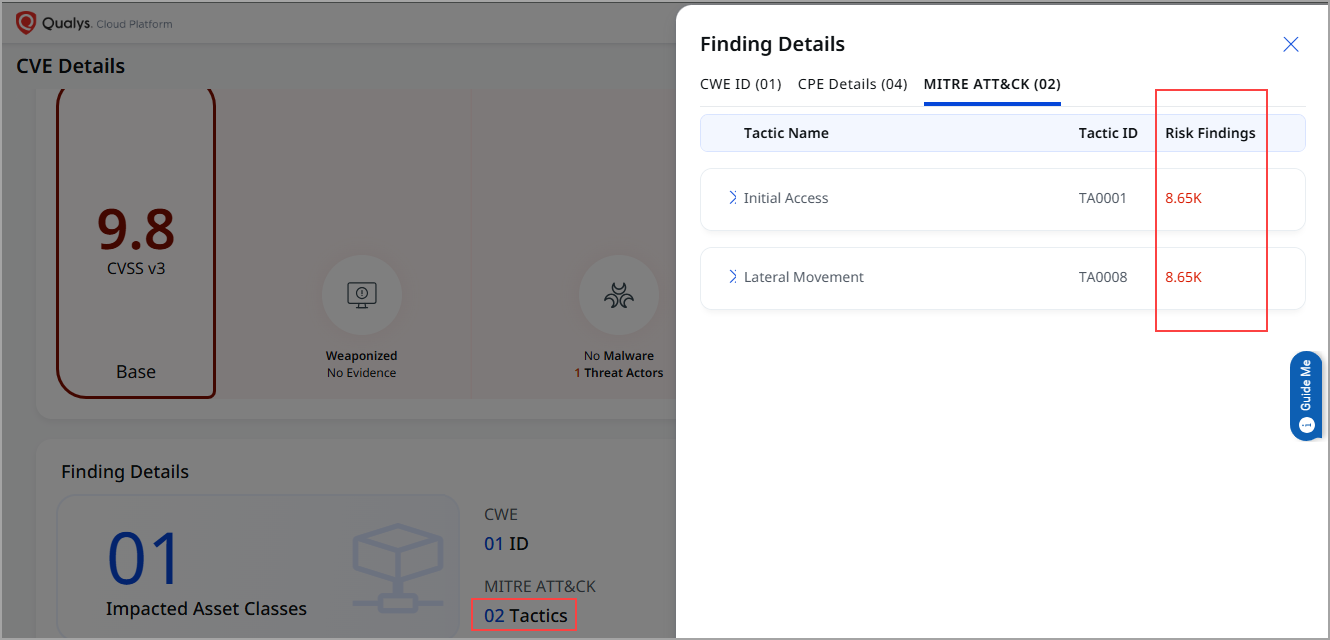
You can now see how many risk findings in your environment map to each MITRE ATT&CK Tactic and Technique for a CVE, and jump straight to those findings.
The MITRE ATT&CK tab on the CVE details page now includes a Risk Findings column. Counts are shown at the tactic level and for each technique within that tactic, connecting adversary behavior for a CVE to what is actually detected in your environment.
Click a technique-level count to open the corresponding risk findings, filtered by that Tactic and Technique, so you can move from the technique to the affected assets without building the query yourself. Tactic-level counts are shown for context and are not clickable.
CVE Aliases and Clickable Malware Entries
What Changed For You
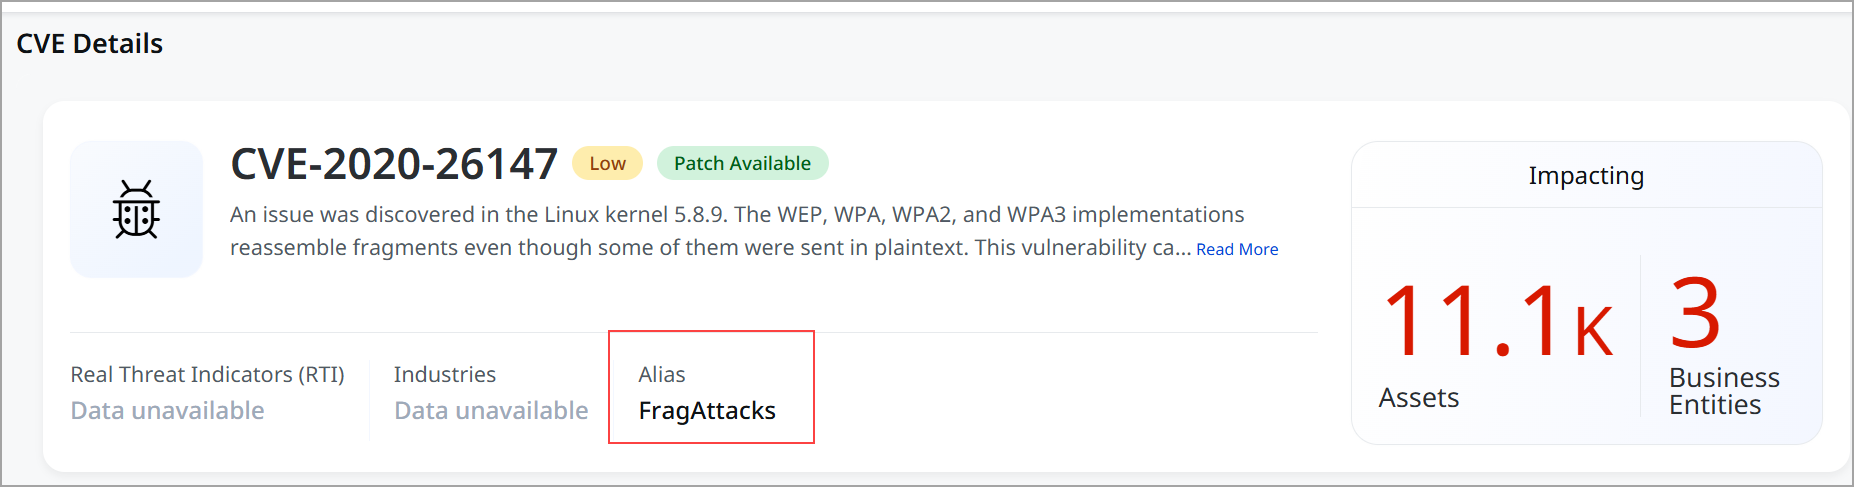
You can now search CVEs by their alias and move from malware on the CVE list straight to the related risk findings.
CVE aliases are now shown on the CVE details page, so a CVE that is publicly known by a name rather than its identifier is easier to recognize. When no alias is available for a CVE, the section is hidden. The CVE listing supports searching by alias using QQL, and the filter is applied to the list, counts, and pivots.
Malware entries on the CVE listing page are now clickable and take you to the associated risk findings, matching the behavior already available on the CVE details page.
The following are the key aspects of the CVE KnowledgeBase usability enhancements:
| CVE Aliases | View the alias for a CVE on the details page and search the CVE list by alias using QQL. |
| Malware Navigation | Navigate from malware on the CVE listing page to the related risk findings. |
For more information, refer to ETM Online Help.
CISA BOD 26-04 Risk Factors in TruLens
What Changed For You
You can now use the CISA BOD 26-04 tokens in TruLens search, so you can narrow the CVE list by technical impact, automatability, and remediation SLA without leaving the TruLens tab.
TruLens now supports the Qualys Query Language (QQL) tokens introduced for CISA BOD 26-04 support. Use them on the CVEs tab to build the same directive-aligned worklists you build on the Findings listing.
For the full token list and examples, see New Tokens for TruLens Tab.
Identify Vulnerabilities Qualys Can Mitigate
What Changed For You
You can now search TruLens for vulnerabilities that Qualys can mitigate for you, and for the type of mitigation applied, so you can separate what Qualys already covers from what your teams still need to remediate.
Mitigation is different from remediation. Remediation fixes the underlying vulnerability, typically by patching it. Mitigation reduces the risk of exploitation using a compensating control such as a virtual patch or a WAF rule — delivered through Qualys TruRisk Eliminate, without changing the vulnerable software itself.
You can now filter the TruLens CVE list down to vulnerabilities Qualys can mitigate, so your remediation worklists reflect only the issues that still need action from your side.
For the full token list and examples, see Tokens for TruLens Tab.
See Which CVEs TruConfirm Can Assess
What Changed For You
You can now see which CVEs can actually be assessed by TruConfirm, and whether that assessment runs through Cloud Agent or a scanner, so you know before you plan an assessment which vulnerabilities are covered by the collector you have deployed.
TruConfirm checks if a reported vulnerability can be exploited on an asset. However, not every CVE can be assessed, and some may need a specific collection method. Previously, you only discovered this when you tried to do the assessment.
TruLens now records TruConfirm applicability at the CVE level. On the TruLens > KnowledgeBase > CVEs tab, two new tokens tell you whether a TruConfirm assessment can be launched by Cloud Agent for a given CVE, and whether it can be initiated by a scanner. Because the two are evaluated separately, you can also identify CVEs that only one collection method supports.
Use these tokens to scope an assessment to the CVEs your deployment can actually cover, or to find gaps where a CVE can be evaluated only by a method you have not rolled out.
For the full token list and examples, see Tokens for TruLens Tab.
View CWE, CPE, and MITRE ATT&CK Details Without Leaving the Page
What Changed For You
You can now open CWE, CPE, and MITRE ATT&CK details in a pop-up from the CVE Details page instead of navigating away, so you can review everything related to a CVE without losing your place.
The Finding Details section now includes the following fields:
- CWE (Common Weakness Enumeration) ID
- CPE (Common Platform Enumeration) ID
- MITRE ATT&CK Tactic
All fields displaying counts are now clickable. Clicking a count opens a pop-up view with the related details, so you can move between CVE-related entities without leaving the page. For example, clicking CWE displays the CWE Name, CWE ID, Language, and Reference URL.
Navigate to Risk Management tab > Findings > Vulnerabilities, and refer to the Finding Details section.
Token
New Tokens for TruLens Tab
The following tokens are introduced in this release, along with tokens to build CISA BOD 26-04 worklists.
| Token | Sub Tab | Description |
|---|---|---|
|
finding.truConfirm.isCloudAgentApplicable |
TruLens > KnowledgeBase > CVEs |
Select TRUE or FALSE to search findings based on whether a TruConfirm assessment can be launched by Cloud Agent for the given CVE ID.
|
|
finding.truConfirm.isScannerApplicable |
TruLens > KnowledgeBase > CVEs |
Show findings where the TruConfirm assessment can be initiated by a scanner
|
|
finding.isQualysMitigable |
TruLens > KnowledgeBase > CVEs |
Show vulnerabilities that can be mitigated by Qualys
|
|
finding.qualysMitigableType |
TruLens > KnowledgeBase > CVEs |
Show vulnerabilities by the type of mitigation Qualys applies
|
|
finding.technicalImpact |
TruLens > KnowledgeBase > CVEs |
Select a technical impact level (TOTAL CONTROL, PARTIAL CONTROL, or UNKNOWN) to search findings based on the level of control an attacker could gain if the vulnerability is successfully exploited. Select from values in the drop-down menu. Example Show findings where an attacker could gain total control of the asset
|
|
finding.isAutomatableByAdversary |
TruLens > KnowledgeBase > CVEs |
Select TRUE or FALSE to search findings based on whether the vulnerability can be automatically exploited by an adversary without manual intervention. Example Show findings that can be automated by an adversary
|
Enhancement
Select Multiple Scanners for TruConfirm Scans
What Changed For You
You can now select multiple internal scanner appliances to perform a TruConfirm scan. The available scanner appliances are based on the network you select.
Prerequisite
This feature is available on request; contact Qualys Support or your Technical Account Manager (TAM) to activate it for your account.
When you launch a TruConfirm scan with Scanner Appliance as the exploit validation source, you can now select a Network and then choose the scanner appliance type:
- Internal: search for and select multiple scanner appliances associated with the selected network.
- External: TruConfirm scan runs against the default network automatically, with no additional selection required.
The scanner appliances you select are shown in the:
- Review & Confirm step before you launch the scan
- Assessment Details page
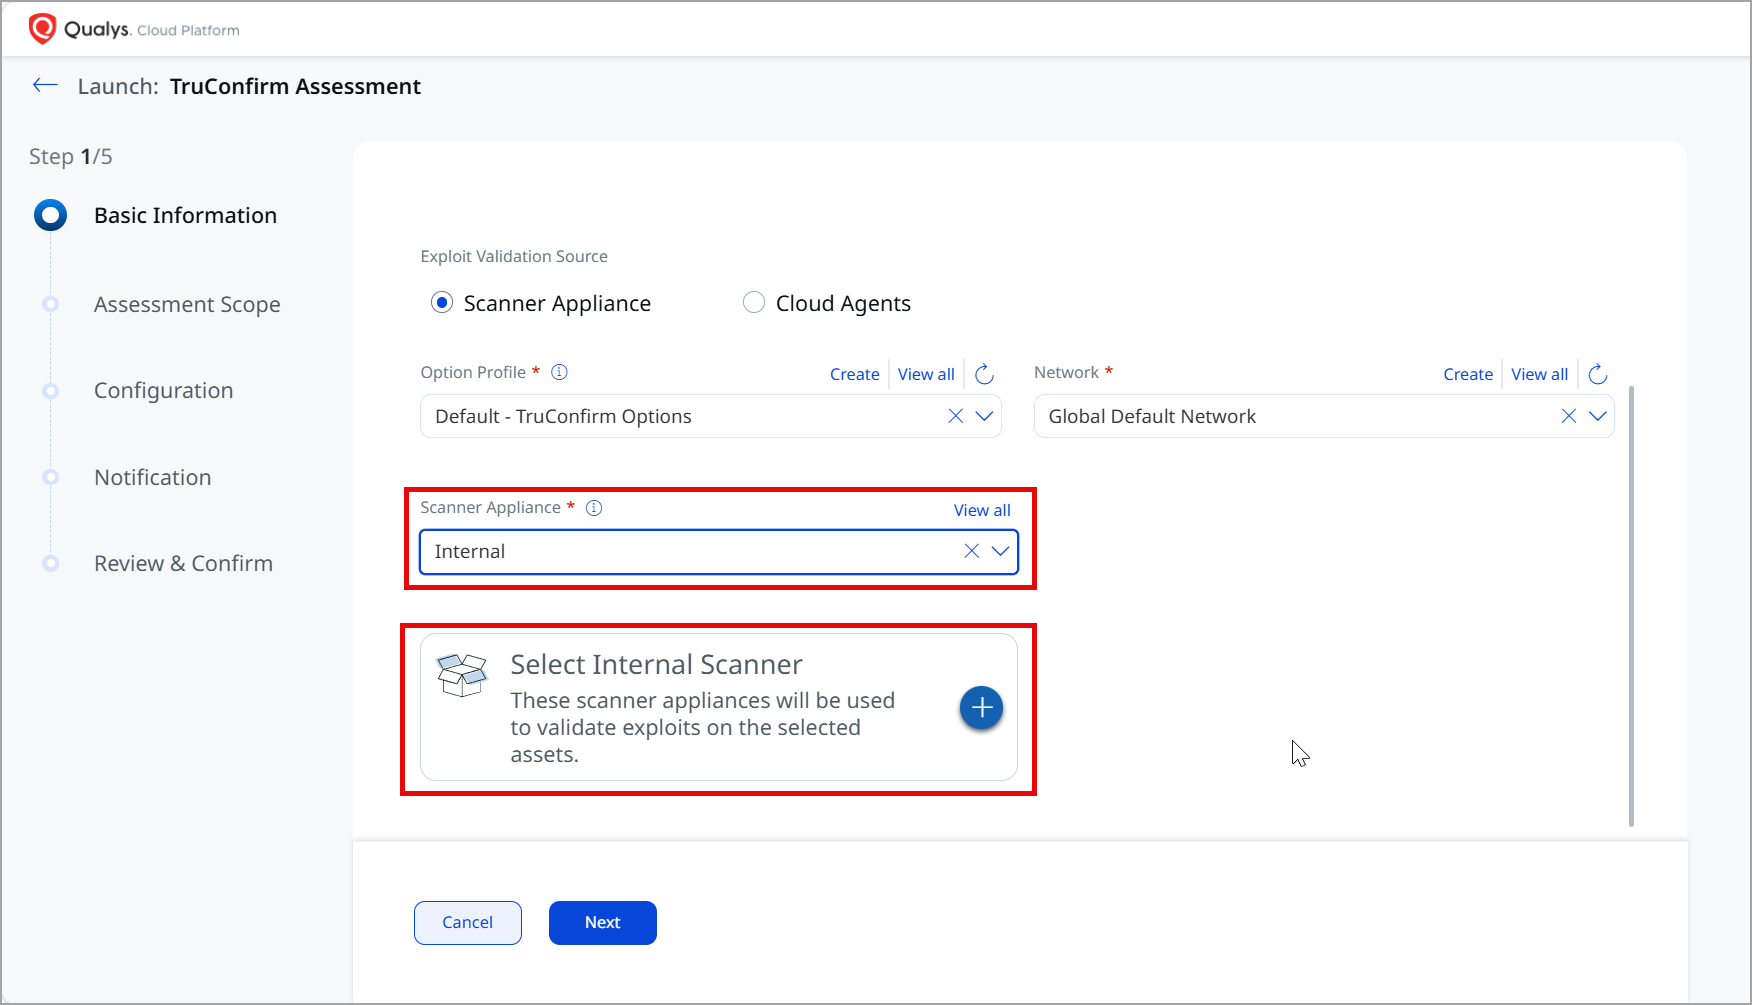
If networks are not available for your subscription, the Network field is not displayed, and the assessment runs against the Global Default Network.
The following are the key aspects of selecting multiple scanners for TruConfirm scans:
- Cover More Assets in One Scan: Validate assets behind different internal scanner appliances in a single assessment instead of running separate scans for each appliance.
- Choose Scanners Based on the Selected Network: The appliance list is filtered based on the network you select, so you only see appliances that can reach the assets in that network.
- Keep a Record of Scanner Usage: The scanner type and the appliances used are shown before you launch and are retained in the scan and schedule details afterward.
For more information, refer to ETM Online Help.
Token
New Tokens for Attack Path
You can use the following tokens to search attack paths and rules in the Attack Path tab:
| Token | Sub Tab | Description |
|---|---|---|
|
asset.uid |
Risk Management > Attack Path |
Use this token to search for host and non-host assets using their asset UID.
|
|
asset.name |
Risk Management > Attack Path |
Use quotes or backticks within values to find the asset with the specified asset name.
|
|
asset.type |
Risk Management > Attack Path |
Use this token to find assets of a certain type. Select from the asset types in the drop-down menu.
|
|
asset.tag.name |
Risk Management > Attack Path |
Use a text value to find assets with the specified tag.
|
|
finding.vendorName |
Risk Management > Attack Path |
Select a detection source (Wiz, Qualys, Microsoft) to search findings from the specified source. Select from the names in the drop-down menu.
|
|
finding.cveId |
Risk Management > Attack Path |
Use a text value to search for findings based on the CVE ID of the vulnerability.
|
|
finding.truConfirm.status |
Risk Management > Attack Path |
Select a TruConfirm status to filter findings based on their TruConfirm assessment results. Choose a value from the drop-down list.
|
|
attackPath.severity |
Risk Management > Attack Path |
Use this token to search attack paths by their severity. Select a value from the drop-down menu.
|
|
attackPath.length |
Risk Management > Attack Path |
Use an integer value to search attack paths by the number of nodes in the path.
|
|
attackPath.createdDate |
Risk Management > Attack Path |
Use this token to search attack paths by the date on which they were detected. You can use relative values to find recently detected paths.
|
|
attackPath.entryAsset.type |
Risk Management > Attack Path |
Use this token to search attack paths by the asset type at the entry point of the path.
|
|
attackPath.impactedAsset.isCrownJewel |
Risk Management > Attack Path |
Use a Boolean value to find attack paths whose impacted asset is classified as a crown jewel.
|
|
rule.title |
Risk Management > Attack Path |
Use a text value to search for rules by their title.
|
|
rule.severity |
Risk Management > Attack Path |
Use this token to search rules by their severity. Select a value from the drop-down menu.
|
|
rule.contributingFactors |
Risk Management > Attack Path |
Use this token to search rules by the contributing factors defined for them, that is, the risk dimensions across your attack surface that the rule evaluates. Contributing factors are: Credential Theft, Data Exfiltration, Lateral Movement Potential, Remote Code Execution
|
|
rule.mitre.attack.technique.id |
Risk Management > Attack Path |
Use a text value to search rules by the ID of the MITRE ATT&CK technique associated with them.
|
|
rule.mitre.attack.technique.name |
Risk Management > Attack Path |
Use a text value to search rules by the name of the MITRE ATT&CK technique associated with them.
|
Token
New Tokens to Build CISA BOD 26-04 Worklists
You can use these Qualys Query Language (QQL) tokens to build CISA BOD 26-04 worklists:
| Token | Sub Tab | Description |
|---|---|---|
| finding.technicalImpact |
Risk Management > All Risk Management > Vulnerabilities TruLens > KnowledgeBase > CVEs |
Select a technical impact level (TOTAL CONTROL, PARTIAL CONTROL, or UNKNOWN) to search findings based on the level of control an attacker could gain if the vulnerability is successfully exploited. Select from values in the drop-down menu. Example Show findings where an attacker could gain total control of the asset
|
| finding.isAutomatableByAdversary |
Risk Management > All Risk Management > Vulnerabilities TruLens > KnowledgeBase > CVEs |
Select TRUE or FALSE to search findings based on whether the vulnerability can be automatically exploited by an adversary without manual intervention. Example Show findings that can be automated by an adversary
|
| finding.remediationSla.days |
Risk Management > All Risk Management > Vulnerabilities TruLens > KnowledgeBase > CVEs |
Use a number or a range of numbers to search findings based on the number of days defined in the remediation SLA. Examples Show findings with a remediation SLA of 30 days
Show findings with a remediation SLA between 15 and 30 days
|
| finding.remediationSla.status |
Risk Management > All Risk Management > Vulnerabilities TruLens > KnowledgeBase > CVEs |
Select a status (WITHIN SLA, NEARING SLA, or OUT OF SLA) to search findings based on where they currently stand against the remediation SLA. Select from values in the drop-down menu. Example Show findings that are out of SLA
|
| finding.remediationSla.profile |
Risk Management > All Risk Management > Vulnerabilities TruLens > KnowledgeBase > CVEs |
Use a text value to search findings by the name of the remediation SLA profile assigned to them. Example Show findings assigned to the SLA profile named Critical Assets
|
| finding.remediationSla.dueDate |
Risk Management > All Risk Management > Vulnerabilities TruLens > KnowledgeBase > CVEs |
Use a date range or a specific date to define when the remediation SLA is due for findings. Examples Show findings with an SLA due date within certain dates
Show findings with an SLA due on a specific date
|
| finding.remediationSla.actionRequired |
Risk Management > All Risk Management > Vulnerabilities TruLens > KnowledgeBase > CVEs |
Select an action (REMEDIATE or FORENSIC TRIAGE) to search findings based on the remediation action required by the SLA. Select from values in the drop-down menu. Example Show findings that require remediation
|
Fix
Fixes
The following reported and notable customer issues are fixed in this release:
| Component/Category | Description |
|---|---|
|
ETM UAI |
We fixed an issue where the Weaponized Vulnerabilities count displayed for container assets appeared significantly higher than the vulnerability count shown in ETM. This issue was caused by differences in how weaponized vulnerability metrics were calculated and displayed compared to findings data. The count calculation has been corrected, and the displayed values now accurately align with the associated vulnerability data. |
|
ETM User Interface |
We fixed an issue where findings imported through Orca connectors were not displayed in ETM even after successful connector execution. This issue was caused by connector findings not being processed correctly for display after asset ingestion. Findings from Orca connectors now display correctly in ETM Risk Management views using correct |
|
ETM Findings |
We fixed an issue where users received a success notification when creating Risk Factors or Compensating Factors, but the items were not actually saved. This issue was caused by request validation failures that generated API errors while the UI continued to display a success message. The creation workflow now correctly validates requests and displays saved factors in the list view. |
|
ETM Findings |
We fixed an issue where the Findings page took an excessive amount of time to load for customers with very large datasets. This issue was caused by inefficient processing in the findings retrieval flow. Performance optimizations have been implemented, and findings now load significantly faster. |
|
ETM Findings |
We fixed an issue where Technology Category, Technology Name, and Technology Vendor fields were unavailable during Findings CSV export. This issue was caused by the export configuration not exposing these supported fields. The fields are now available for selection when exporting findings reports. |
|
ETM Search |
We fixed an issue where the token finding.isPatchAvailable was accepted when manually entered but did not appear in the autocomplete suggestions. This issue was caused by the token not being registered in the search token discovery list. The token is now available in autocomplete and can be selected directly from the search interface. |
|
ETM TruConfirm |
We fixed an issue where TruConfirm scheduling used an incorrect default time zone and prevented some future scans from being scheduled. This issue was caused by time zone validation and scheduling logic not consistently honoring the user profile configuration. TruConfirm now uses the configured user time zone and correctly validates scheduled scan times. |
|
ETM TruConfirm |
We fixed an issue where TruConfirm scans could incorrectly select IPv6 addresses when users targeted IP ranges or CIDR ranges. This issue was caused by IP matching logic falling back to the first available network interface when an exact match was not found. IP selection now correctly prioritizes the intended IPv4 targets and processes scan scopes as expected. |
|
ETM Dashboard |
We fixed an issue where CISA KEV counts displayed on the dashboard did not match the counts shown in findings views. This issue was caused by the dashboard referencing an incorrect data source when calculating the CISA KEV metric. Dashboard counts now accurately reflect the underlying findings data. |
|
ETM TruRisk™ |
We fixed an issue where Asset Criticality Score (ACS) and TruRisk™ scores were missing from Host List API responses even though the values were available in the UI. This issue was caused by score publication and downstream processing inconsistencies. API responses now correctly return ACS and TruRisk™ score information. |