PCI Compliance Release 6.9
October 30, 2026
This release adds time-based one-time password (TOTP) multi-factor authentication, so you can verify your identity with a second factor when you sign in to PCI Compliance.
New Feature
TOTP-based Multi-Factor Authentication
What's New for You
You can now grant, revoke, and reset MFA for your sub-users as a Merchant or Bank POC, and move them from Symantec VIP to authenticator applications during the grace period.
You can now set up time-based one-time password (TOTP) multi-factor authentication (MFA) for the merchant, bank, and admin users.
PCI Compliance now supports TOTP-based multi-factor authentication (MFA) for the Merchant, Bank, and Admin users. Through this update, Merchant and Bank point-of-contact (POC) users can now grant, revoke, and reset MFA directly for their sub-users.
This update does not affect API access or SAML SSO users as MFA applies only for PCI application logins.
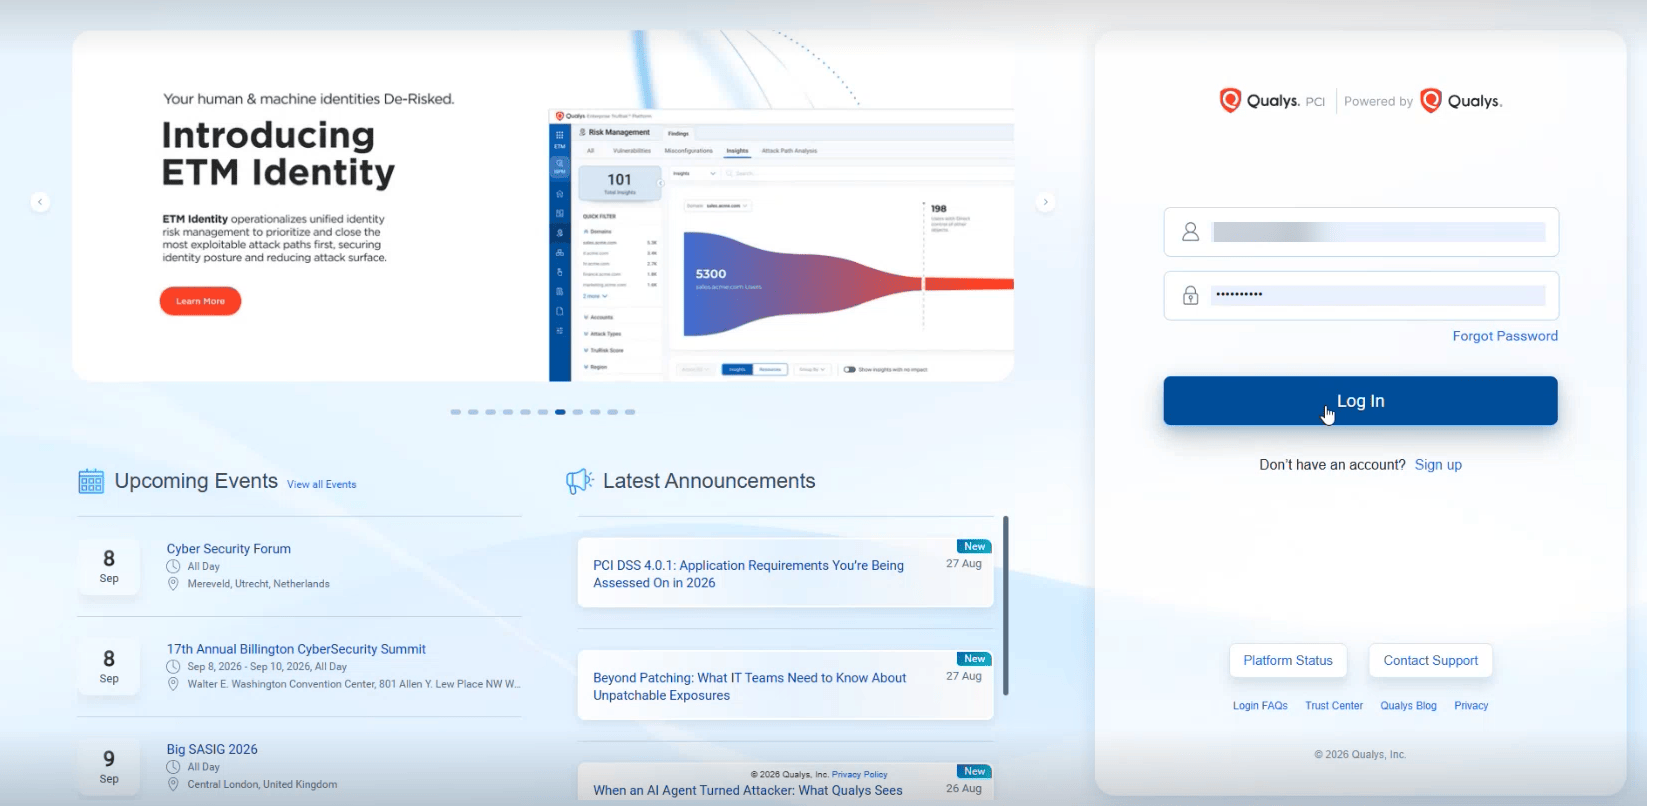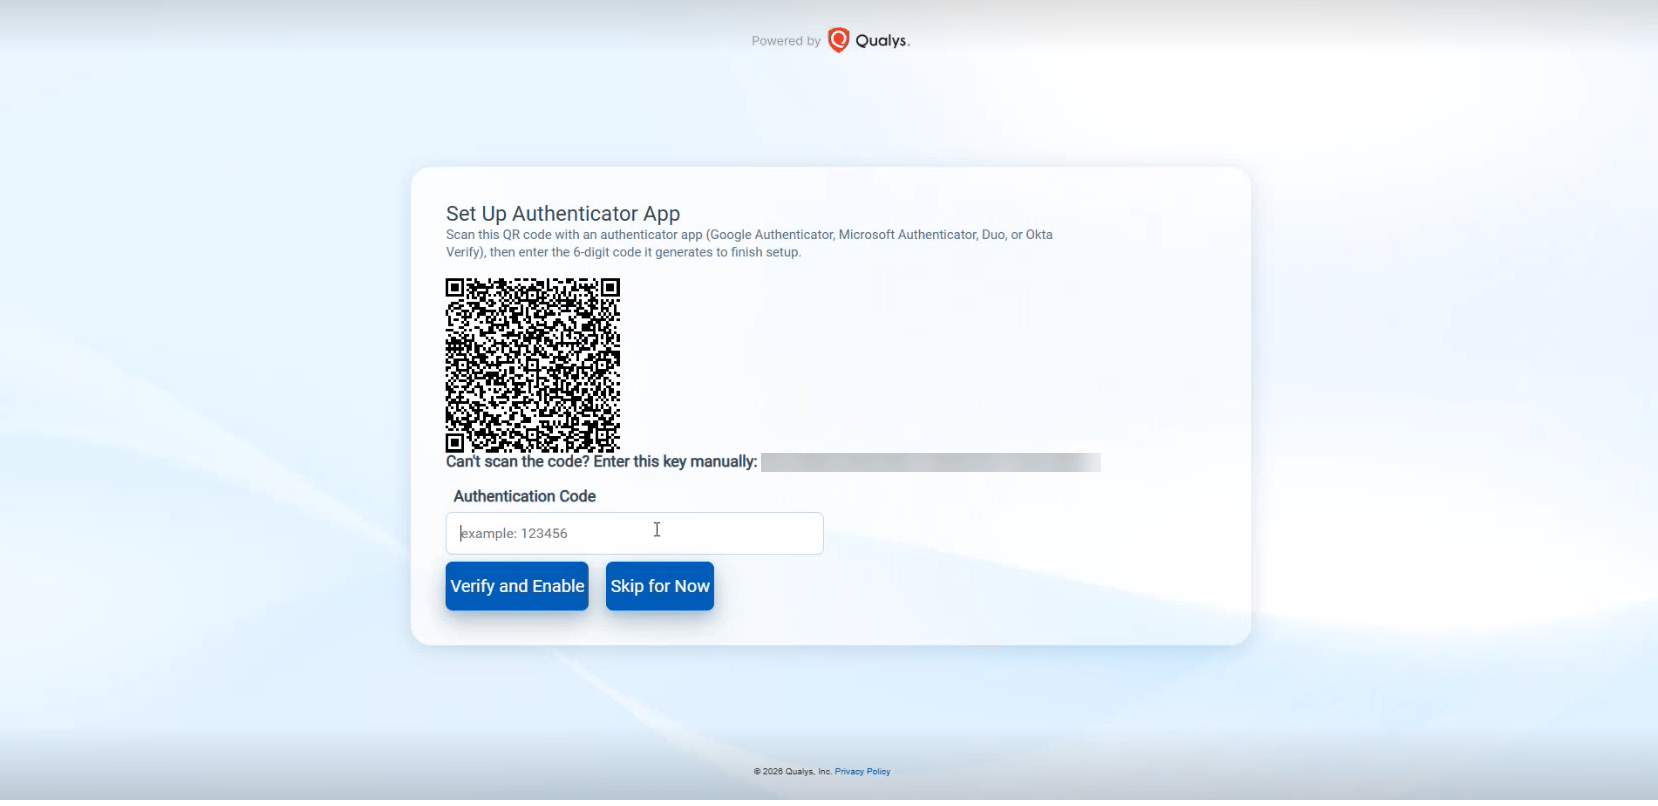
To enable the MFA option for the first time, Merchant and Bank POCs must raise a request to the Qualys support team. Once enabled, users can set up MFA by scanning a QR code or entering a setup key in one of the supported authenticator applications: Microsoft Authenticator, Google Authenticator, Duo, and Okta Verify.
MFA replaces Symantec VIP as the standard authenticator mechanism. Symantec VIP will remain active during a transitional grace period, allowing organizations to onboard users to TOTP-based authenticator apps before the VIP support ends.