Qualys Flow Release 1.24
August 25, 2026
With this QFlow release, we are introducing the following new features and enhancements.
Generate Workflows with AI
You can now create QFlow workflows just by describing them. Generate with AI option is now available on the Create Workflow screen along with From scratch and Use a template, so instead of building a workflow node by node, you can tell QFlow what you want and generate a workflow. This is available now for AWS and Azure workflows.
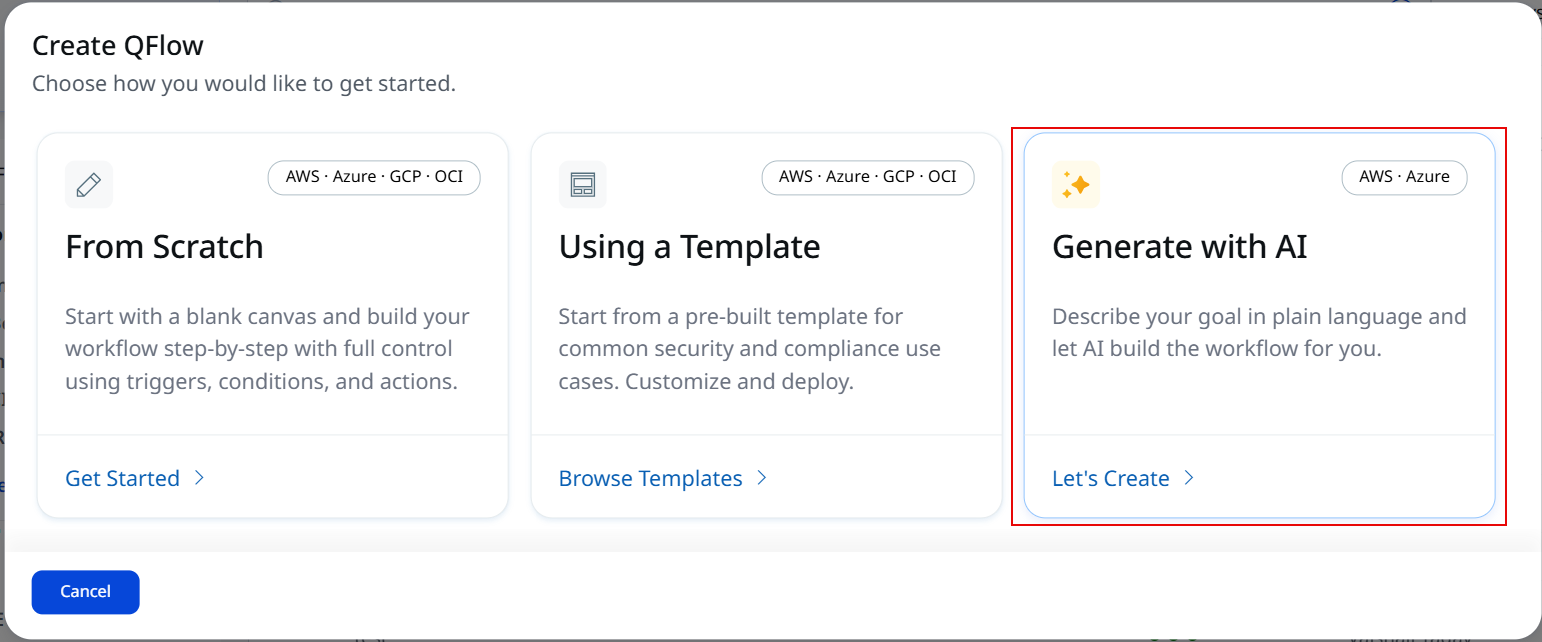
Key Features
- Confirmation before generation: QFlow repeats your request back to you and waits for confirmation before building anything.
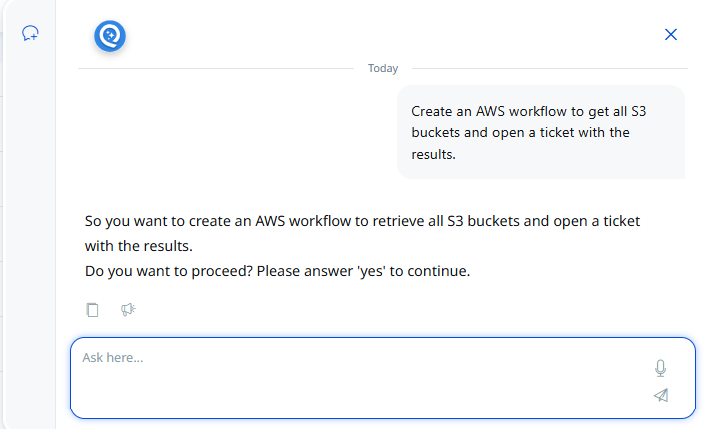
- Direct editor access: Once confirmed, the workflow opens fully editable, just like any workflow built by hand.
- In-chat refinement: While the session is open, you can send follow-up prompts, add a node, change a filter, add a formatter step, before saving the workflow.
- AI-generated label: Workflows built this way carry an "AI-generated" tag in your workflow list, so they're easy to spot.
The AI-generated workflow might not always be perfect, especially with more complex processes. It's advisable to review node configurations and details carefully before live deployment.
Benefits
- Faster workflow creation: Describe the outcome you want instead of manually building each node from scratch.
- Lower barrier to entry: Users less familiar with individual node types can still produce a functional workflow.
- Handles simple and complex requests: Supports both single-step requests and multi-step, iterative prompting for more complex automation.
- Consistent with existing process: Generated workflows use the same account/region selection and save steps as manually built ones, so there's no new process to learn there.
Limitations
- AI can only generate new workflows. It cannot be used to open and modify a workflow that has already been saved, whether it was built manually or by AI.
- Once a workflow is saved, and the originating chat session is closed, no further AI-based changes can be made to it. A new workflow must be started to use AI again.
- Each user is limited to 100 AI chat messages per day.
Deploy workflows based on tags
When saving a QFlow workflow, you can now choose how it gets deployed across your cloud environment:
- Manual Scope - explicitly select the connectors the workflow should run against (existing behavior, unchanged).
- Dynamic Scope - automatically target connectors based on criteria you define, such as tags, so the workflow's scope stays current as your inventory changes.
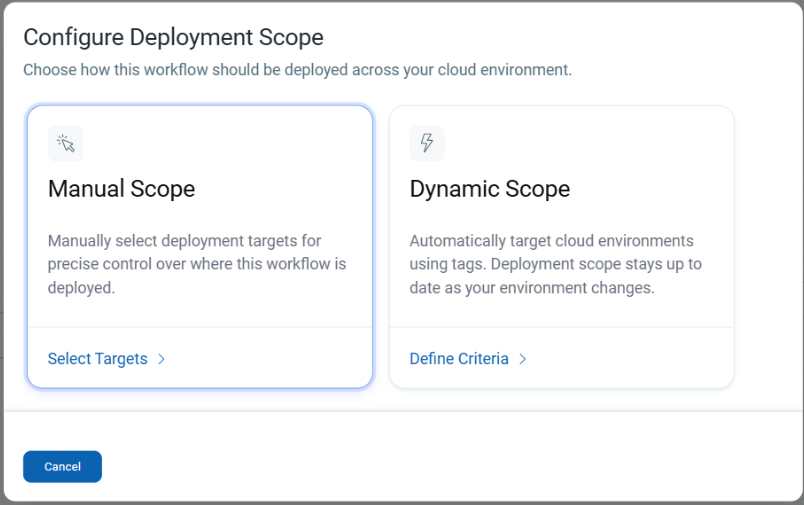
Within Dynamic Scope, Custom Scope Configuration lets you build inclusion and exclusion rules from tags. Connectors that match your inclusion tags are automatically added to the workflow's scope. Optionally, you can add a connector tag to exclude it from the workflow.
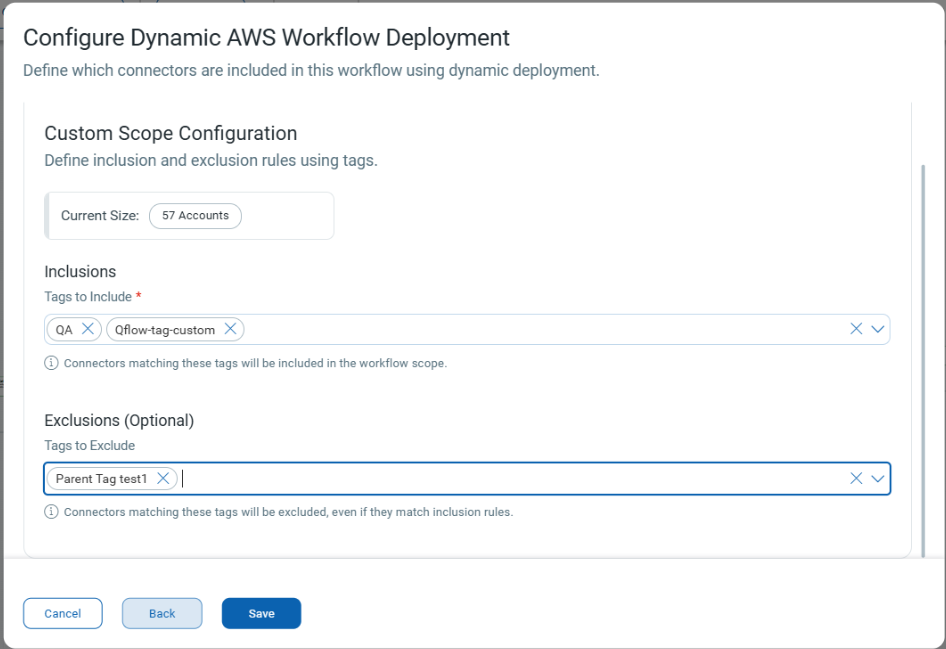
Contact your Technical Account Manager (TAM) or Qualys Support to enable this feature for your account.
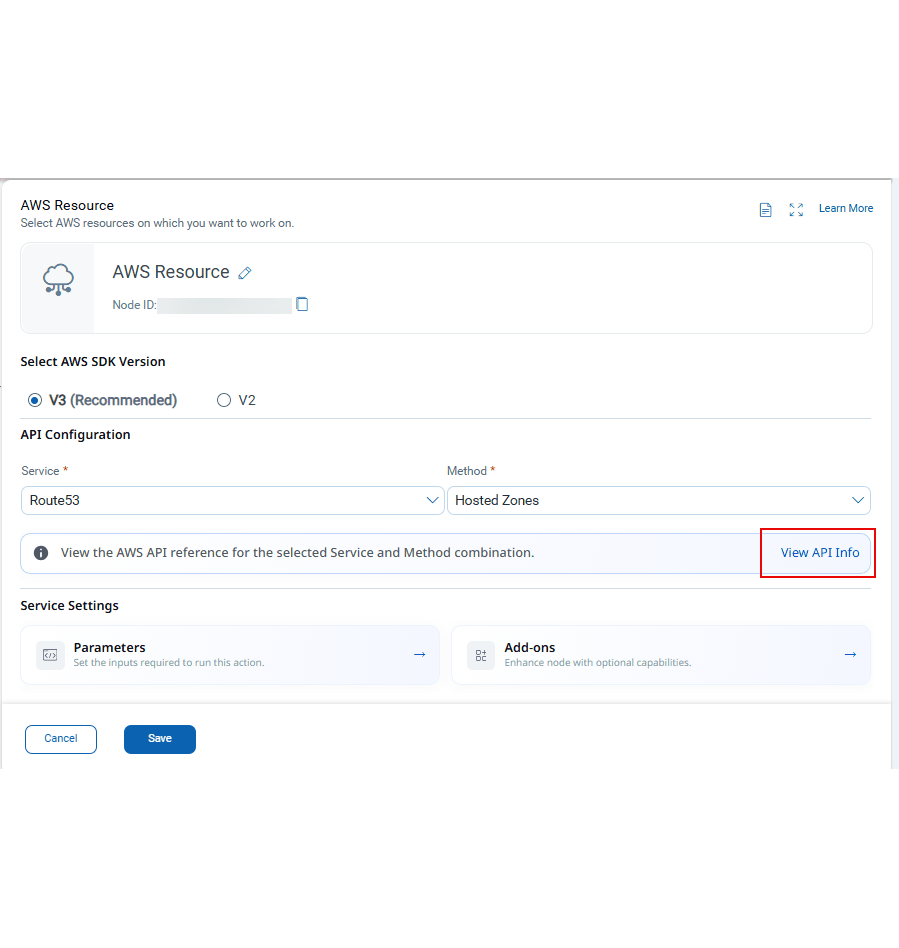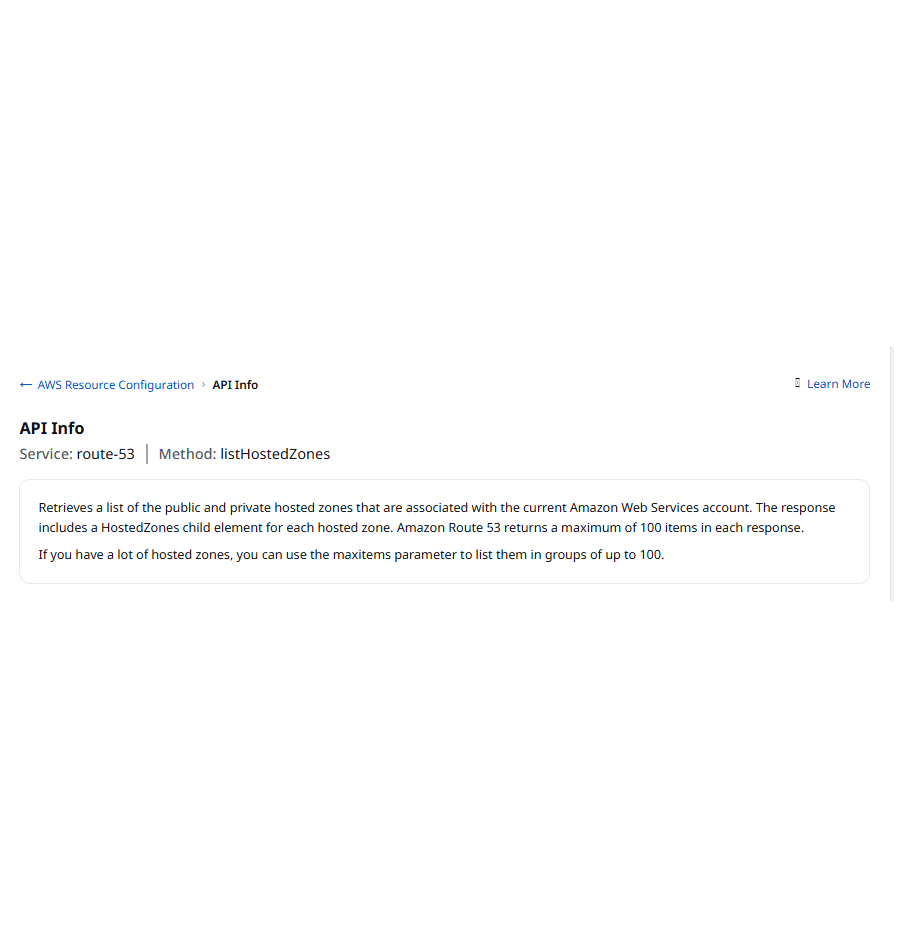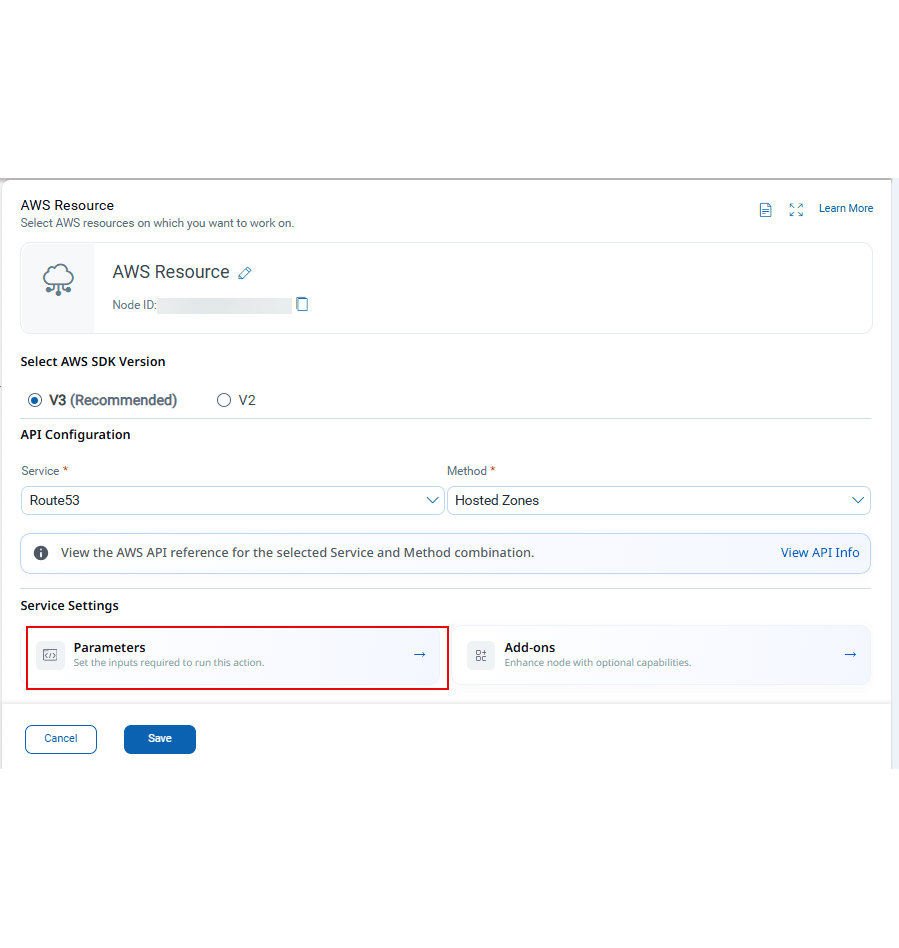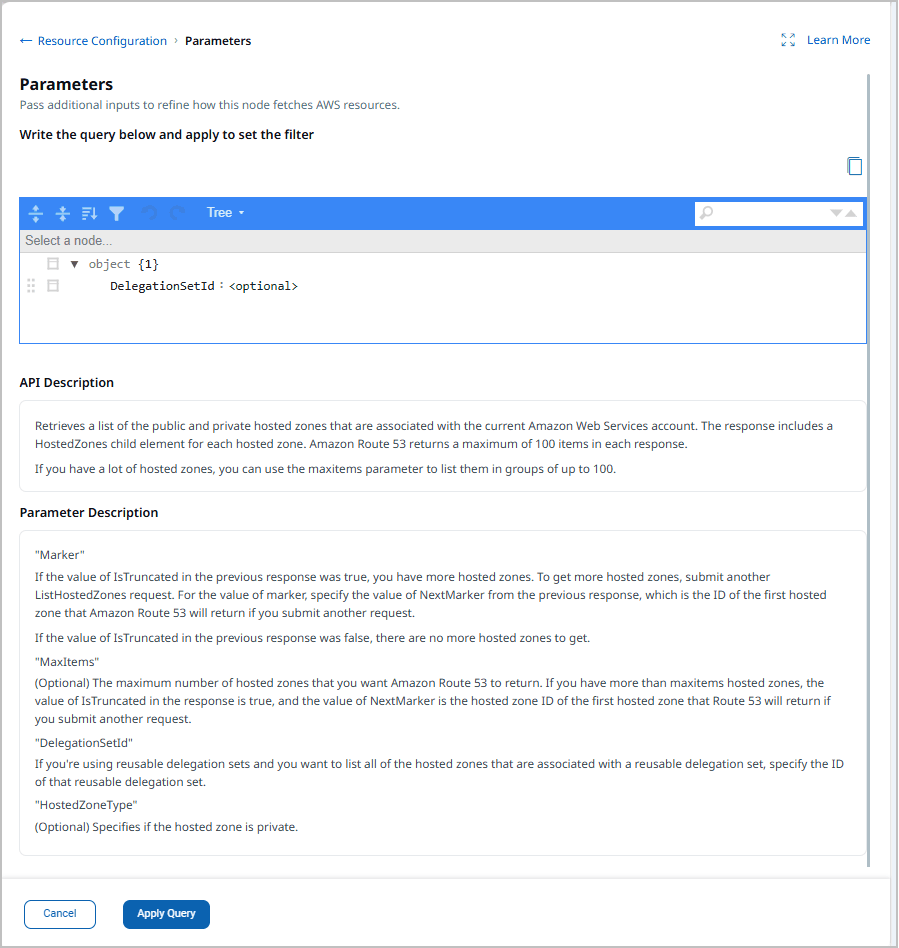
API and parameter descriptions for AWS and Azure
When configuring a Resource, Action, or Raw node against an AWS or Azure service, QFlow now shows in-context descriptions for:
- API/method - what it does and when to use it
- Parameters - whether each one is required and what value it expects.
Full support (method + parameter descriptions) is available for AWS SDK V3. For Azure, method descriptions are shown, but parameter descriptions aren't supported yet.
Added support for New AWS and Azure templates
We have added 13 new QFlow templates across AWS and Azure, bringing the total in the template library from 407 to 420. These templates enable one-click remediation of cloud vulnerabilities and misconfigurations, reducing manual effort and improving compliance posture. Each template maps to a Control ID within TotalCloud for precise governance.
| Cloud | Template Name |
|---|---|
| AWS | Spoke and Entity Hub VPCs must not have AWS Direct Connect configured |
| Spoke and Entity Hub VPCs must not have AWS VPN configured | |
| AWS Default VPC must not be used | |
| Spoke and Entity Hub VPCs must not have VPC peering | |
| S3 Bucket Ownership control assigned | |
| Azure | VNet peering must not be done directly between spokes |
| Spoke routing table must contain default route towards hub firewall | |
| NSG must not allow unrestricted RDP access at Spoke level | |
| NSG must not allow unrestricted SSH access at Spoke level | |
| Spoke subnet must have a custom route table | |
| Spoke Subnets must be associated with a Network Security Group | |
| Spoke VNet must be peered only with one Entity Hub | |
| Spoke VNet must not have GatewaySubnet |