QScanner Release 5.2.0
September 29, 2026
QScanner 5.2.0 offers the following features.
- Scan Azure Functions Alongside AWS Lambda
- Cloud Tag Retrieval for Serverless Functions
- Enhanced Lambda Function Scanning
- Extended JAR SCA in Offline Mode: Scan JAR Files Without Network Access
- Support for QScanner MCP Server
- Enhanced CI/CD Policy Evaluation: Detailed Breakdown in QScanner Results
- Configure TLS Separately for Container Registries
- Subscription-Level OAuth for QScanner: Centralized Token Authentication
- Busybox-Based Image Scanning
- Packages in SARIF Report
New Feature
Scan Azure Functions Alongside AWS Lambda
Organizations using Microsoft Azure can now scan their Azure Functions using the same QScanner workflow, extending the serverless scanning coverage beyond the AWS Lambda support introduced in QScanner 5.1.0. QScanner automatically detects the function type and performs the appropriate scan.
To know QScanner supportability towards Azure Functions, refer to Azure Function Scan > Supported Configurations.
Key Benefits
- Multi-Cloud Serverless Coverage: Scan serverless functions across both AWS and Azure using a unified QScanner workflow.
- Consistent Security Posture: Apply the same vulnerability and security assessment practices to Azure Functions as to containers and AWS Lambda.
- Simplified Operations: No additional tooling required; Azure Functions scanning integrates into existing QScanner deployments.
Supported Matrix for Serverless Functions
The supported matrix for QScanner 5.2.0 with serverless functions is provided below. Deployment Storage refers to the storage service used to deploy the function, such as Azure Blob Storage in Azure. Source Repository refers to the repository where the function's source code is maintained, such as Git or another supported source control repository.
| Cloud Provider | Deployment Type | |||
|---|---|---|---|---|
| Zip Archive | Container Image | Cloud Storage | Source Repository | |
| AWS Lambda | ✅Supported | ✅Supported | ❌Not Supported | ❌Not Supported |
| Azure Functions | ✅Supported | ✅Supported | ❌Not Supported | ❌Not Supported |
| GCP | ❌Not Supported | ❌Not Supported | ❌Not Supported | ❌Not Supported |
New Feature
Cloud Tag Retrieval for Serverless Functions
QScanner now retrieves cloud tags associated with serverless functions during scanning. These tags are pulled from the cloud provider and included with scan results, so you can identify owners, assign findings, and organize assets for AWS Lambda and Azure Functions. The tags are visible in Qualys Container Security alongside other scan results and are retrieved automatically without additional configuration.
Key Benefits
- Improved Asset Ownership: Use cloud tags to identify team or application ownership of serverless functions.
- Streamlined Assignment: Route findings and remediation tasks based on tag-driven ownership.
- Consistent Asset Context: Apply the same tag-based organization to serverless functions as to other cloud assets.
Enhancement
Enhanced Lambda Function Scanning
You can now track your AWS Lambda function scans with greater visibility. For functions deployed as container images, QScanner associates the function with its container image. Scan records are retained for a configurable period to support traceability, reporting, and lifecycle management.
Serverless Functions Data Retention Setting
A new Serverless Functions section is now available in Qualys Enterprise TruRisk™ Platform under Configurations > General > Data Retention Settings. You can configure how long serverless function records are retained. The retention period is configurable between 7 (Seven) and 30 days. Records for serverless functions that are not updated within the configured period are automatically removed.
New Feature
Extended JAR SCA in Offline Mode: Scan JAR Files Without Network Access
You can now detect vulnerable JAR files, including nested JARs, in air-gapped or network-restricted environments. QScanner's offline scan mode (--offline-scan) now supports SCA detection for JAR files by offloading JAVADB resolution to the platform-side Delta Service, so no live network connection is required during the scan. Previously, JAVADB resolution was available only in Online mode.
Use the --scan-types pkg,sca option along with --offline-scan to include JAR SCA detection.
Key Benefits
- Air-Gapped Environment Support: Enables JAR SCA detection in network-restricted environments where online scans are not possible.
- No Runtime Network Dependency: QScanner handles JAVADB resolution internally; no live connection is required during the scan.
- Consistent SCA Coverage: Uniform SCA coverage across both online and offline scan modes, including nested JAR packages.
New Feature
Support for QScanner MCP Server
QScanner now includes an MCP (Model Context Protocol) server, enabling integration with AI assistants and LLM-powered workflows. The new mcp command starts the QScanner MCP server.
Key Benefits
- AI Tool Integration: Connect AI assistants and LLM-powered workflows directly to QScanner scanning capabilities.
- Programmatic Access: Invoke QScanner operations through the standardized MCP protocol without direct CLI interaction.
- Flexible Automation: Embed QScanner into agentic pipelines and AI-driven security automation workflows.
Enhancement
Enhanced CI/CD Policy Evaluation: Detailed Breakdown in QScanner Results
QScanner now returns a structured Policy Evaluation report alongside the overall Pass or Fail result for CI/CD policy evaluations. The report breaks down the evaluated policy, identifying exactly which criteria caused the evaluation outcome. Previously, QScanner returned only the final Pass or Fail result, requiring manual investigation to determine the root cause of failures.
This release also introduces support for multi-policy evaluation. QScanner can now evaluate a container image against multiple policies in a single scan, returning individual results for each policy.
Key Benefits
- Immediate Failure Visibility: Know which policy criteria caused a CI/CD evaluation failure without separate investigation.
- Multi-Policy Support: Evaluate images against multiple policies simultaneously and receive per-policy results in a single scan.
- Structured Reporting: Easy-to-read policy evaluation breakdown presented alongside the final Pass or Fail result.
- Reduced Troubleshooting Time: Failure reasons surface directly in QScanner output, shortening the feedback loop for developers.
New Feature
Configure TLS Separately for Container Registries
QScanner now supports a separate TLS configuration for communication with remote container registries. You can use --registry-cert-path to specify a custom CA certificate for registry HTTPS connections, and --registry-skip-verify-tls to skip TLS verification when connecting to a registry that uses an untrusted or self-signed certificate.
This separation ensures that TLS settings for the Qualys Enterprise TruRisk™ Platform and the remote registry can be configured independently. For example, you can verify the Qualys Enterprise TruRisk™ Platform endpoint while bypassing verification for an internal registry, or supply a private CA that is trusted only by the registry.
Existing customers using an insecure registry will need to explicitly specify either the new flag or the registry certificate.
For example, if you have a CA (Certificate Authority) certificate of this registry, this flow should also work when using it,
--registry-cert-path /path/to/abc.cert --registry-skip-verify-tls=false
Key Benefits
- Independent TLS Control: Configure registry TLS separately from Qualys Platform TLS.
- Support for Private Registries: Connect to registries that use custom or self-signed certificates.
- Flexible Deployment Options: Skip registry TLS verification only when required in controlled environments.
New Feature
Subscription-level OAuth for QScanner: Centralized Token Authentication
You can now generate a subscription-level Client ID and Client Secret to authenticate QScanner using the --client-type flag, removing the dependency on individual user accounts. Previously, QScanner authentication required a user-level token tied to a specific account. Subscription-level tokens allow centralized credential management at the subscription level.
- The Subscription Token is highly sensitive and must be treated as a secret credential.
- Subscription-level tokens are supported for QScanner only.
- Container Security APIs cannot be accessed using a subscription-level token.
Required Permissions
To use a subscription-level token with QScanner, assign the following permissions when creating the client.
- Policy Evaluation
- QScanner Scan CICD
- CS Access
- CS API Access
- CS UI Access
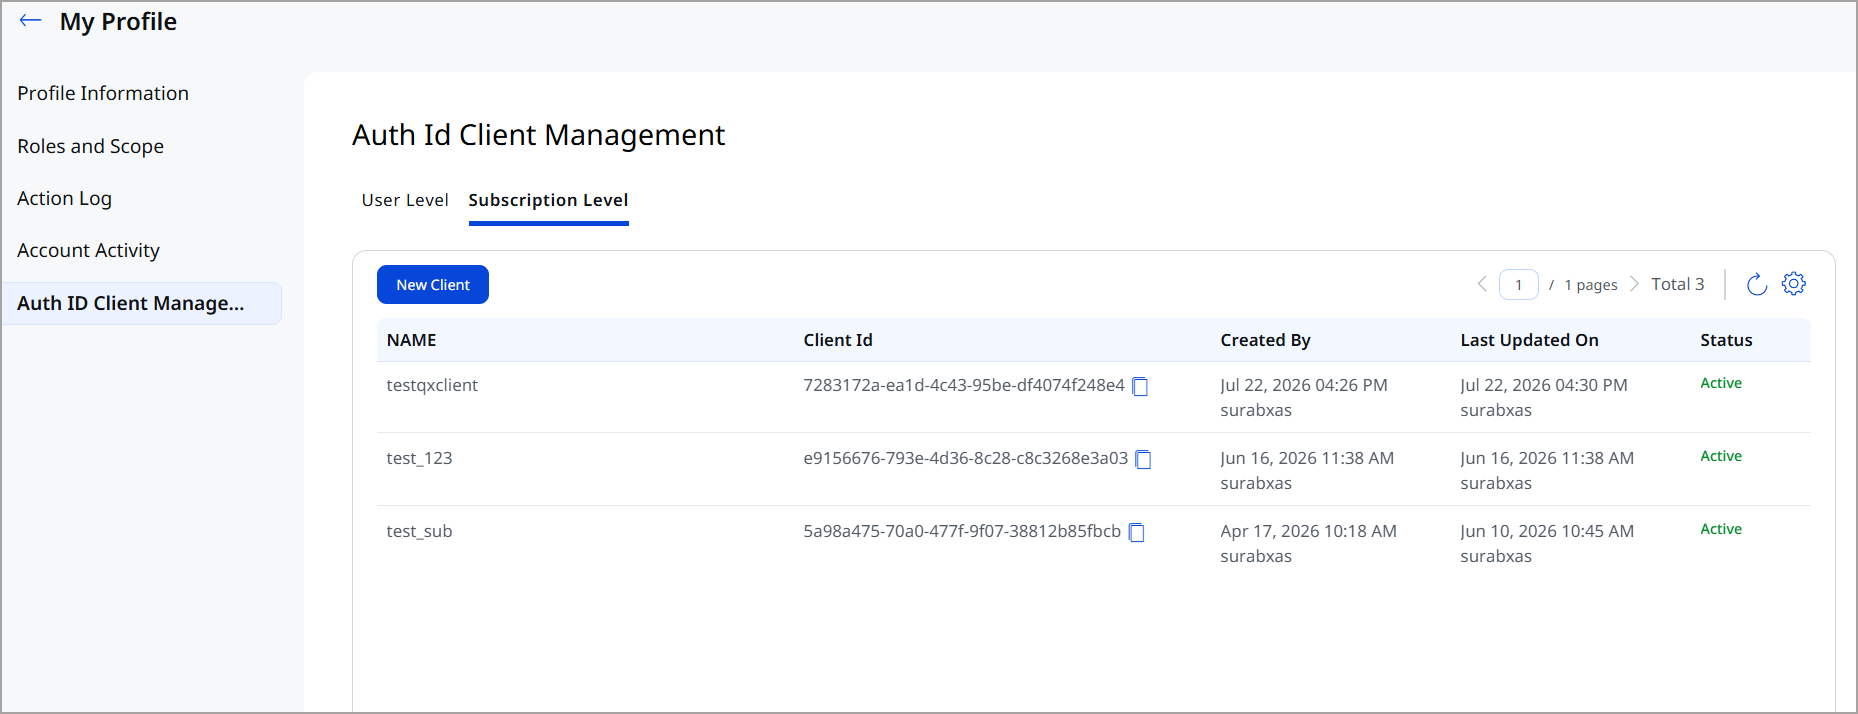
The above image shows the subscription-level OAuth token configuration in Auth ID Client Management.
Key Benefits
- Resilient Authentication: Eliminates dependency on individual user accounts, making QScanner authentication resilient to account changes or departures.
- Centralized Credential Management: Simplifies token lifecycle administration at the subscription level.
- Least-Privilege Access: Scope permissions specifically to QScanner operations.
- Reduced CI/CD Maintenance: Decouples pipeline credentials from personal accounts, reducing overhead.
Enhancement
Busybox-based Image Scanning
QScanner now supports scanning busybox-based container images when a busybox binary rule is enabled. Busybox bundles many common Unix utilities into a single small executable and is widely used in minimal container images. Previously, busybox installations were not assessed for vulnerable components. With this enhancement, QScanner correctly identifies busybox installations and evaluates them for known vulnerabilities.
Key Benefits
- Expanded Image Coverage: Accurately scans minimal and embedded container images that rely on busybox.
- Improved Vulnerability Detection: Identifies known vulnerabilities in busybox binaries that were previously undetected.
- Consistent Security Assessment: Applies the same security scanning capabilities to busybox-based images as to standard container images.
Enhancement
Packages in SARIF Report
SARIF (Static Analysis Results Interchange Format) reports generated by QScanner now include package details alongside vulnerability findings. Previously, SARIF output contained only vulnerability information, requiring teams to cross-reference a separate inventory report to understand which software packages were present in the scanned image. With this enhancement, a single SARIF report provides both the software inventory and associated security findings in one place.
Package entries in the SARIF report include details such as package name, version, and type, making it easier for security and development teams to trace vulnerabilities back to their source packages without additional tooling. Package inclusion is automatic and requires no additional flags. Existing tools that consume SARIF files can read the new package data without changes, as the additional fields are additive and do not alter the existing report structure.
Key Benefits
- Consolidated Reporting: A single SARIF output contains both software inventory and vulnerability findings, reducing the need to correlate multiple reports.
- Improved Traceability: Directly trace each vulnerability finding to the specific package that introduced it.
- Broader Tool Compatibility: Richer SARIF output integrates more effectively with security platforms, IDEs, and CI/CD tools that consume SARIF.
- Faster Remediation: Package context alongside findings helps developers identify and update the responsible dependency without separate investigation.