F5 BIG-IP Non Advanced Shell Account Setup
BIG-IP user with an Administrator or User Manager role, can assign user roles to other BIG-IP user accounts. Specifically, for each BIG-IP user account, you can assign a specific user role to each administrative partition to which you grant the user access. In this way, you can control the BIG-IP configuration objects that the user can manage, as well as the types of actions the user can perform on those objects
User Roles and Access Scope
The multiple user roles and respective access details are described in the following table with use cases:
|
User Role |
Description |
Write Access |
Read Access |
No Access |
SHELL |
|---|---|---|---|---|---|
|
Administrator |
This is the most powerful user role. A user with this role grants complete access to all system objects. Users with this role cannot have any other user roles in the system. |
All objects in the system. |
All objects in the system. |
Not applicable |
BASH |
|
Resource Administrator |
A user with this role grants access to all system objects except BIG-IP user accounts. Users with this role can view a list of all user accounts on the system but cannot view or modify user account properties, except for their own accounts. Users with this role cannot have any other user roles on the system. |
Most objects in the system have their own password. |
Most objects in the system include a list of user accounts. |
User account properties and some command-line interface (CLI) commands, such as commands that edit TMSH scripts. |
BASH |
|
Auditor |
This is a powerful role that grants read-only access to all system configuration data except ARP data, archives, and support tools. Users with this role cannot have any other user roles in the system, but they can edit their own account passwords. When granted terminal access, users with this role can access TMSH but not the advanced shell. |
Their own user account password. |
Most objects in the system, in all partitions. |
ARP entries, archives, the advanced shell, and support tools. |
TMSH |
Required Role
Scan account for a successful scan needs:
| Role: | auditor |
| Partition: | all-partitions |
| Shell: | tmsh |
Steps to Create Scan Account
Create a scan user account with privilege level 3.
Here are the steps:
- Log in to tmsh by typing the following command:
tmsh - To create a new user, use the following command syntax:
create /auth user <user_name> partition-access add { <parition_name> { role <role> } } prompt-for-password shell <shell> - Scan User partition, role, and shell options need to be set as below:
create /auth user qualys_scan partition-access add { all-partitions { role auditor } } prompt-for-password shell tmsh

	changing password for qualys_scan

	new password:

	confirm password:
Environment Setup Steps (Mandatory)
By default, the CLI Preference display-threshold is set to 100, which will trigger the question "Display all [number] items? (y/n)." when more than 100 items are configured.
Required Action:
- Configure CLI Preference to disable paging and display-threshold set to 0
- Login to the TMSH using the appropriate user credentials.
BIG-IP F5 does not provide a built-in option in the TMSH shell to disable the pager on a per-login basis. The
modify cli preference pager disabled display-threshold 0command applies only to the current TMSH session for the scan account and remains in effect for all commands that run during that session. This setting is user-specific and does not apply globally. Other user accounts on the BIG-IP system retain their own CLI preference settings and remain unaffected. - Run the following command:
modify cli preference pager disabled display-threshold 0. - Save the configuration:
save sys config.
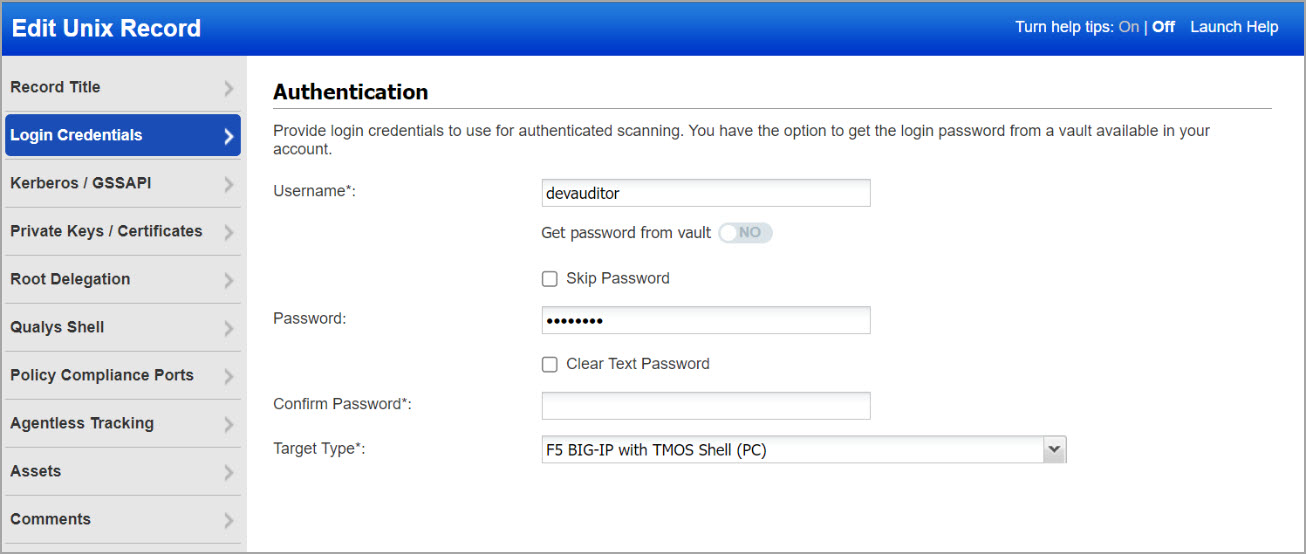
F5 BIG-IP Authentication at UI Level
Authentication > New > OS > Unix
Target Type ID: F5 BIG-IP with TMOS Shell (PC)