VMDR OT Release 1.7
August 24, 2026
Enhanced User Interface for VMDR OT
We introduced an improved user experience across all VMDR OT pages, with updates to fonts, colors, typography, and buttons that make the interface more intuitive and user-friendly. Enhancements to the User Interface and design system improve visual consistency, readability, and usability throughout the application, resulting in a cleaner and more streamlined experience.
Key benefits are:
- Cleaner, more consistent screens
- Easier-to-read and understandable text
- Important information stands out better, with less clutter
- Faster comprehension of risk, status, and numbers
- User Interface Consistency and Clarity
Introducing the new and improved User Interface with the following key upgrades:
- Easier-to-read labels and text, with ALL CAPS replaced by sentence-style text
- Consistent text style for status and source names across the application
- Uniform text colors in tables, filters, page numbers, and tabs
- Aligned colors and text styles for tabs and page navigation throughout the application
- Clear visual indicators for buttons and options, showing active, inactive, or secondary states
- Better emphasis on important information, with subtle styling for less critical details to help users focus
Asset Criticality Score (ACS) and TruRisk™ Score
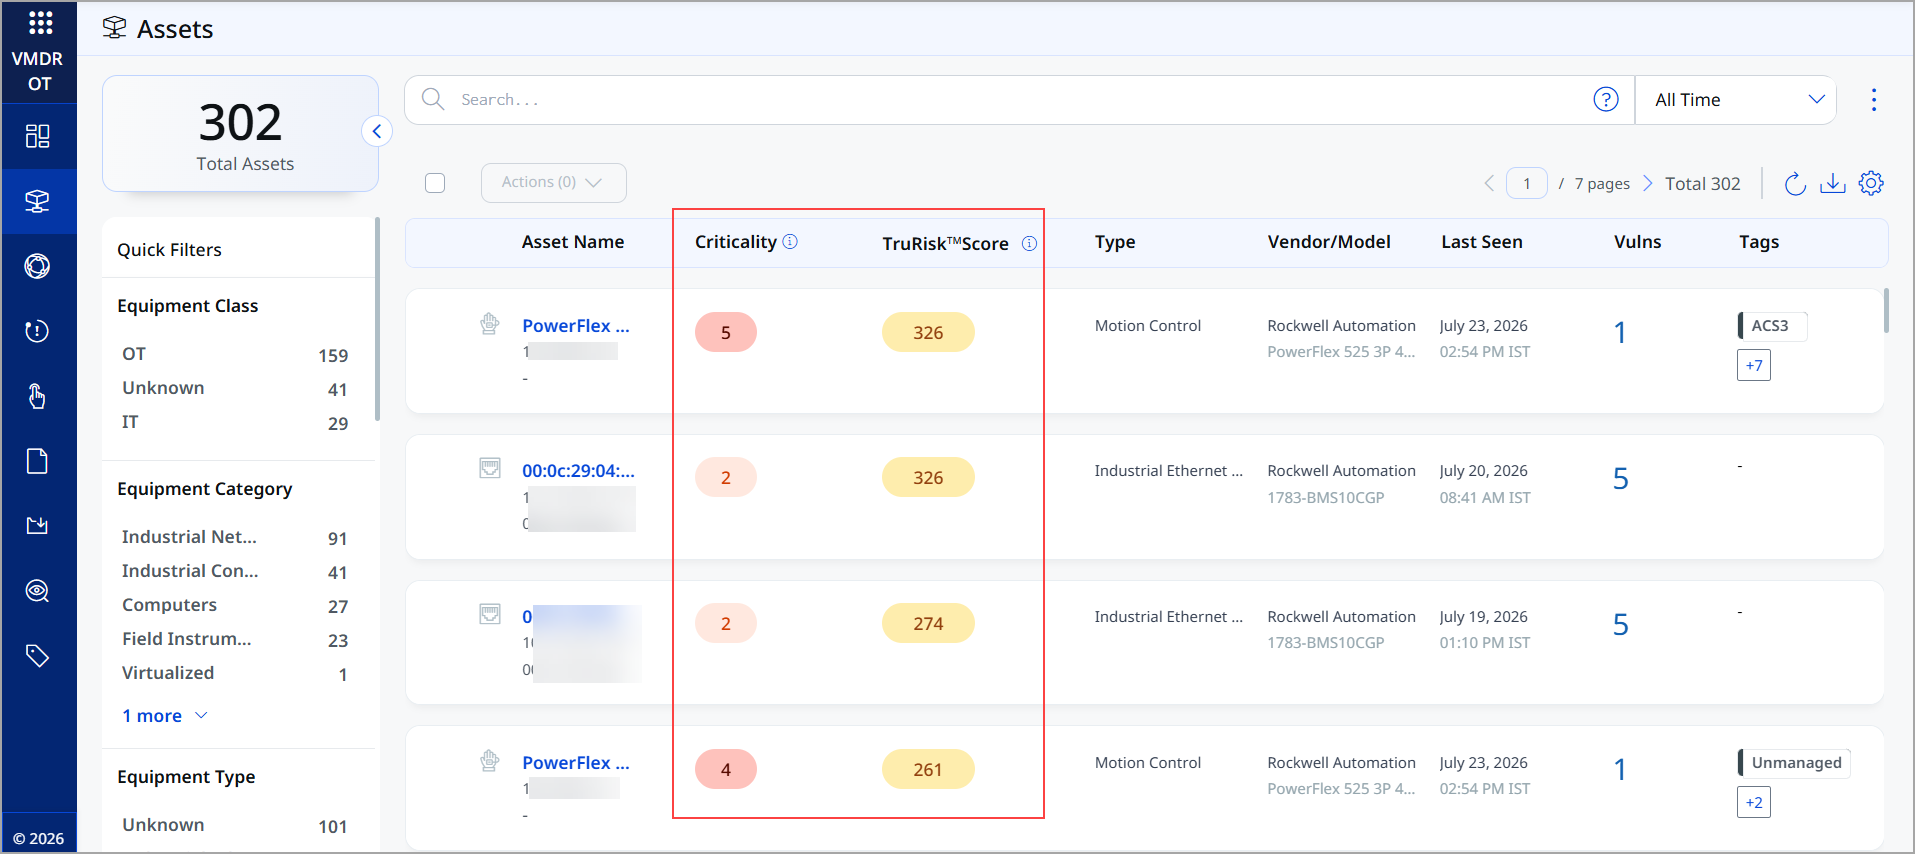
VMDR OT now supports Qualys TruRisk™ Score and Asset Criticality Score (ACS) for OT assets, enabling organizations to prioritize remediation based on both asset importance and security risk.
Asset Criticality Score (ACS)
The Asset Criticality Score (ACS) represents the business importance of an asset. It is derived from the criticality scores assigned to the tags associated with the asset and is rated on a scale of 1 (lowest) to 5 (highest).
ACS helps you classify assets by business impact, ensuring critical assets receive higher priority in risk assessment and remediation.
For more information, refer to Asset Criticality Score (ACS) in VMDR OT Online Help.
TruRisk™ Score
TruRisk™ Score is a risk-scoring framework that evaluates the security posture of an OT asset on a scale of 0 to 1000. It combines vulnerability severity and Asset Criticality Score (ACS) to help you prioritize remediation based on both security risk and business impact. The TruRisk™ Score is calculated only for assets with detected vulnerabilities.
For more information, refer to TruRisk™ Score in VMDR OT Online Help.
Qualys is rolling out the TruRisk™ Score feature in phases. For more details, contact Qualys Support.
You can view both scores from the Assets tab to quickly identify high-risk and business-critical assets.
Asset Details Enhancements
The asset details now include security, risk, and business context of an asset to help you better understand the asset's risk posture, prioritize remediation, and make informed decisions.
The following new information is now available:
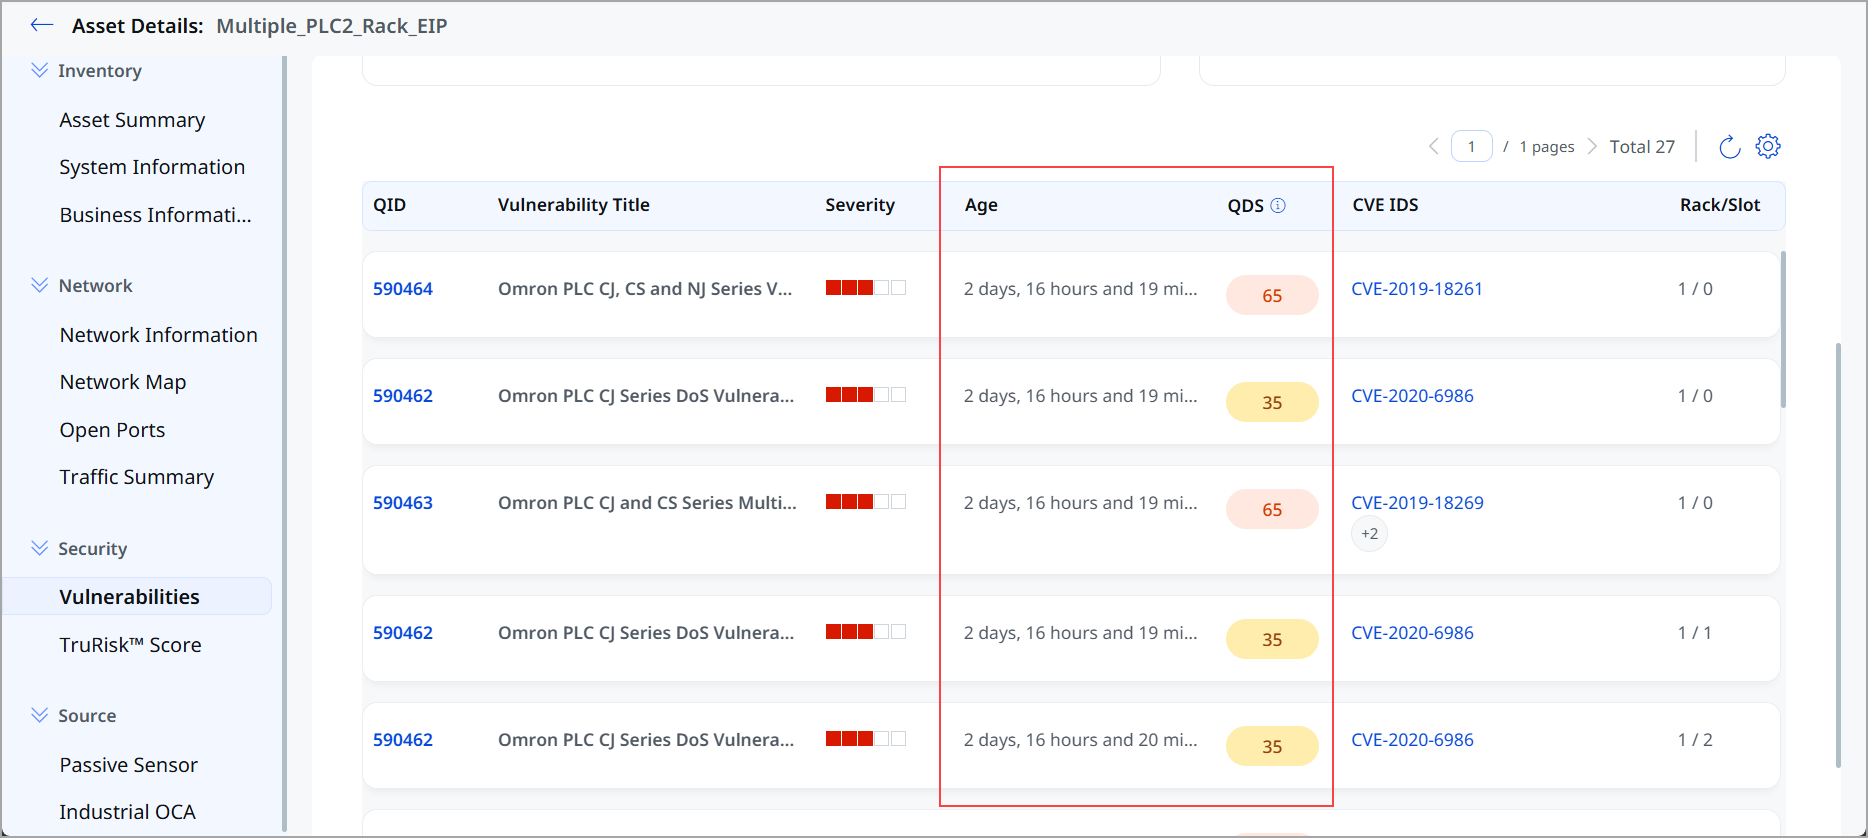
Identify high-risk vulnerabilities and prioritize the remediation efforts using the following new vulnerability details:
- QDS: Displays the QDS for each QID to help assess its relative risk.
- Age: Displays the first detected timestamp of the vulnerability.
You can view these details on the Asset Details > Security > Vulnerabilities tab.
For more information, refer to VMDR OT Online Help.
TruRisk™ Score Calculation DetailsTruRisk™ Score Calculation Details
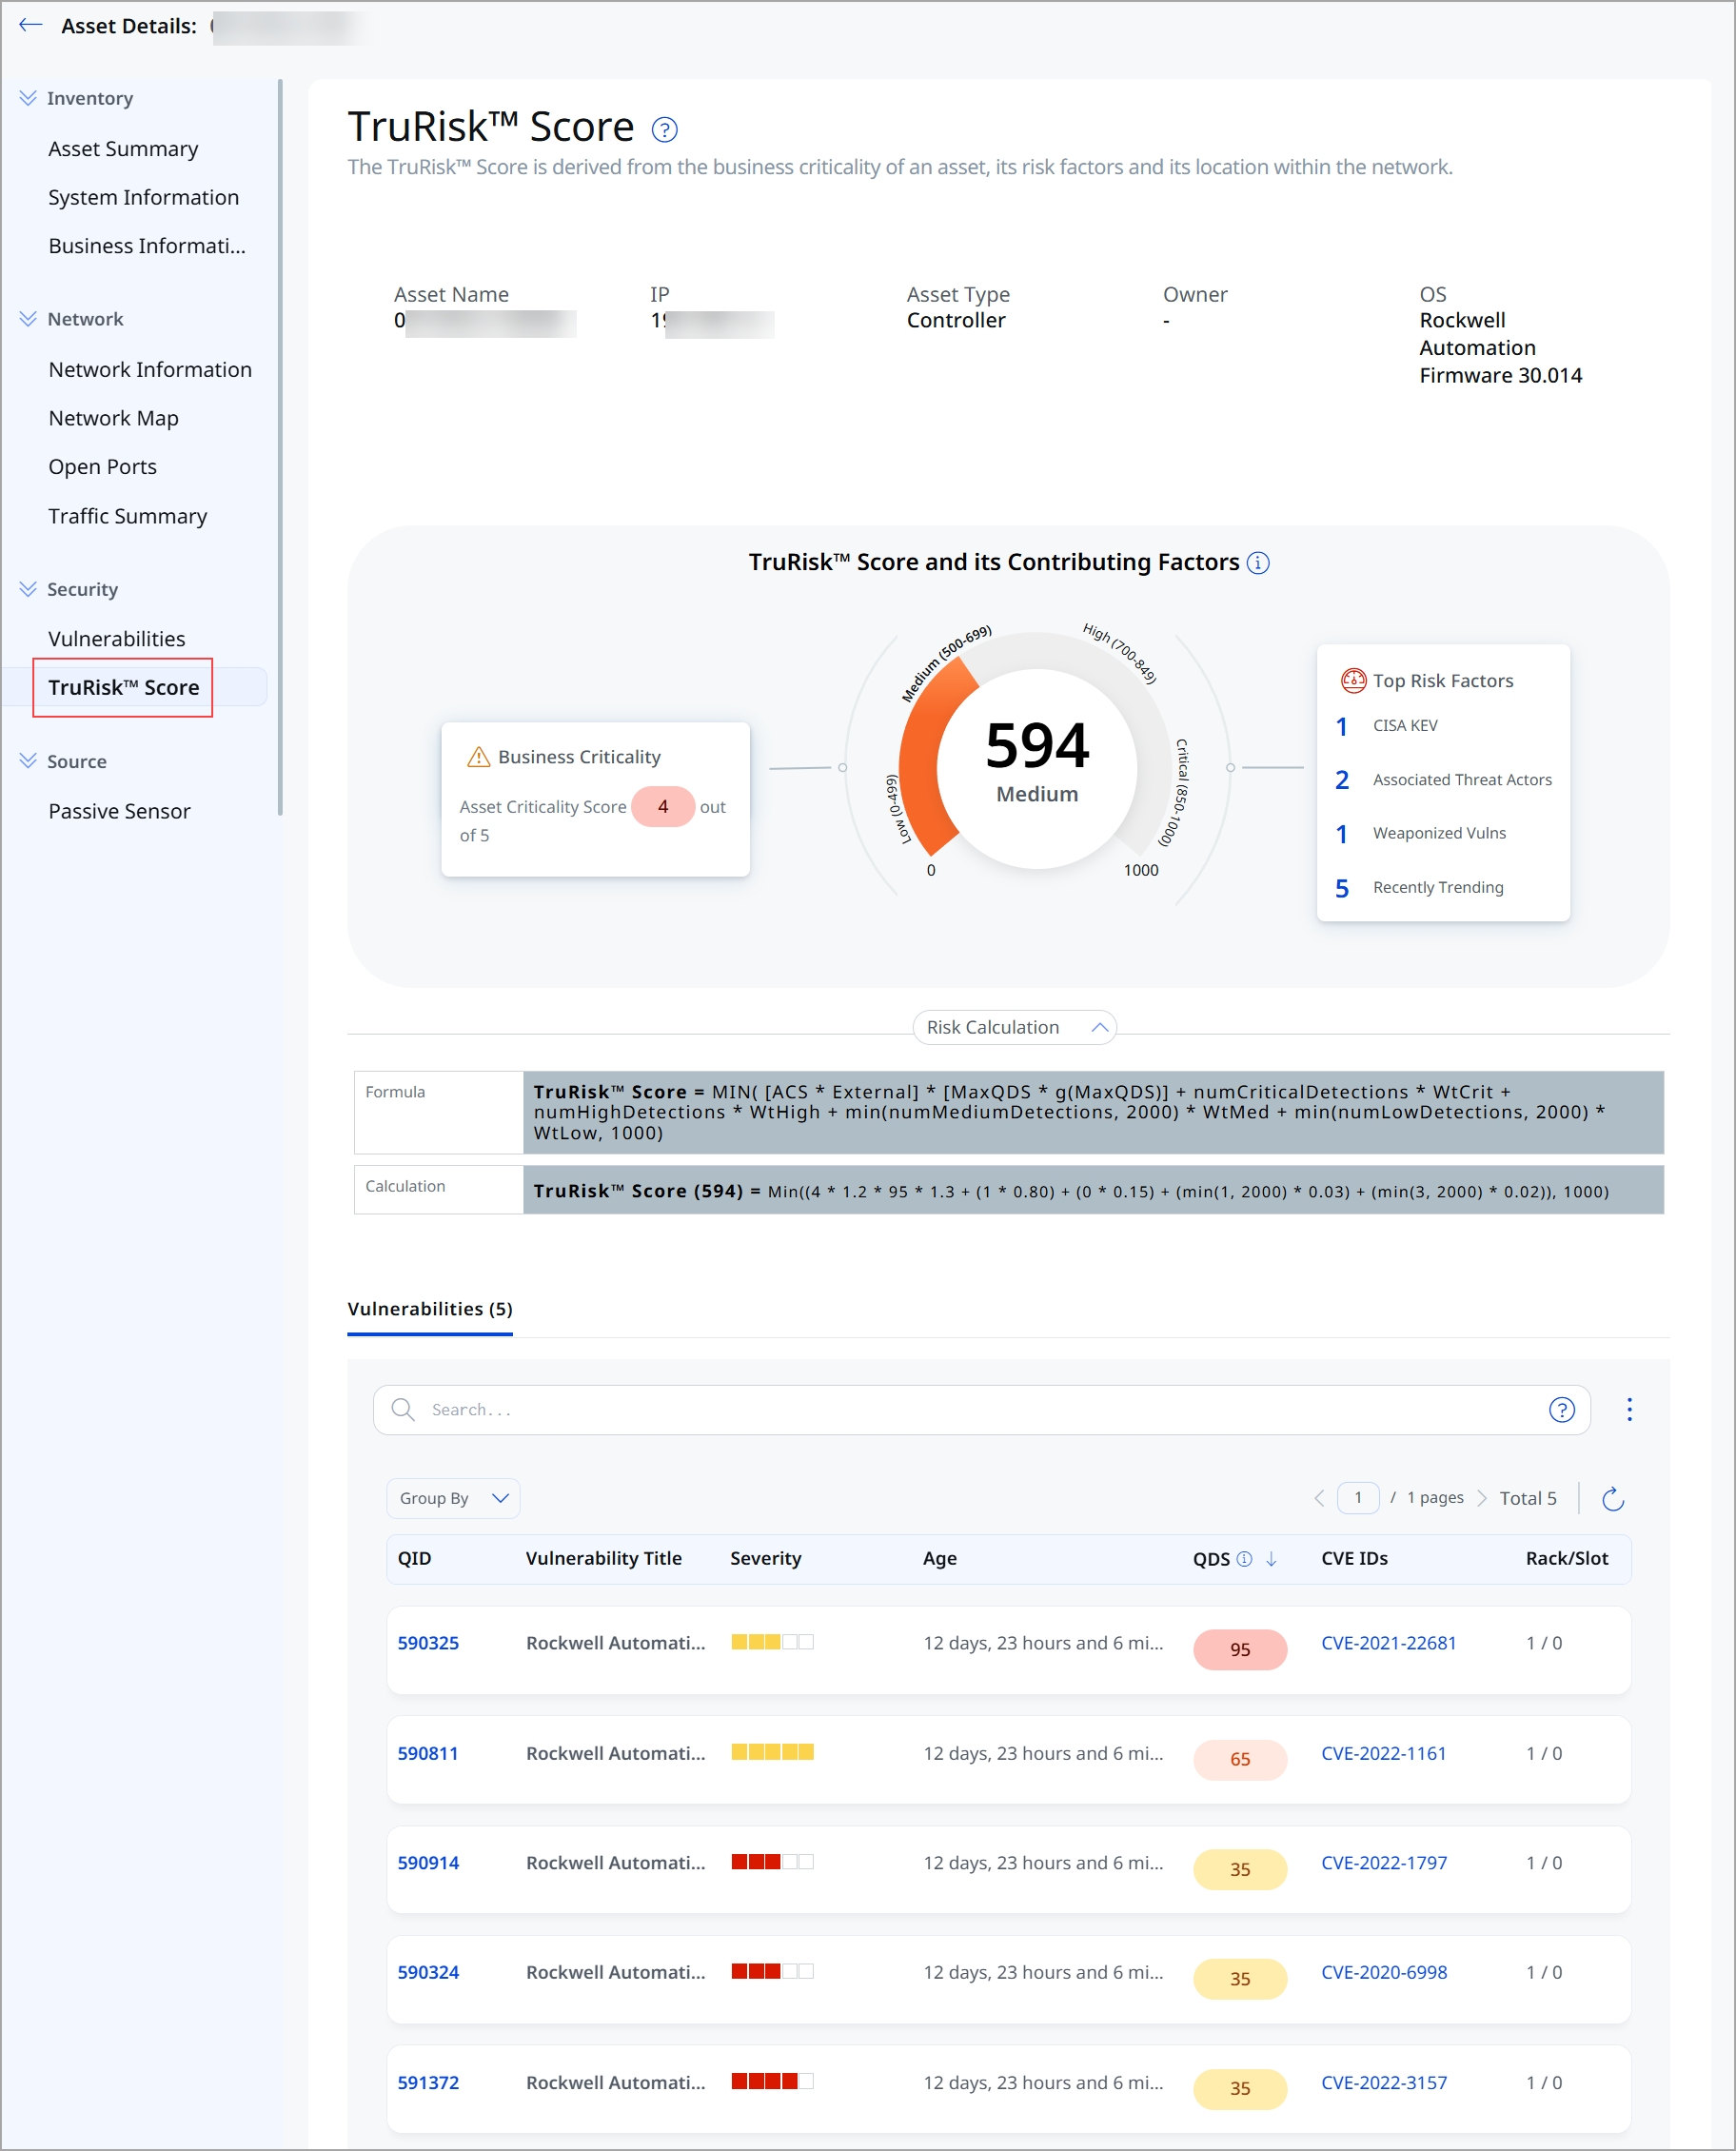
View the TruRisk™ Score and the top contributing risk factors to better understand an asset's overall security risk and prioritize remediation.
You can view the score details on the Asset Details > Security > TruRisk™ Score tab.
Business InformationBusiness Information
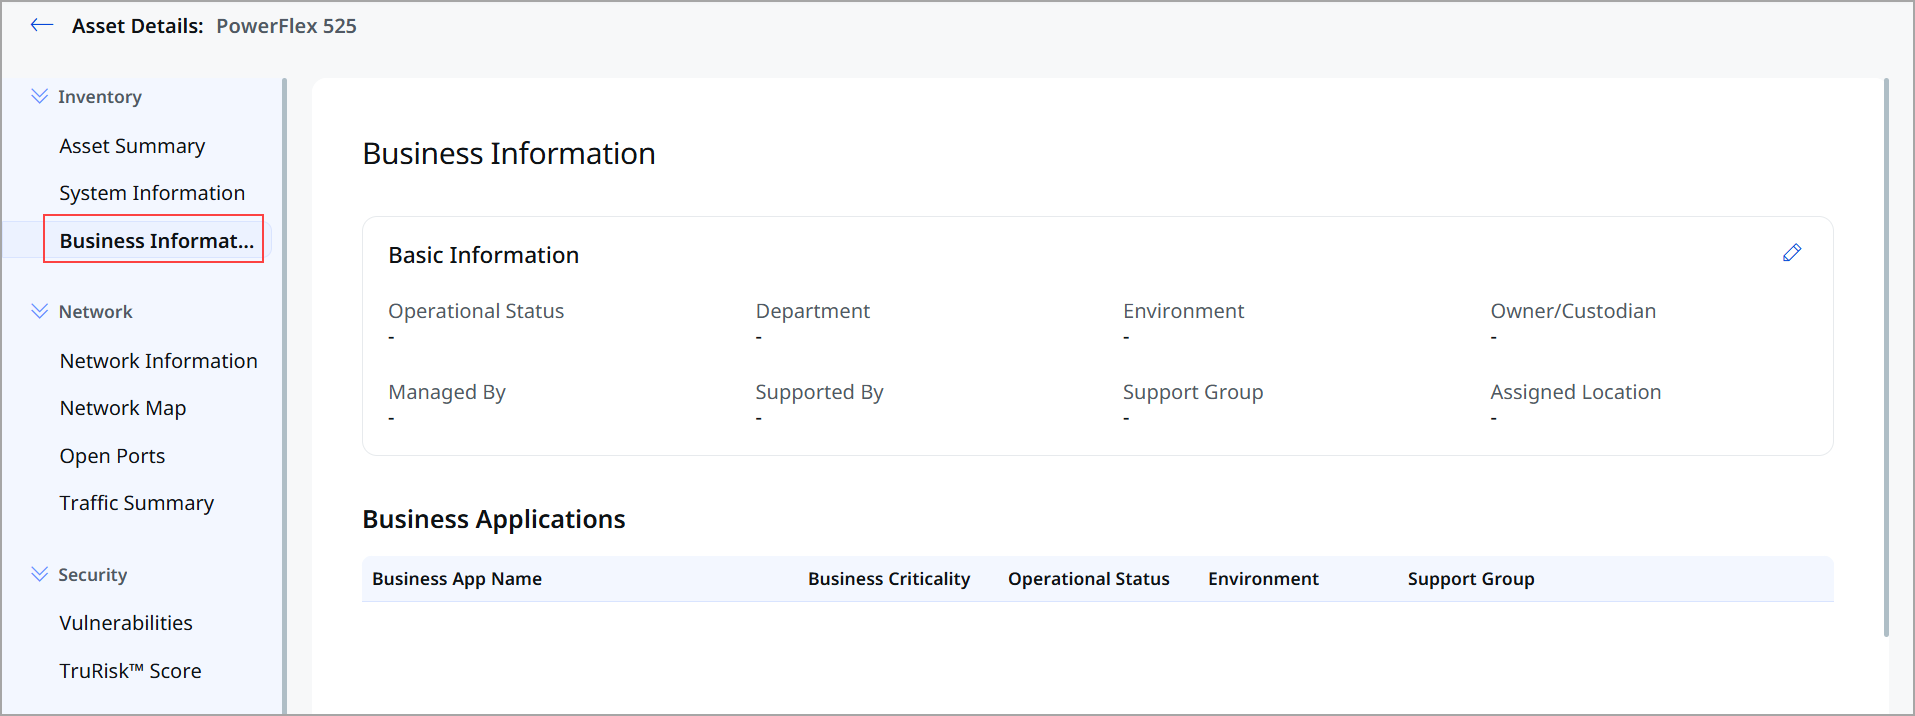
Assess the business impact and business criticality of an asset based on the business context associated with the asset, such as the business owner, business environment, and other organizational attributes.
You can view this business-related information on the new Asset Details > Business Information tab.
For more information on these new asset details, refer to VMDR OT Online Help.
Vulnerability Details Enhancements
You can now view additional vulnerability details to better understand the risk and impact of a vulnerability. The Vulnerability Details page includes the following additional information:
Identify the top CVEs contributing to a vulnerability's Qualys Detection Score (QDS) to better understand the factors that affect the score.
To view the QDS details, click QDS Details from the Vulnerability Details page.
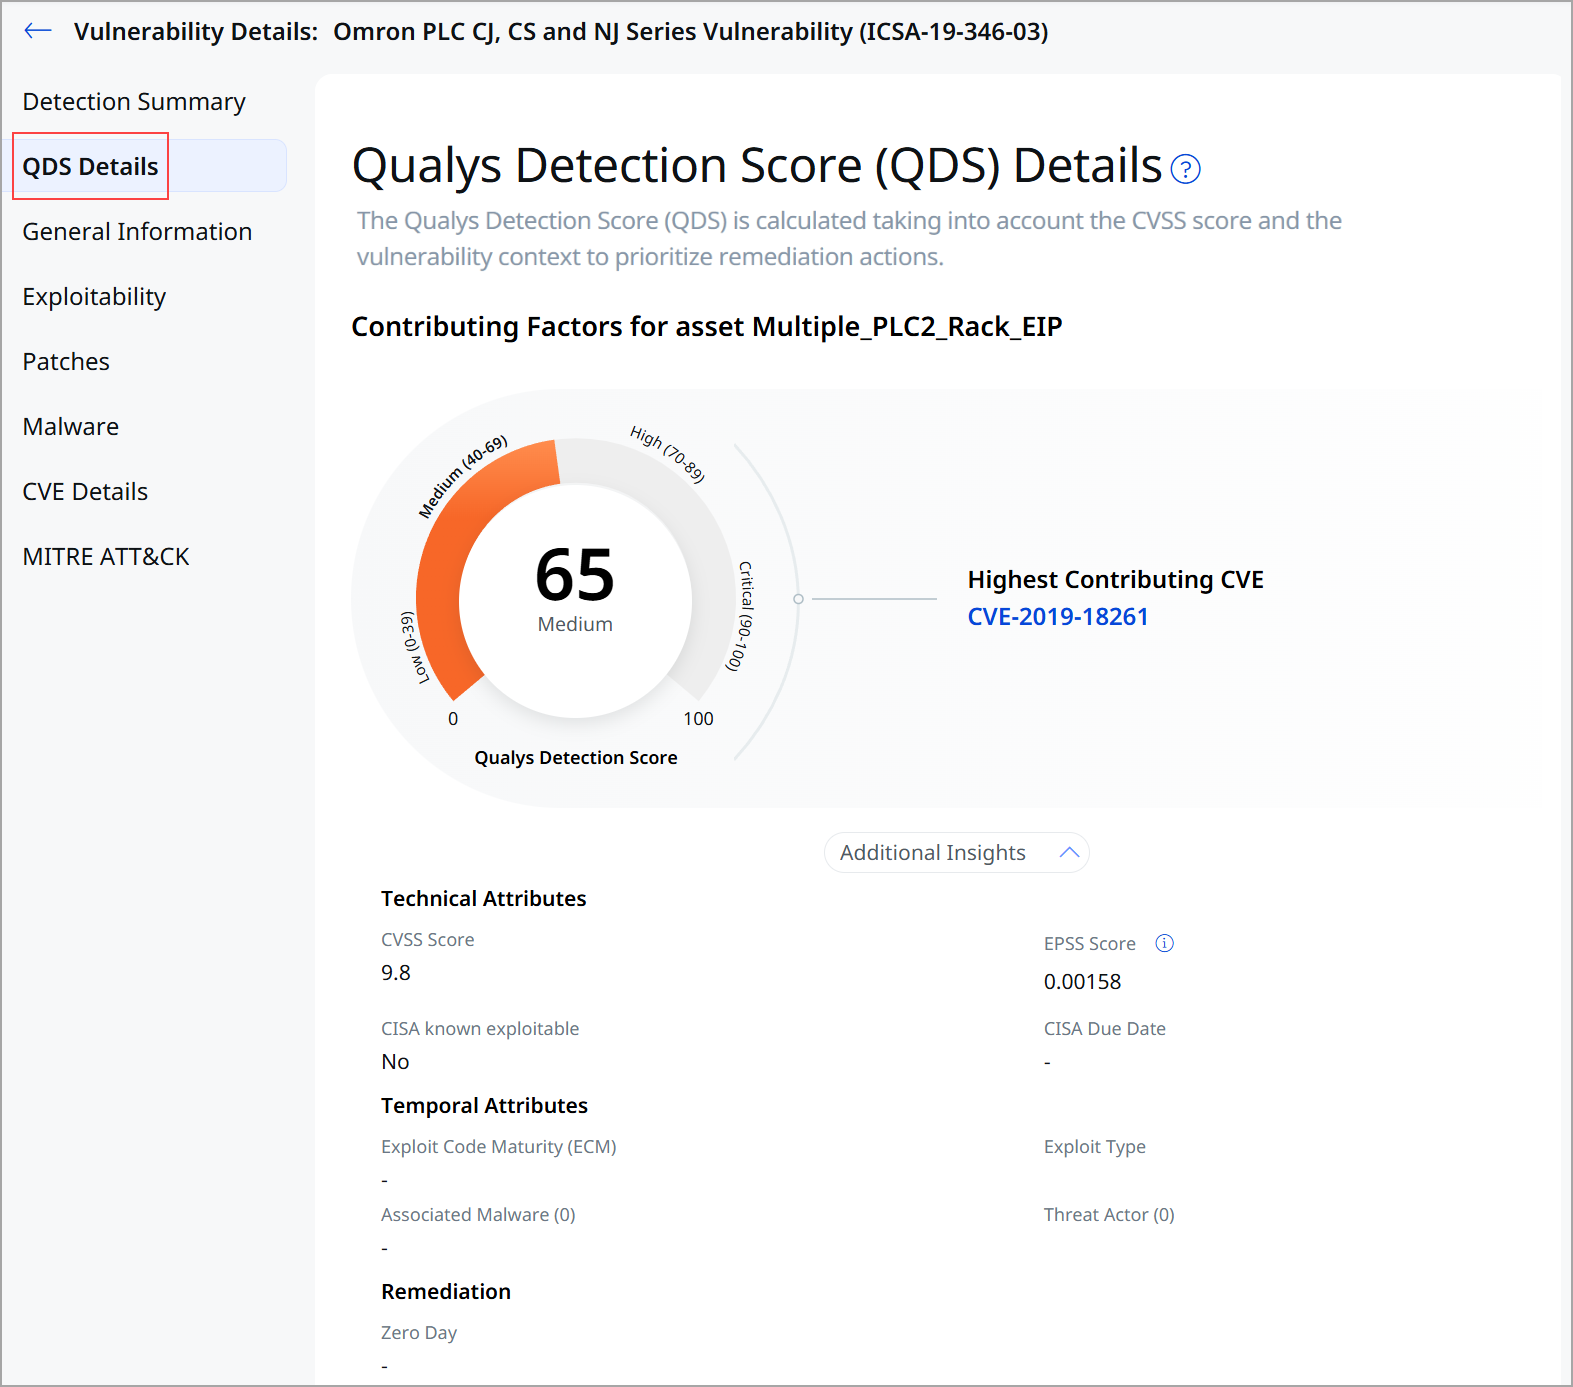
For more information, refer to VMDR OT Online Help.
View all CVEs associated with the selected vulnerability, along with the total number of associated CVEs. The CVEs are listed from the highest to the lowest Qualys Vulnerability Score (QVS), helping you identify the highest-risk CVEs.
To view the CVE details, click CVE Details from the Vulnerability Details page.
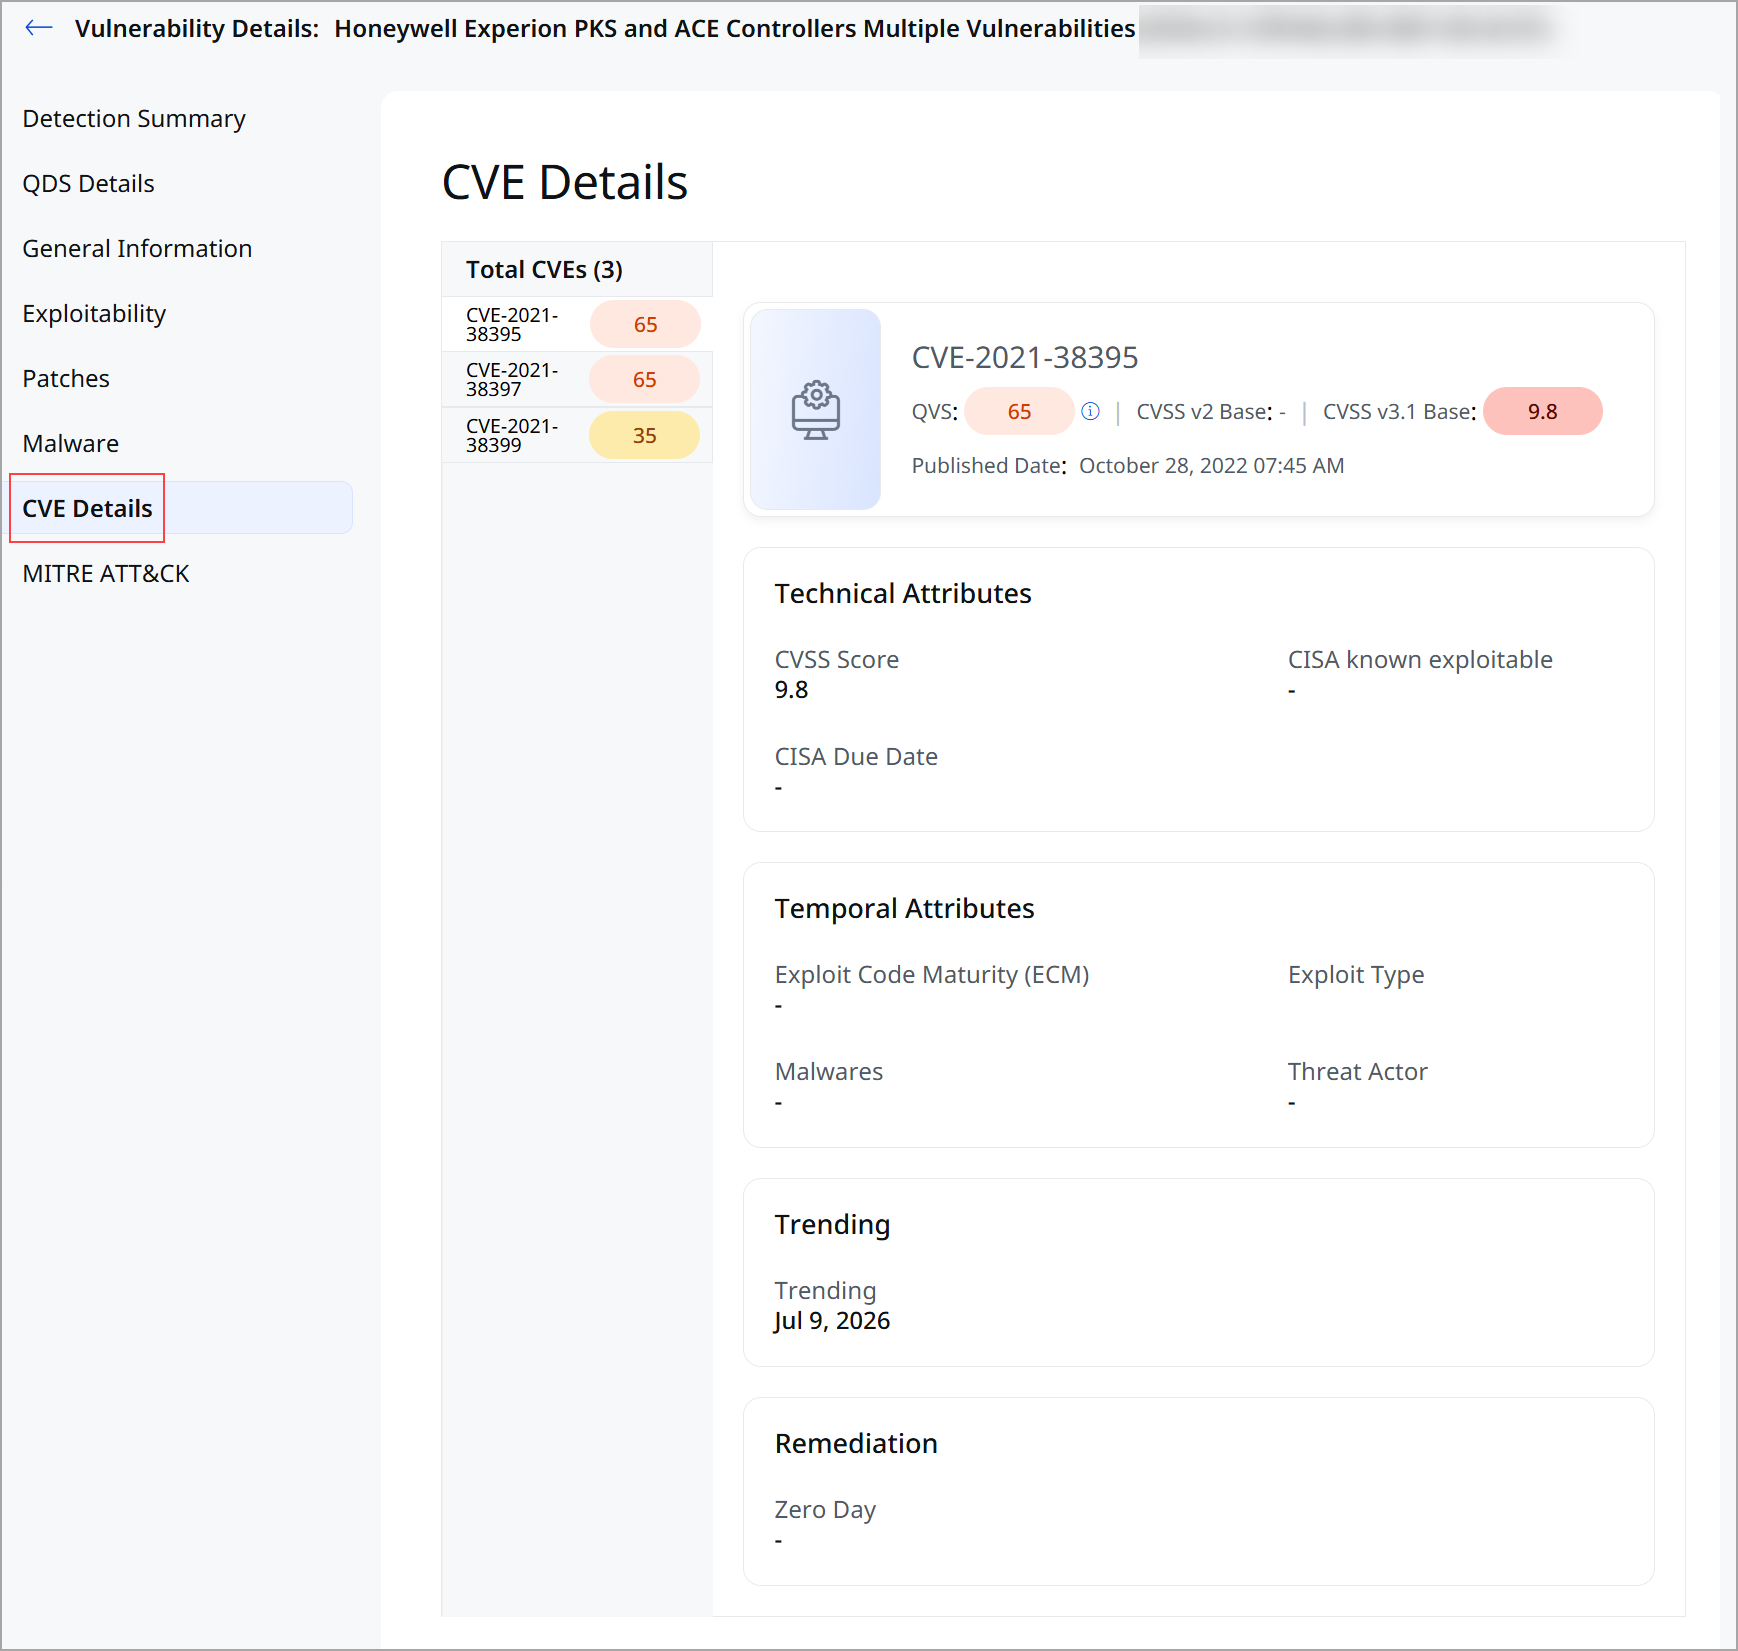
For more information, refer to VMDR OT Online Help.
View the MITRE ATT&CK tactics associated with a vulnerability, providing additional context about the attacker objectives that the vulnerability may enable.
The MITRE ATT&CK framework, developed by MITRE, is a globally recognized knowledge base that categorizes adversary tactics and techniques based on real-world observations. By mapping vulnerabilities to MITRE ATT&CK tactics, you can understand the potential attack lifecycle and prioritize remediation based on attacker behavior.
To view the tactics, click MITRE ATT&CK from the Vulnerability Details page.
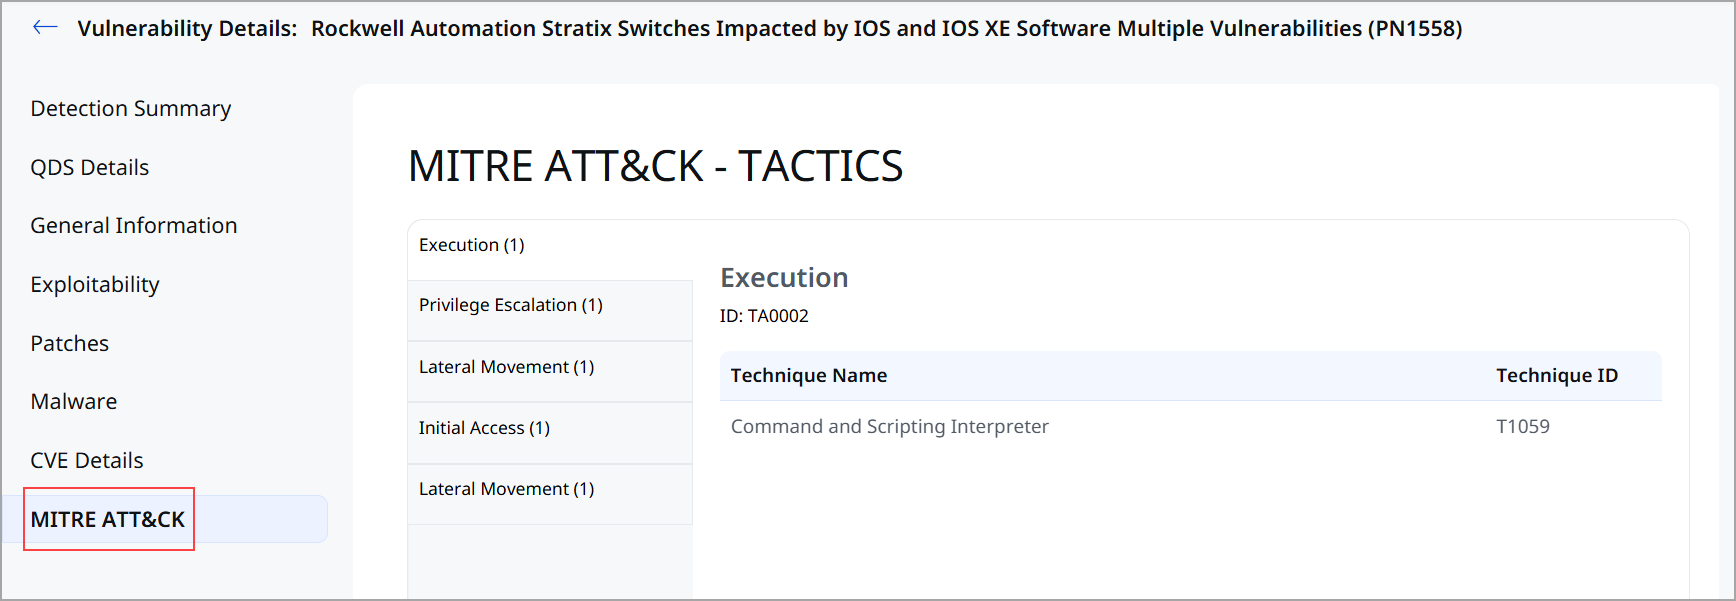
For more information on MITRE ATT&CK tactics, refer to VMDR Online Help.
For more information on these new vulnerability details, refer to VMDR OT Online Help.
Enhancements to VMDR OT Reports
You can now create more comprehensive Asset, Vulnerability, and Monitoring Details reports by including additional TruRisk™, business information, and vulnerability fields in the report. These details provide visibility into asset criticality, business context, and vulnerability risk to help you prioritize remediation effectively.
To view these new fields, navigate to the Reports tab and create a report.
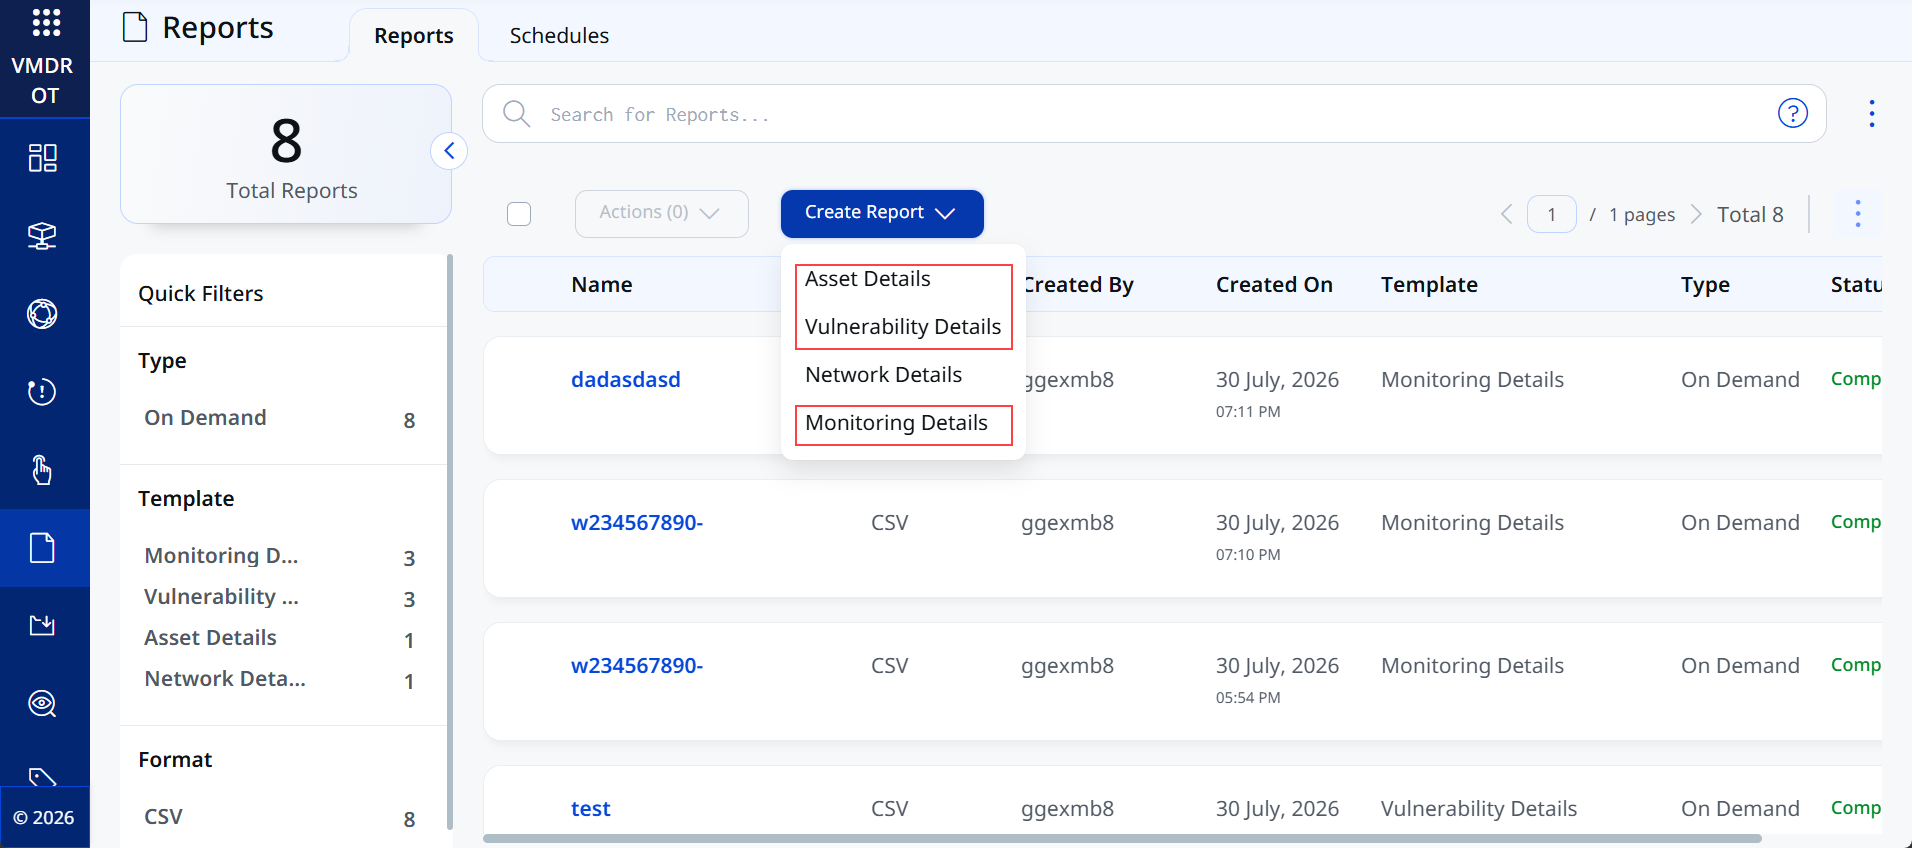
The following new fields are available to select on the Report Display step of report creation:
| Asset Details | Vulnerability Details | Monitoring Details |
|---|---|---|
|
CVE:
QID:
|
|
For more information on these reports, refer to VMDR OT Online Help.
Criticality Score for Tags
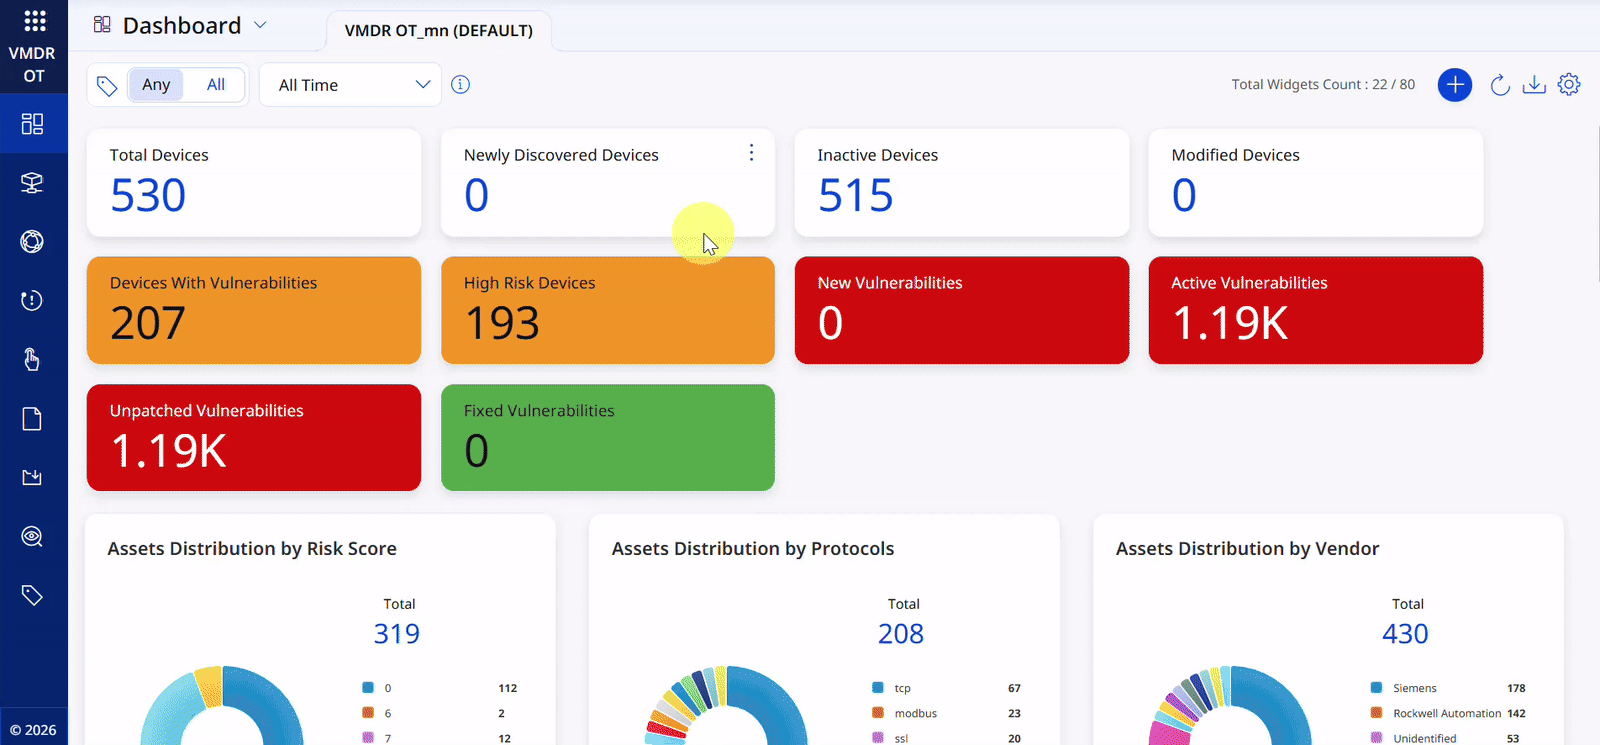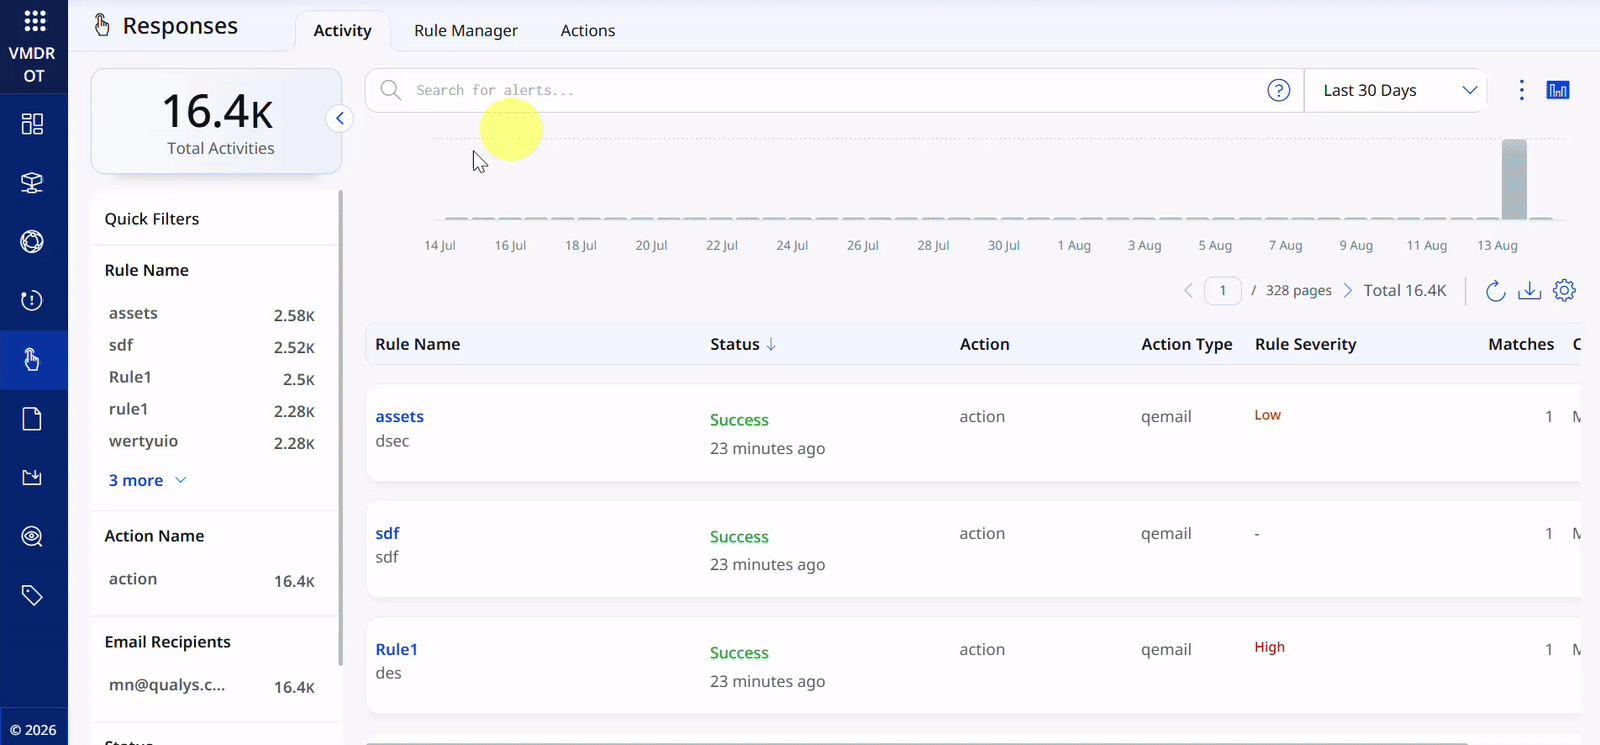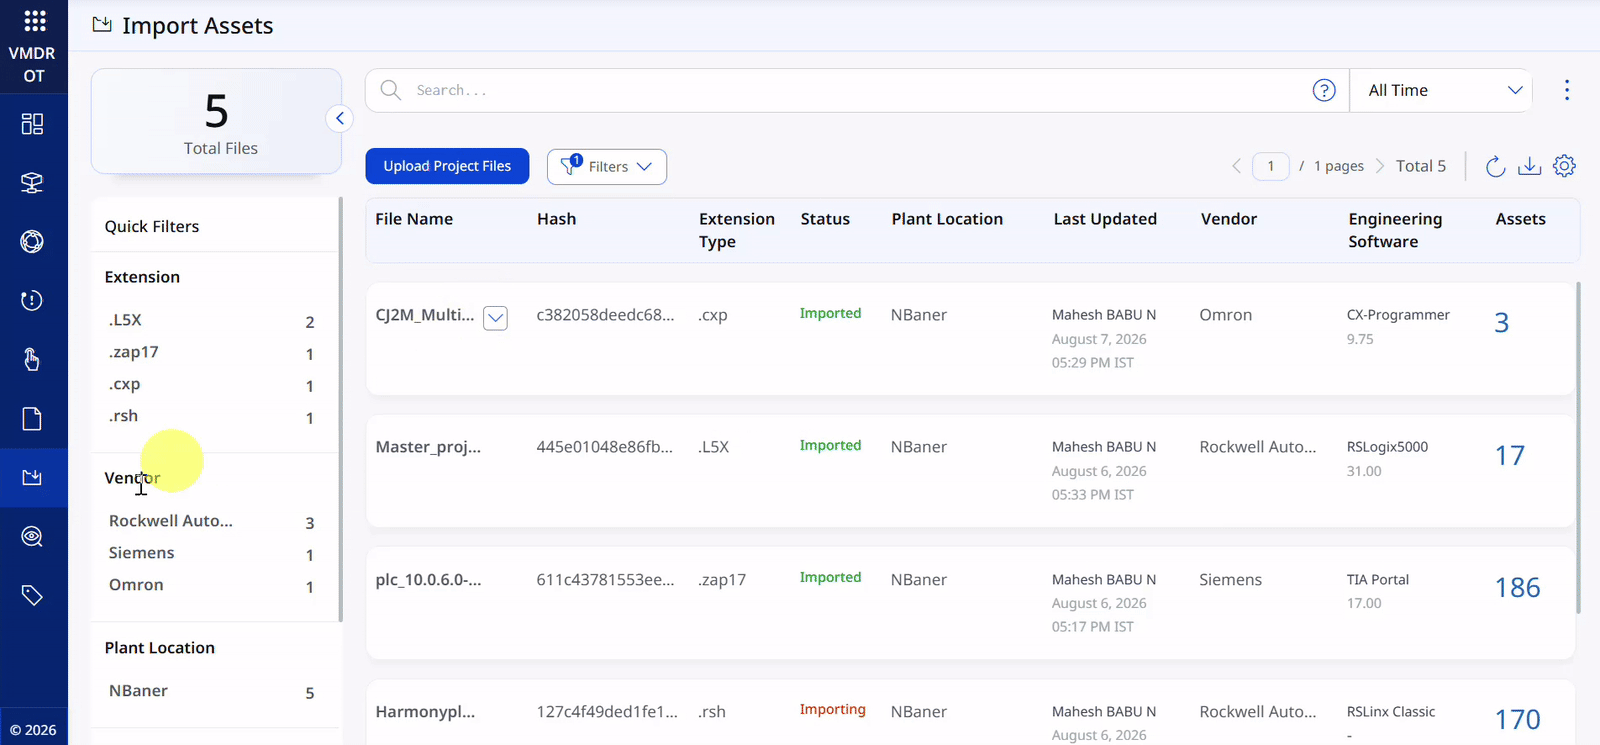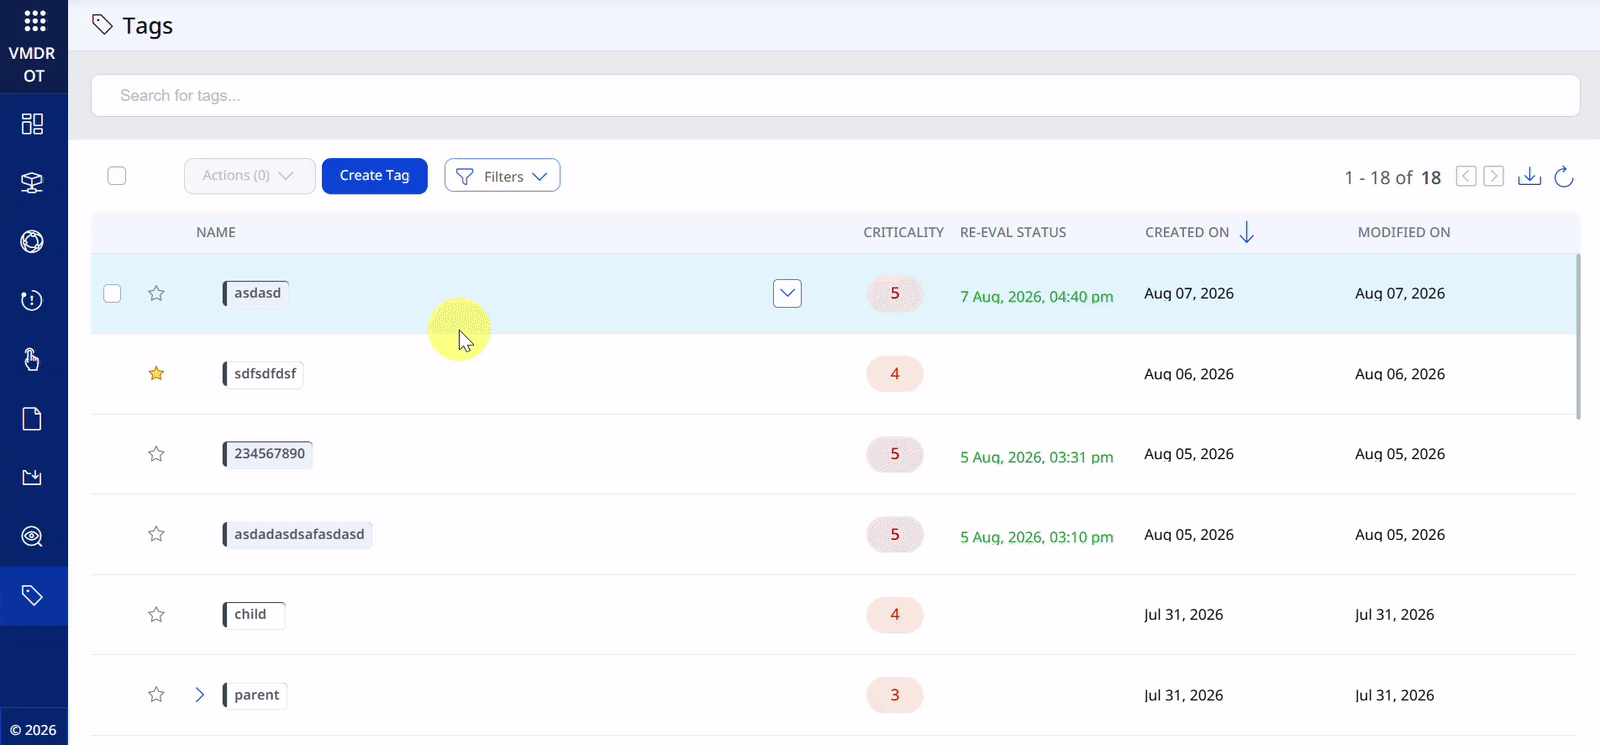
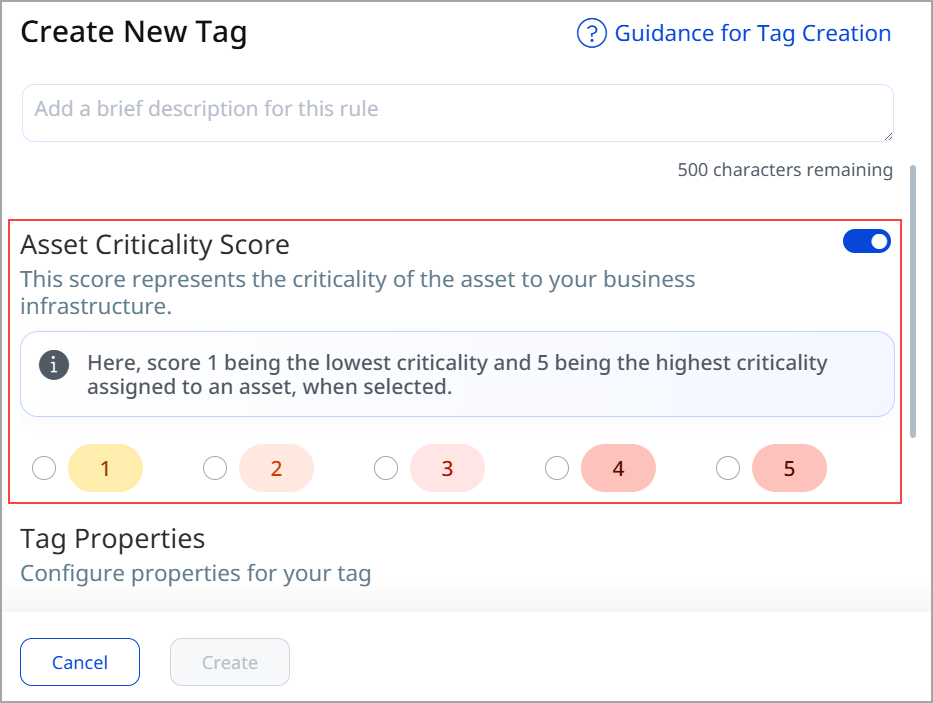
You can now assign an Asset Criticality Score (ACS) to a tag. The assigned score helps the system determine the criticality of assets associated with that tag.
To assign an ACS to a tag, enable the Asset Criticality Score toggle while creating or editing the tag, and then select a criticality score.
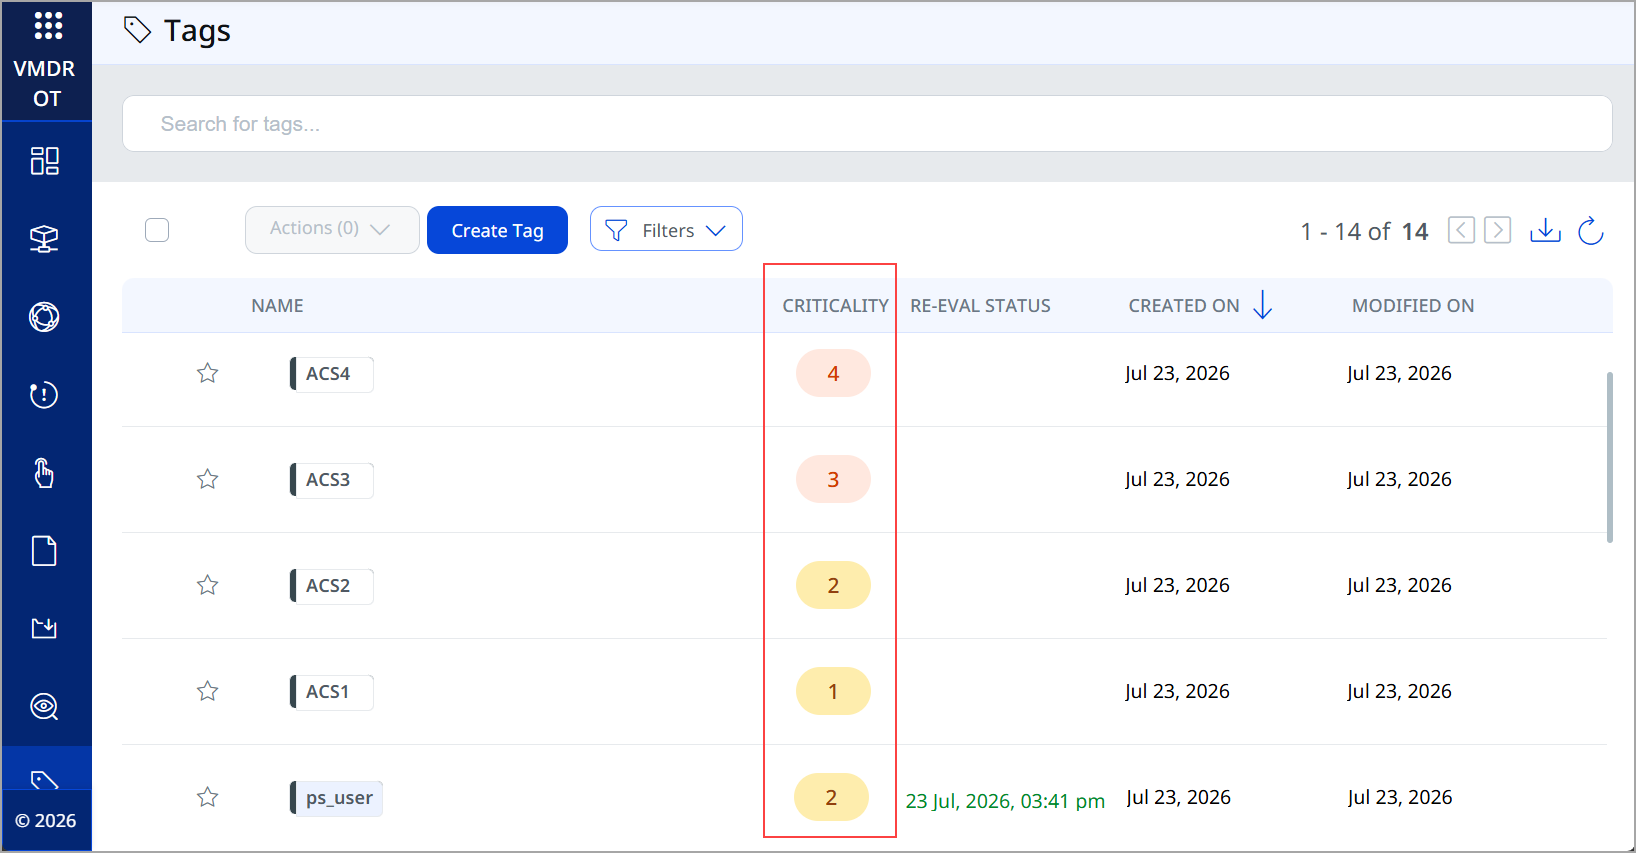
You can view the configured criticality score for each tag on the Tags tab.
For more information tags, refer to VMDR OT Online Help.
Re-evaluation Status for Tags
You can now monitor the progress of the dynamic tag application to affected assets after creating or updating a dynamic tag. The system evaluates the updated tag conditions and applies the tag to all matching assets.
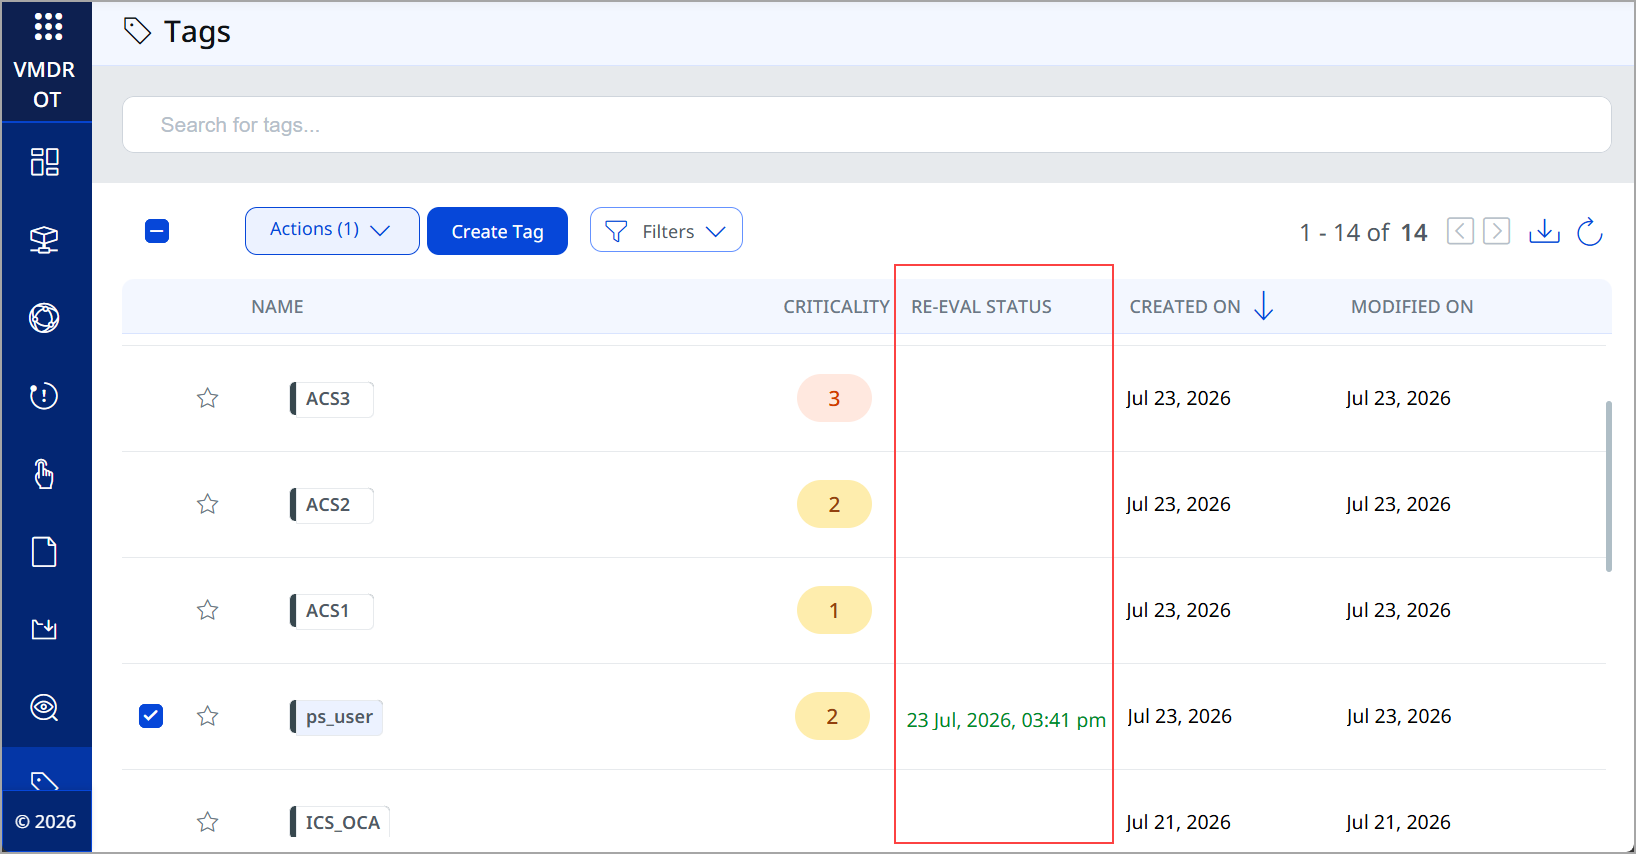
The new RE-EVAL STATUS column on the Tags tab displays the current re-evaluation status. Once the re-evaluation is complete, the column also displays the completion timestamp. Hover over the timestamp to view the status.
The RE-EVAL STATUS is displayed only for dynamic tags created with the Evaluate Rule on Creation checkbox selected.
The following statuses are displayed for tags under re-evaluation:
- In Progress: The system is currently evaluating assets against the updated tag conditions.
- Completed: Re-evaluation is complete, and the latest tag changes are applied to all applicable assets.
For more information, refer to VMDR OT Online Help.
Tag-based User Scoping for PIM Events and Network Traffic
You can now view Process Integrity Monitoring (PIM) events and Network Traffic only for the assets within your assigned tag scope. This ensures that you can access only the data for assets you are authorized to manage.
A user with the Manager role can define each user's scope by assigning tags to assets and adding those tags to the user's tag scope in the Qualys Administration application.
The manager role has unrestricted access to all assets, regardless of any tags applied to them.
For more information about tag-based user scoping, refer to VMDR Online Help.
New QQL Tokens
The following new QQL tokens are added in this release:
| Token | Tab | Description |
|---|---|---|
| source.passiveSensor.id | Network | Use this token to search network traffic by the passive sensor ID associated with the source asset.
Example:
|
| destination.passiveSensor.id | Network | Use this token to search network traffic by the passive sensor ID associated with the destination asset.
Example:
|
| asset.criticalityScore | Assets | Use this token to search assets based on their Criticality Score.
Example:
|
| asset.truRisk | Assets | Use this token to search assets based on their TruRisk™ score.
Example:
|
| asset.businessInfo. environment |
Assets | Use this token to search assets by their business environment.
Example:
|
| asset.businessInfo. managedBy.username |
Assets | Use this token to search assets by the username of the user responsible for managing the asset.
Example:
|
| asset.businessInfo. operationalStatus |
Assets | Use this token to search assets by their operational status.
Example:
|
| asset.businessInfo. ownedBy.username |
Assets | Use this token to search assets by the username of the asset owner.
Example:
|
| asset.businessInfo. supportGroup |
Assets | Use this token to search assets by the support group assigned to the asset.
Example:
|
| asset.businessInfo. supportedBy.username |
Assets | Use this token to search assets by the username of the user providing support.
Example:
|
| asset.businessInfo. department |
Assets | Use this token to search assets by the associated business department.
Example:
|
| asset.businessInfo. company |
Assets | Use this token to search assets by the company name associated with the asset.
Example:
|
| finding.qds | Vulnerabilities | Use this token to search vulnerabilities by their Qualys Detection Score (QDS).
Example:
|
| finding.riskFactor. cisaKEVDueDate |
Vulnerabilities | Use this token to search CISA known exploited vulnerabilities whose remediation due date is as per the CISA Catalog.
Example:
|
| finding.riskFactor. isCisaKnownExploit |
Vulnerabilities | Use this token to search vulnerabilities based on whether they are listed in the CISA Known Exploited Vulnerabilities (KEV) catalog.
Example:
|
| finding.riskFactor. exploitCodeMaturity |
Vulnerabilities | Use this token to search for vulnerabilities that can be exploited based on the existing state of exploit techniques and code availability.
Example:
|
| finding.riskFactor. exploitType |
Vulnerabilities | Use this token to search vulnerabilities based on the type of exploits and their related vulnerabilities.
Example:
|
| finding.riskFactor. malwareName |
Vulnerabilities | Use this token to search vulnerabilities associated with malware.
Example:
|
| finding.riskFactor.rti | Vulnerabilities | Use this token to search vulnerabilities with Real-Time Threat Indicators (RTIs).
Example:
|
| finding.riskFactor. threatActorName |
Vulnerabilities | Use this token to search vulnerabilities associated with a specific threat actor.
Example:
|
| finding.riskFactor. trending |
Vulnerabilities | Use this token to search vulnerabilities that are trending within a specific date range.
Example:
|
For more information on these tokens, refer to VMDR OT Online Help.
Issue Addressed
The following reported and notable customer issue is fixed in this release.
| Component/Category | Description |
|---|---|
|
VMDR OT - Asset Details |
We fixed an issue where the detection age displayed on the Asset Details > Vulnerabilities tab reset every day, even for vulnerabilities detected several days ago. Now, the detection age is correctly displayed for each vulnerability. |