Privilege level for Junos OS
We use Unix authentication for authenticating to Juniper devices with Junos operating system (Junos OS).
This help will describe how to create a custom login class with the least privileges required for scanning, and then associate the scan user account with the custom login class.
Overview
Junos OS allows you to grant access or permissions to the commands and configuration hierarchy levels and statements. This enables users to execute only those commands and configure and view only those statements for which they have access privileges. You can use extended regular expressions to specify which operational mode commands, configuration statements, and hierarchies are denied or allowed for users. This prevents unauthorized users from executing or configuring sensitive commands and statements that could potentially cause damage to the network.
Junos OS uses login classes to assign permissions to groups of users. Each user must be part of a login class. You can define a custom login class with the permissions you want to grant to the scan user account. The account must be configured so that it's able to execute the commands that are required for scanning these devices.
Commands required for scanning
For compliance scans:
show interfaces statistics
show configuration|display xml
For vulnerability scans:
show version
cli show version
show bgp summary
cli show bgp summary
show chassis hardware
cli show chassis hardware
Permissions required for scanning
Junos OS provides the following permission flags that you can assign to a login class. Flags that end in -control, and flags such as all, configure, and maintenance, grant read-write or administrative access. Don't assign these flags to the scan user account.
For the least privileges required for scanning, assign only the following read-only flags to the scan user's login class: admin, interface, routing, shell, snmp, system, and view. With these flags, the scan user account can view information but can't modify it.
To assess controls that check authentication secrets, such as NTP authentication keys, RADIUS and TACACS+ secrets, and key chains, also assign the secret flag. For details, see the note that follows the table.
|
Permission flag |
Description |
|---|---|
|
access |
Can view the access configuration in configuration mode and with the show configuration operational mode command. |
|
access-control |
Can view and configure access information at the [edit access] hierarchy level. |
|
admin |
Can view user account information in configuration mode and with the show configuration operational mode command. |
|
admin-control |
Can view user account information and configure it at the [edit system] hierarchy level. |
|
all-control |
Can view user accounts and configure them at the [edit system login] hierarchy level. |
|
all |
Can access all operational mode commands and configuration mode commands. Can modify configuration in all the configuration hierarchy levels. |
|
clear |
Can clear (delete) information learned from the network that is stored in various network databases by using the clear commands. |
|
configure |
Can enter configuration mode by using the configure command. |
|
control |
Can perform all control-level operations—all operations configured with the -control permission flags. |
|
field |
Can view field debug commands. Reserved for debugging support. |
|
firewall |
Can view the firewall filter configuration in configuration mode. |
|
firewall-control |
Can view and configure firewall filter information at the [edit firewall] hierarchy level. |
|
floppy |
Can read from and write to the removable media. |
|
flow-tap |
Can view the flow-tap configuration in configuration mode. |
|
flow-tap-control |
Can view the flow-tap configuration in configuration mode and can configure flow-tap configuration information at the [edit services flow-tap] hierarchy level. |
|
flow-tap-operation |
Can make flow-tap requests to the router or switch. For example, a Dynamic Tasking Control Protocol (DTCP) client must have flow-tap-operation permission to authenticate itself to the Junos OS as an administrative user. Note: The flow-tap-operation option is not included in the all-control permissions flag. |
|
idp-profiler-operation |
Can view profiler data. |
|
interface |
Can view the interface configuration in configuration mode and with the show configuration operational mode command. |
|
interface-control |
Can view chassis, class of service (CoS), groups, forwarding options, and interfaces configuration information. Can edit configuration at the following hierarchy levels:
|
|
maintenance |
Can perform system maintenance, including starting a local shell on the router or switch and becoming the superuser in the shell by using the su root command, and can halt and reboot the router or switch by using the request system commands. |
|
network |
Can access the network by using the ping, ssh, telnet, and traceroute commands. |
|
pgcp-session-mirroring |
Can view the pgcp session mirroring configuration. |
|
pgcp-session-mirroring-control |
Can modify the pgcp session mirroring configuration. |
|
reset |
Can restart software processes by using the restart command and can configure whether software processes are enabled or disabled at the [edit system processes] hierarchy level. |
|
rollback |
Can use the rollback command to return to a previously committed configuration other than the most recently committed one. |
|
routing |
Can view general routing, routing protocol, and routing policy configuration information in configuration and operational modes. |
|
routing-control |
Can view general routing, routing protocol, and routing policy configuration information and can configure general routing at the [edit routing-options] hierarchy level, routing protocols at the [edit protocols] hierarchy level, and routing policy at the [edit policy-options] hierarchy level. |
|
secret |
Can view passwords and other authentication keys in the configuration. |
|
secret-control |
Can view passwords and other authentication keys in the configuration and can modify them in configuration mode. |
|
security |
Can view security configuration in configuration mode and with the show configuration operational mode command. |
|
security-control |
Can view and configure security information at the [edit security] hierarchy level. |
|
shell |
Can start a local shell on the router or switch by using the start shell command. |
|
snmp |
Can view Simple Network Management Protocol (SNMP) configuration information in configuration and operational modes. |
|
snmp-control |
Can view SNMP configuration information and can modify SNMP configuration at the [edit snmp] hierarchy level. |
|
system |
Can view system-level information in configuration and operational modes. |
|
system-control |
Can view system-level configuration information and configure it at the [edit system] hierarchy level. |
|
trace |
Can view trace file settings and configure trace file properties. |
|
trace-control |
Can modify trace file settings and configure trace file properties. |
|
view |
Can use various commands to display current system-wide, routing table, and protocol-specific values and statistics. Cannot view the secret configuration. |
|
view-configuration |
Can view all of the configuration excluding secrets, system scripts, and event options. Note: Only users with the maintenance permission can view commit script, op script, or event script configuration. |
How to create custom login class with permissions for scan user
Follow the steps below to create a custom login class and provide permissions (least privilege) at different hierarchy levels. Then add the scan user account to this class.
1) Create custom login class. In this example, the new custom class is "mytestclass". Here's an example:
[edit system login]
root@pcavmx14# edit class mytestclass ?
Possible completions:
<[Enter]> Execute this command
| Pipe through a command
2) Go to the new custom login class. Here's an example:
[edit system login class mytestclass]
root@pcavmx14# set permissions ?
Possible completions:
[ Open a set of values
access Can view access configuration
access-control Can modify access configuration
admin Can view user accounts
admin-control Can modify user accounts
all All permission bits turned on
clear Can clear learned network info
configure Can enter configuration mode
control Can modify any config
field Can use field debug commands
firewall Can view firewall configuration
firewall-control Can modify firewall configuration
floppy Can read and write the floppy
flow-tap Can view flow-tap configuration
flow-tap-control Can modify flow-tap configuration
3) Use the following command to assign required permissions to the custom login class. You can give multiple permission flags in one command, or use separate commands.
[edit system login class mytestclass]
root@comvmx14# set permissions interface permissions system permissions snmp permissions routing permissions view permissions shell permissions admin
4) Create scan user account and associate it with the custom login class. In the following example, we'll associate the user "scanuser" with the custom class "mytestclass". Note that we've given only read permissions with different permission flags to this class/user. This means the user will not be able to modify information.
[edit system login]
root@comvmx14# set user scanuser class mytestclass
Verify whether the scan user account needs the secret permission
Some controls check authentication secrets, such as NTP authentication keys, RADIUS and TACACS+ secrets, and key chains. To assess these controls accurately, the scan user's login class needs the secret permission flag. Use the following steps to compare scan results with and without this flag.
1) Create two login classes: one without the secret permission and one with it.
Login class without the secret permission:
configure
set system login class qualys-min permissions view
set system login class qualys-min permissions view-configuration
commit and-quit
Login class with the secret permission:
configure
set system login class qualys-full permissions view
set system login class qualys-full permissions view-configuration
set system login class qualys-full permissions secret
commit and-quit
2) Create two test user accounts and assign each one to a login class. When prompted, enter a password for each account.
configure
set system login user scan_min class qualys-min authentication plain-text-password
set system login user scan_full class qualys-full authentication plain-text-password
commit and-quit
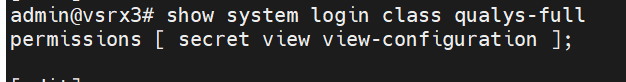
3) Verify that each login class has the required permissions.
show system login class <class-name>
For example, the output for the qualys-full class lists the secret, view, and view-configuration permissions:
4) In Qualys, create two Unix authentication records: one for the scan_min user and one for the scan_full user.
5) Run two compliance scans that include the controls that check authentication secrets:
- Scan 1: Use the authentication record for the scan_min user.
- Scan 2: Use the authentication record for the scan_full user.
6) Compare the results. If the controls fail, return insufficient data, or return different results with the scan_min user but work correctly with the scan_full user, add the secret permission flag to the scan user's login class.