Deep Scan Configuration
Deep Scan is an advanced scanning capability that detects vulnerabilities in non-standard binaries and software that fall outside typical system formats, locations, and behaviors.
Traditional vulnerability scanning methods (IP-based and agent-based) target well-known file locations, executable formats, and standardized software packages. Custom-built tools, standalone executables, and software installed in non-default directories remain unscanned, creating blind spots in your security posture. Deep Scan addresses these visibility gaps by:
- Scanning non-standard binaries and custom software installations.
- Supporting custom file directory specifications.
- Scanning across multiple system drives.
Platform Requirements
Deep Scan is available on the following application versions and platforms:
| Required Application Version | Enterprise TruRisk™ Platform 3.20.1.0 and later Vulnerability Management, Detection and Response 2.3.0 and later |
| Platform Support | Windows OS Deep Scan is currently supported only for Windows assets. Support for Linux assets will be added in a future release. |
Deep Scan is supported on Cloud Agent for Windows 6.2 and later versions.
Current Scope
The following are not in scope for Deep Scan currently:
- Software and application packages discovered during a deep scan are not displayed in the Asset Inventory.
- Deep Scan does not support vulnerability detection for APIs and reporting.
Configuring Deep Scan
To configure the Deep Scan settings, navigate to the Configuration Profile > New Profile > Scan Configuration. Under the Vulnerability Management section, select the Deep Scan checkbox. You can configure the following settings for the Deep Scan. You can configure the following settings for the Deep Scan.
Data Collection Interval
The data collection interval sets the time lapse between the completion of the previous scan and the start of the next scan.
Range: 1440-43200 Minutes. The default value is 10080.
Scan Delay
This is the time added to the start of scanning, both for new installs and for interval scanning. Enter the time in minutes to delay the start of a scan.
Range: 0-1440 Minutes. The default value is 0.
Scan Randomize
The range of randomization added to the scan delay to offset scanning. For example, if the randomization range is 60 minutes, then a random number between 1 and 60 is calculated and used to delay the start of the next scanning interval. A value of 0 (zero) means no randomization added.
Range: 0-1440 Minutes. The default value is 0.
Scan Timeout
Configure the maximum duration for the deep scan. If the scan exceeds the defined time, it is terminated.
Range: 120-1440 Minutes. The default value is 1440 minutes.
Maximum CPU Usage
Configure the maximum CPU consumption allowed for the deep scan. You may observe the momentary spikes in CPU usage.
Range: 10-99%. The default value is 30%.
Windows Profile Settings
Provide the following details to define the scan scope for Windows assets:
- Directories to be included: Enter the comma-separated list of directories/files for Windows assets to be included in the deep scan. By default, C:\ directory is included for the deep scan.
You can only add the absolute path for the directories. Wildcard characters and regular expressions are not supported for specifying the directories/files.
We recommend you add only the specific directories to be included in the deep scan to reduce the memory consumption and CPU usage. - Include all Local Drives: Select this checkbox to include all the local drives in the deep scan scope.
- Directories to be excluded: Enter the comma-separated list of directories/files for Windows assets to be excluded from the deep scan. By default, the following directories are excluded from the deep scan scope: C:\Windows, C:\System Volume Information, C:\$RECYCLE.BIN, C:\hiberfil.sys, C:\pagefile.sys, C:\swapfile.sys
You must define the directories to be included in the deep scan scope for the Windows platform. You cannot create a deep scan configuration profile without including directories. You can also define the deep scan scope by selecting the Include all Local Drives checkbox.
Understanding CPU Throttling for Cloud Agent and Deep Scan
Cloud Agent and Deep Scan each manage CPU usage independently. Their throttling mechanisms work differently:
- Cloud Agent: Utilizes a custom throttling method that limits total CPU usage across all CPU cores.
- Deep Scan: Utilizes job object-based throttling, which limits CPU usage per logical processor.
For example, if both processes are configured to use 20% of the CPU on an 8-core system, the Cloud Agent could utilize up to 20% of the total system CPU (roughly 1.6 cores). Deep Scan, if single-threaded, would use 20% of one core. On an 8-core system, this is displayed to be only about 2.5% of the total CPU usage.
As the CPU limits for Cloud Agent and Deep Scan are independently throttled, their CPU usage does not overlap. Combined usage in this example could reach roughly 22.5%, not just 20%.
Viewing Deep Scan Results
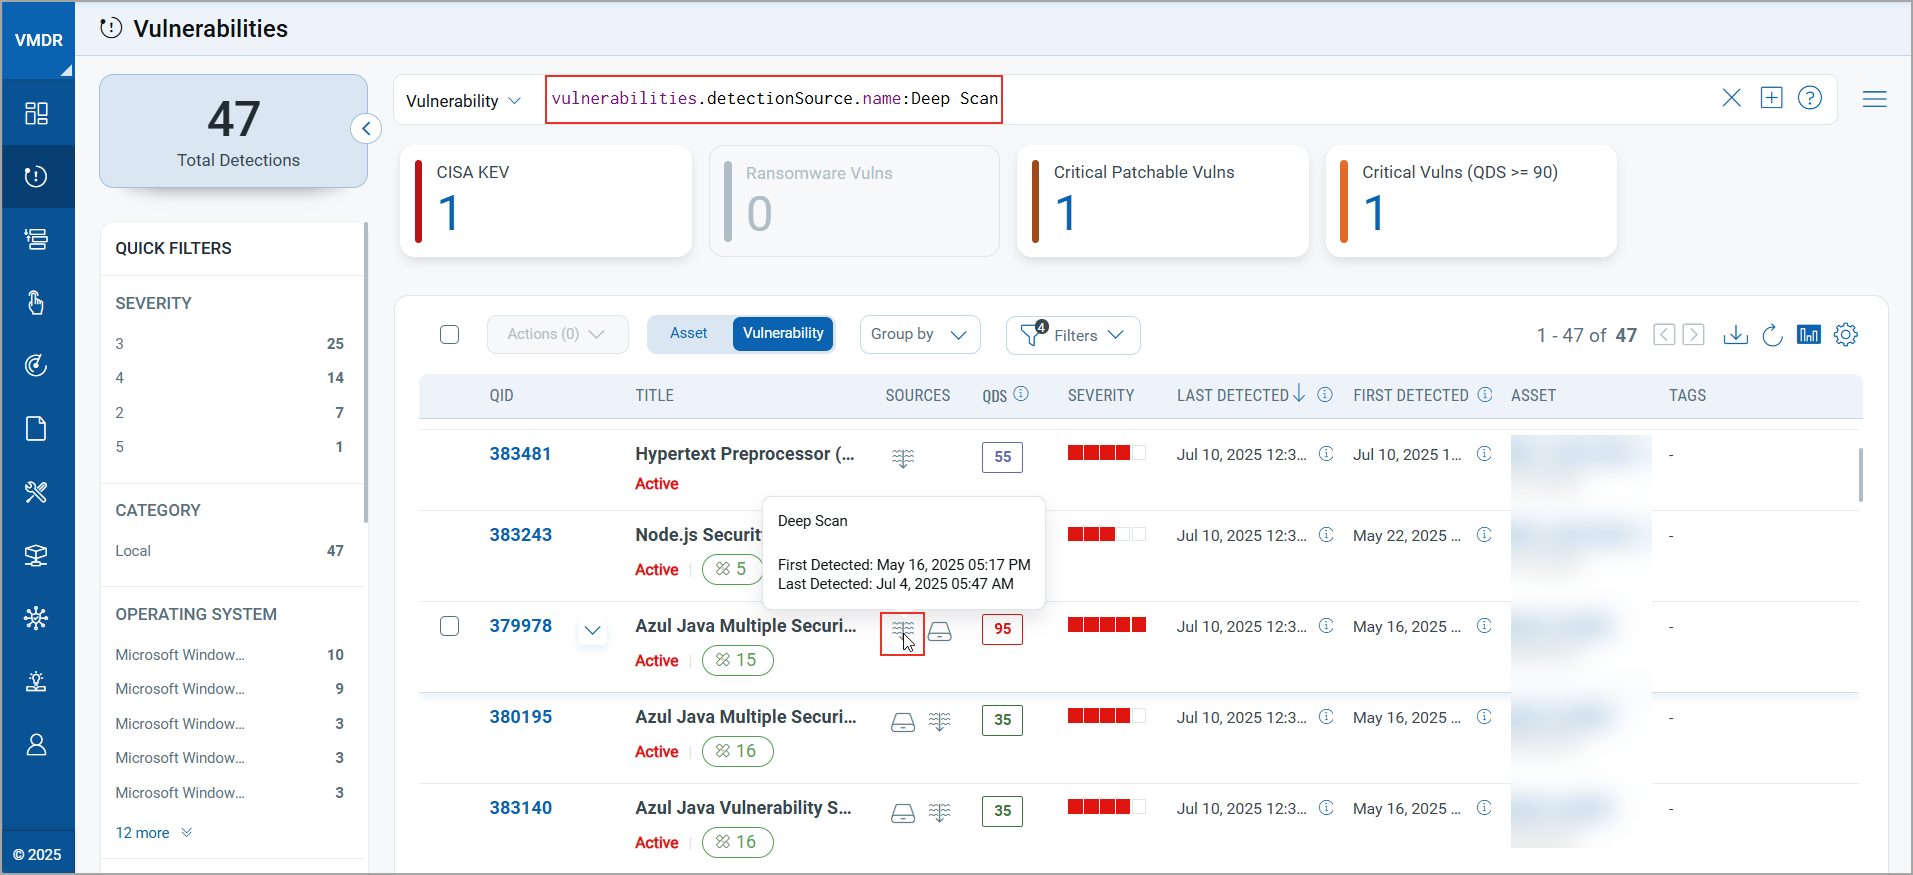
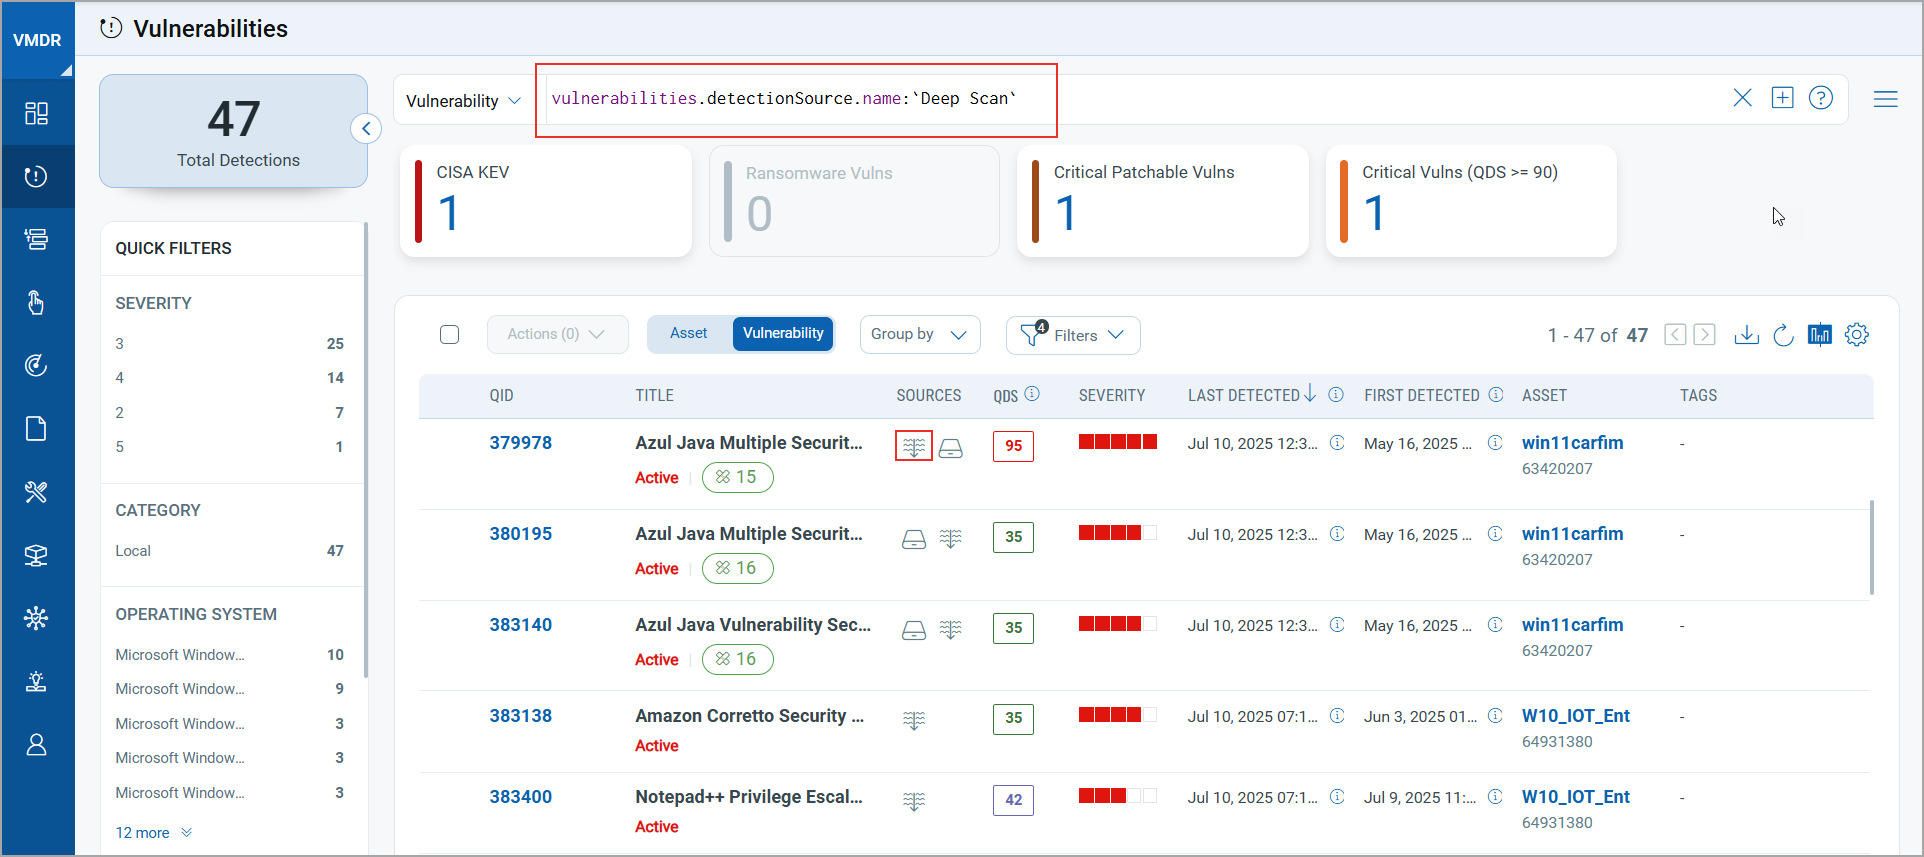
The Deep Scan results are displayed in the Vulnerability Management Detection and Response module. To filter the vulnerabilities detected by Deep Scan, you can either use the search token or the Vulnerabilities Detection Sources Group By filter.
Filtering Using the Search Token
- In the Vulnerability Management Detection and Response module, navigate to the Vulnerabilities tab.
- Ensure Vulnerability is selected in the dropdown next to the Search field.
- In the Search field, enter the QQL token:
vulnerabilities.detectionSource.name: Deep Scan, and then press Enter.
The results display vulnerabilities detected by deep scan. You can also hover on the Source icon to see the first and last detected information in a tooltip.
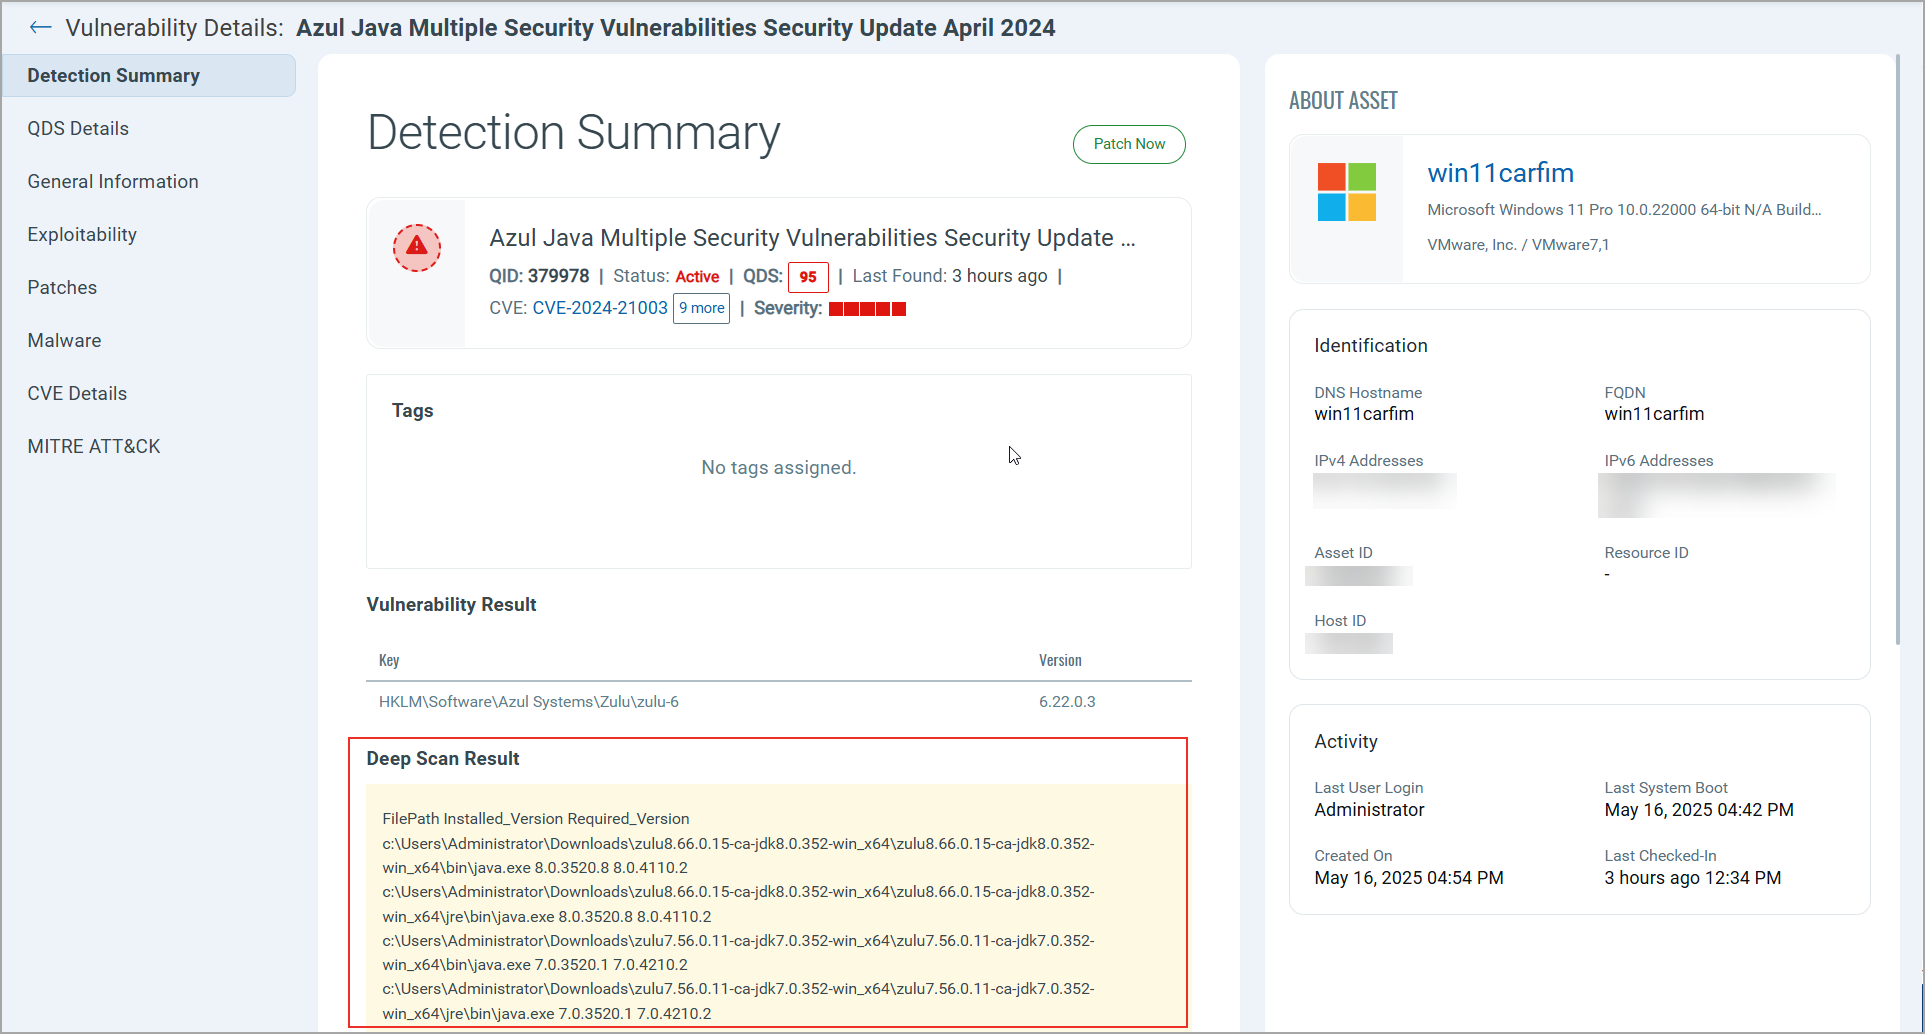
- Click a QID.
- In Vulnerabilities Details > Detection Summary, scroll to the Vulnerability Result section > Deep Scan Result.
Filtering Using the Group By Filter
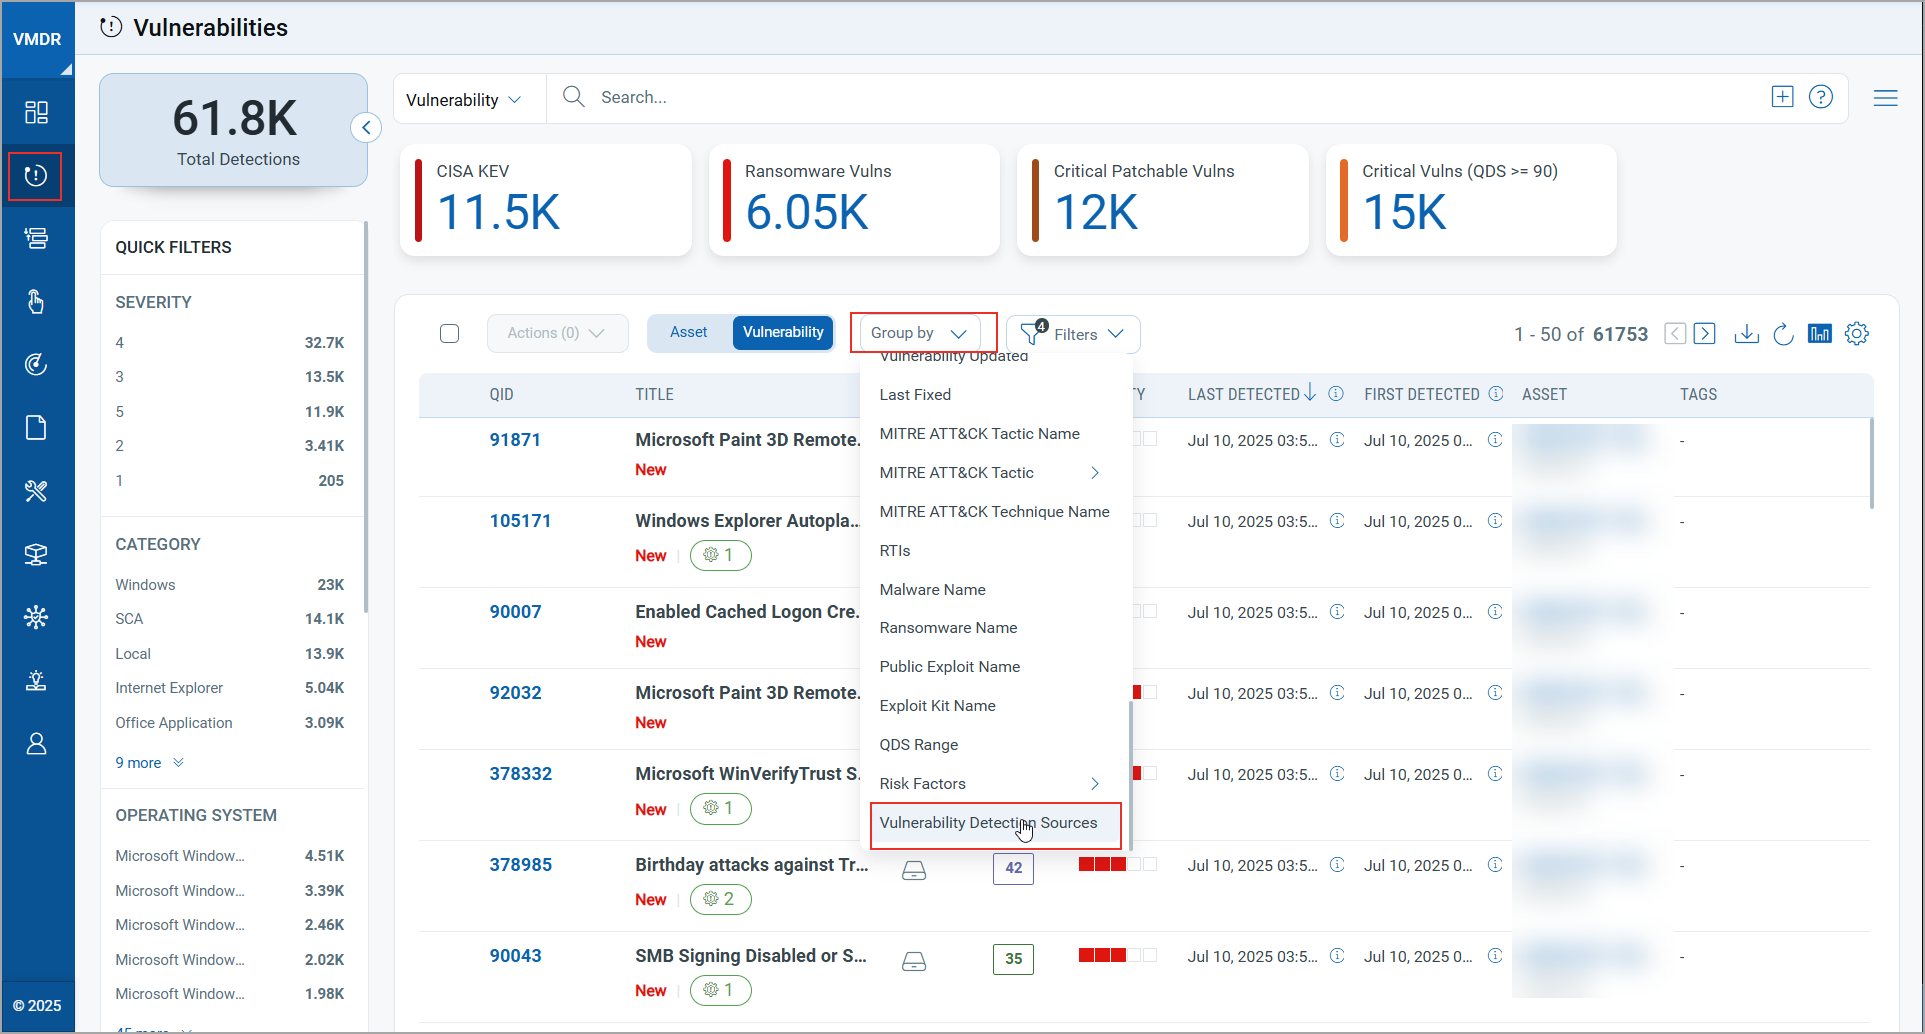
- In the Vulnerability Management Detection and Response module, navigate to the Vulnerabilities tab.
- In the Group By filter, select the Vulnerabilities Detection Sources filter.
- In the detection sources list, click Deep Scan.
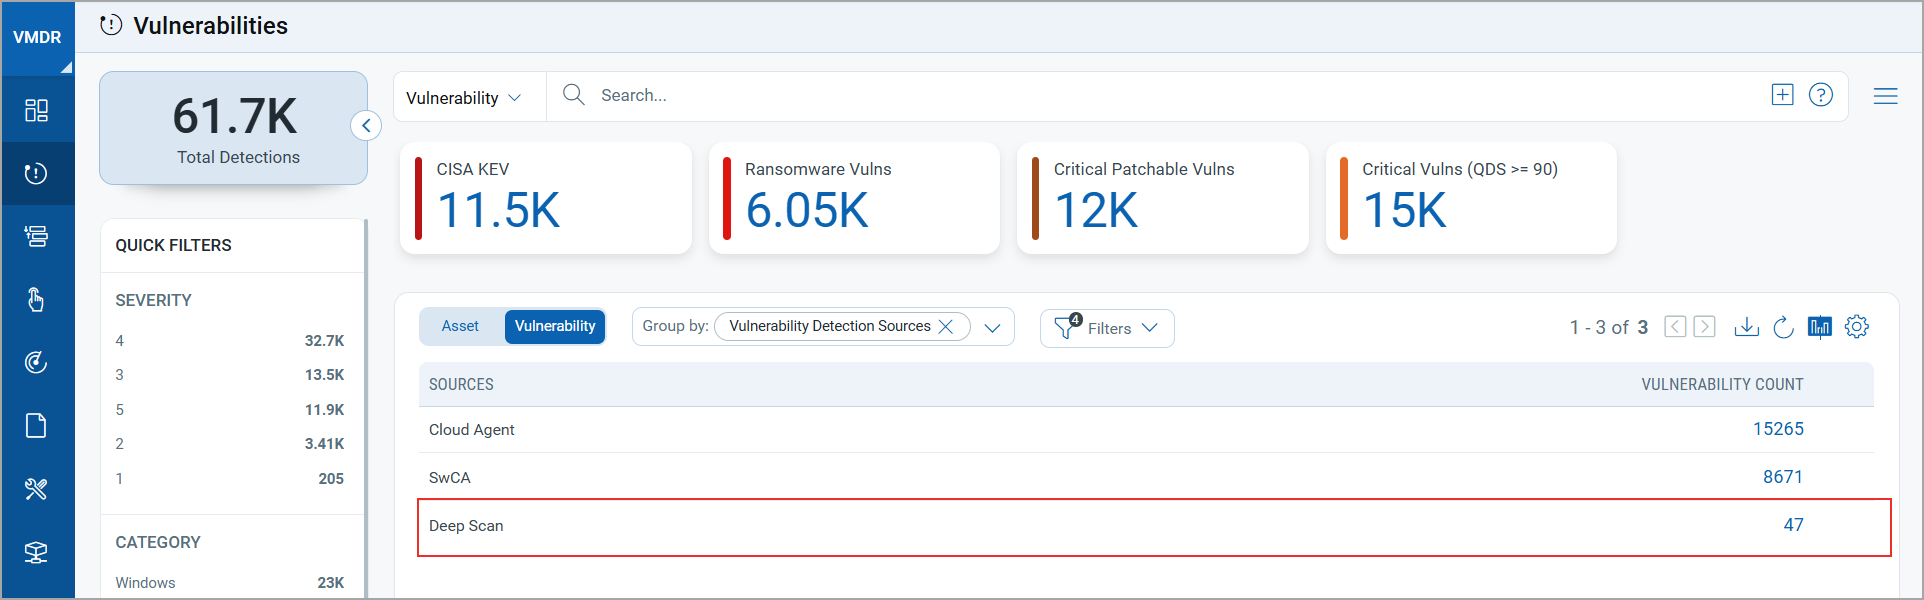
The results display vulnerabilities detected by deep scan.
Identifying Deep Scan Vulnerabilities Using VMDR KnowledgeBase
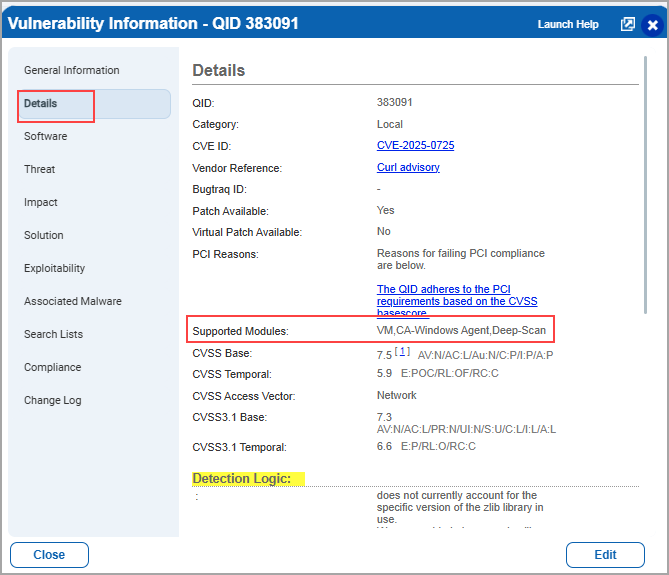
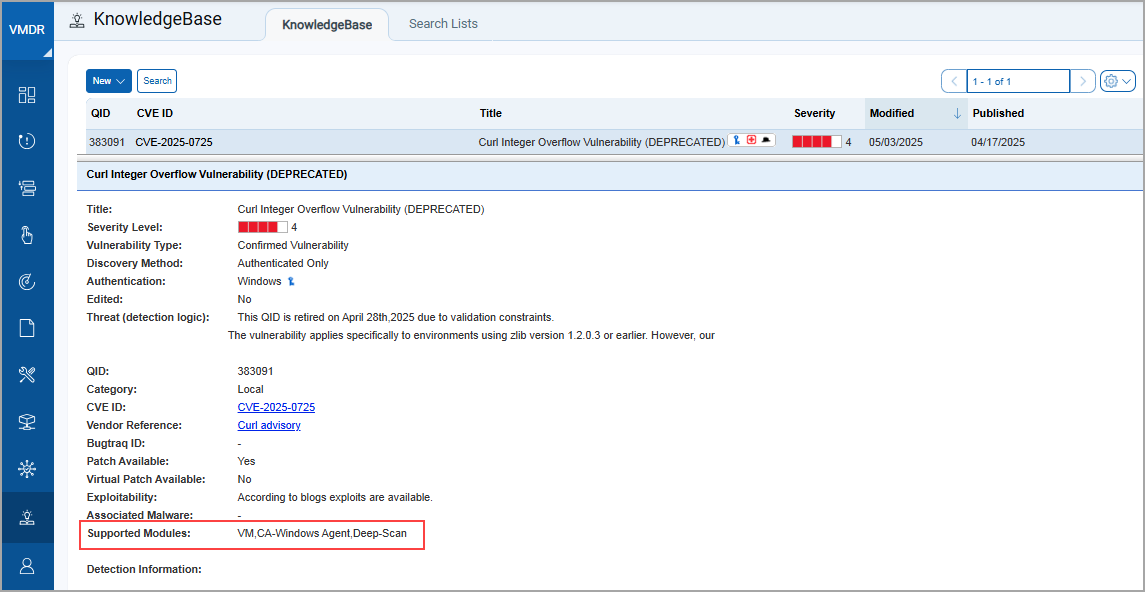
To identify vulnerabilities associated with Deep Scan, refer to the QIDs listed in the VMDR KnowledgeBase. These QIDs can be found under the Supported Modules field, accessible from both the Details tab and the QID preview page. This information supports effective remediation by providing detailed insights into Deep Scan-related vulnerabilities.
| Details Tab | QID Preview Page |
|---|---|
 |
 |
Deep Scan Behavioral Notes
The following points highlight the standard behavior of Deep Scan:
- Once enabled, Deep Scan is executed as per the schedule defined in the scan configuration.
- Results from deep scans are not retroactive and are populated only if the first scan is executed after the Cloud Agent deployment.
Related Topic: Deep Scan Overview