Cloud Posture
The cloud posture provides complete details of control evaluations for your cloud resources. Let us view the evaluation details.

Let us see what each number signifies
- Total number of controls that are evaluated.
- Total number of evaluations. A unique combination of resource and control is treated as one evaluation.
- Number of evaluations that Passed. The Pass count includes control evaluations that are passed as well as passed with exception.
- Number of evaluations that Failed.
- Number of failed evaluations with high criticality.
- Number of failed evaluations with medium criticality.
- Number of failed evaluations with low criticality.
- Number of failed evaluations for remediable controls.
When you change criticality of a control, the revised control criticality for existing evaluations is effective upon next connector run.
Each control is evaluated against the applicable resources which is represented by Total Resources. Number represented by green represents the number of pass resources that have the desired configuration as per the control. Number represented by red represents the number of failed resources.
Click any control to get details of all the resources evaluated against the control.
View Posture Across All Clouds
The All tab on the Cloud Posture page lists the control evaluations from all connected cloud providers (AWS, Azure, GCP, and OCI) in a single view, so you don't have to select a specific cloud first. You can also reach it by selecting a passed or failed slice of a chart on the Cloud Inventory Overview page.
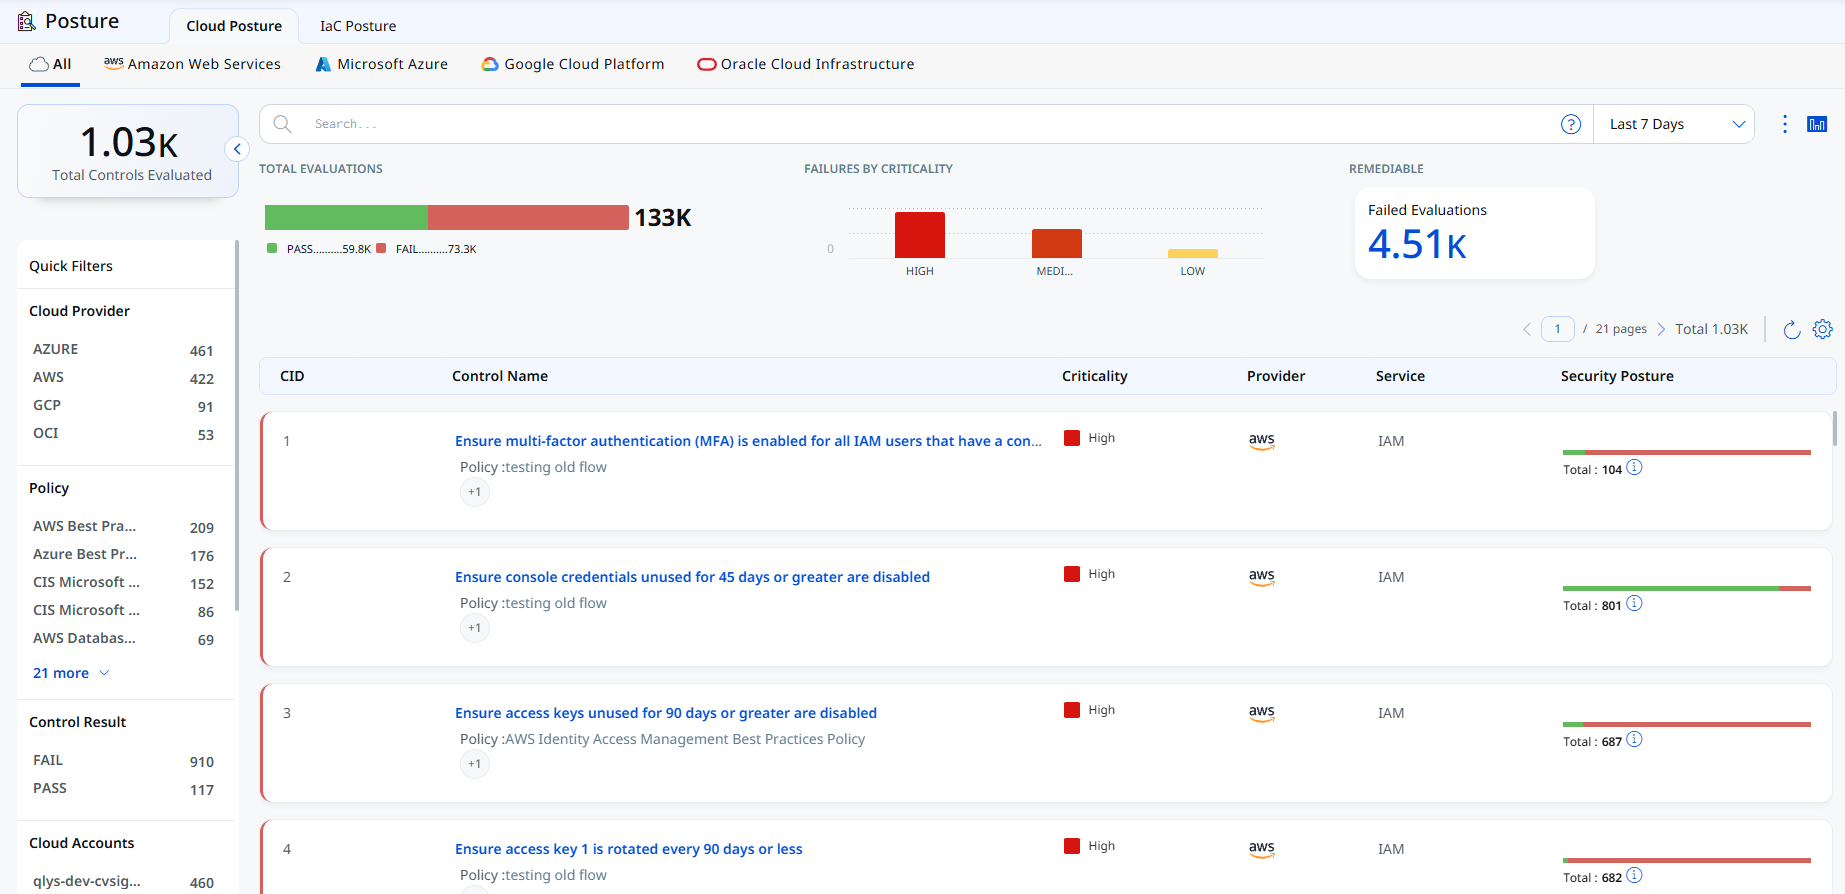
The All tab shows:
- Total Controls Evaluated: The number of controls evaluated across all clouds.
- Total Evaluations: The number of evaluations that passed and failed. Controls that passed with an exception are counted as passed.
- Failures by Criticality: The number of failed evaluations with high, medium, and low criticality.
- Remediable: The number of failed evaluations for controls that can be remediated.
- Control list: The controls with their CID, control name, criticality, cloud provider, service, and security posture (the proportion of passed and failed evaluations). Click a control to view the resources evaluated against it.
Use the Quick Filters on the left to narrow the list by cloud provider, policy, control result, cloud accounts, and so on. Each filter shows the number of matching items. You can also use the search bar to enter a QQL query, for example, by control name, CID, or service, and select a date range to change the time period.
Search Policy Controls
Find all about your policies and control evaluations, and get up-to-date information quickly using Qualys Advanced Search.
Go to Posture tab. You will notice a Search field above the controls list (you can also search on other tabs). This is where you'll enter your search query.

Start typing and we'll show you the properties you can search such as account ID, control criticality, control result, etc. Select the one you're interested in.

Now enter the value you want to match, and press Enter. You can also choose a date range. That's it! Your matches will appear in the list.

Prefer not to write a query? Use the + button next to Filters to add a custom filter by choosing a field, operator, and value. Learn more
Click the control name to view resources that passed or failed the evaluation for that specific control.

You'll notice a Search field and this is where you'll enter your search query. Start typing and we'll show you the properties you can search such as cid, control.name, and so on. Select the one you're interested in.

You could perform various actions on the controls such as re-evaluate the control, create exception for a failed resource, and so on. Select the control and click Actions or the quick actions menu. See Exceptions to know more about exceptions.

To know what led the control to pass or fail, click Evidence. The Evidence details will tell you the reason that led the control to pass or fail.

The evidence details summarize the evaluation results, including both expected and actual outcomes. You can also click on Actions and choose to Remediate Now or Re-evaluate the resource.

Known Issues
- When using the
tags.nameQQL token in the Posture tab, there is a delay in the response of the Policy Pivot filter. Upon clicking the Policy Pivot filter for the first time after applying the tag, the result set does not update as expected. The issue can be resolved by using brackets () in each QQL query. For example, use (tags.name:xyz) AND (policy.name:"AWS Best Practices Policy") instead of tags.name AND policy.name:"AWS Best Practices Policy". - The Remediation option, when chosen from within the evidence menu for the resource or account, does not work as intended. However, the "Remediate Now" option in the quick-action menu functions properly.
- When using the
tags.nameandisRemediabletokens with an AND operation in the Posture tab, theisRemediabletoken is ignored, and onlytags.nameresults are returned. The issue can be resolved by using brackets () in each QQL query. For example, use (tags.name) AND (isRemediable) instead of tags.name AND isRemediable. - When a connector tag is removed, the tag is cleared from active assets but remains on terminated assets since their discovery does not occur post-termination.
- When a connector or exception tag is applied on the Dashboard, the results are correctly displayed on the evaluation widgets. However, clicking on the widget to navigate to the respective tab (e.g., Posture) does not reflect the correct count or results. Additionally, if the same tag is applied both on the dashboard and within the widget settings, no results are displayed. Applying tags.name token individually to each widget and then navigating to respective tabs works as expected.