ETM WAS Integration
Qualys Web Application Scanning (WAS) finds vulnerabilities in your web applications. Integrating WAS with Enterprise TruRisk Management (ETM) connects those findings directly to your risk workflow, where they appear as vulnerabilities in ETM's unified risk management interface alongside every other finding in your environment.
Each finding carries the detail you need to act: the affected asset, the severity, the current status, the payload that triggered the detection, and any known exploits, patches, or associated malware. That lets your security team prioritize remediation by real risk and potential impact, without switching between management interfaces.
At a Glance
| What ETM ingests | Web application findings from WAS, ingested as vulnerabilities |
|---|---|
| Where to view | Risk Management > Findings > Vulnerabilities |
| QQL filter | finding.vendorProductName:WAS |
| How data arrives | Through a CSV connector, after you run a WAS scan |
| Detail tabs available | Summary, QDS Details, Detection Details, Exploitability, Patches, Malware, Sources |
Prerequisites
Web Application Scanning (WAS) must be enabled for your subscription before you can implement the WAS integration with ETM.
How the Integration Works
Unlike the other Qualys application integrations, WAS findings reach ETM through a CSV connector.
- Contact your Technical Account Manager (TAM) or Qualys Support to enable WAS for your subscription.
- Create a CSV connector and select WAS Findings as the Type of Findings. For instructions, see CSV Connector.
- Run a WAS scan to generate current vulnerability data.
- Web application findings from WAS appear in ETM with their respective risk scores, so that you can identify precisely which security issues require remediation.
Once set up, the integration keeps both systems synchronized, so the security posture information in ETM stays current for risk management.
View Assets and Findings in ETM
After completing the integration, you can view and manage WAS findings within the ETM interface.
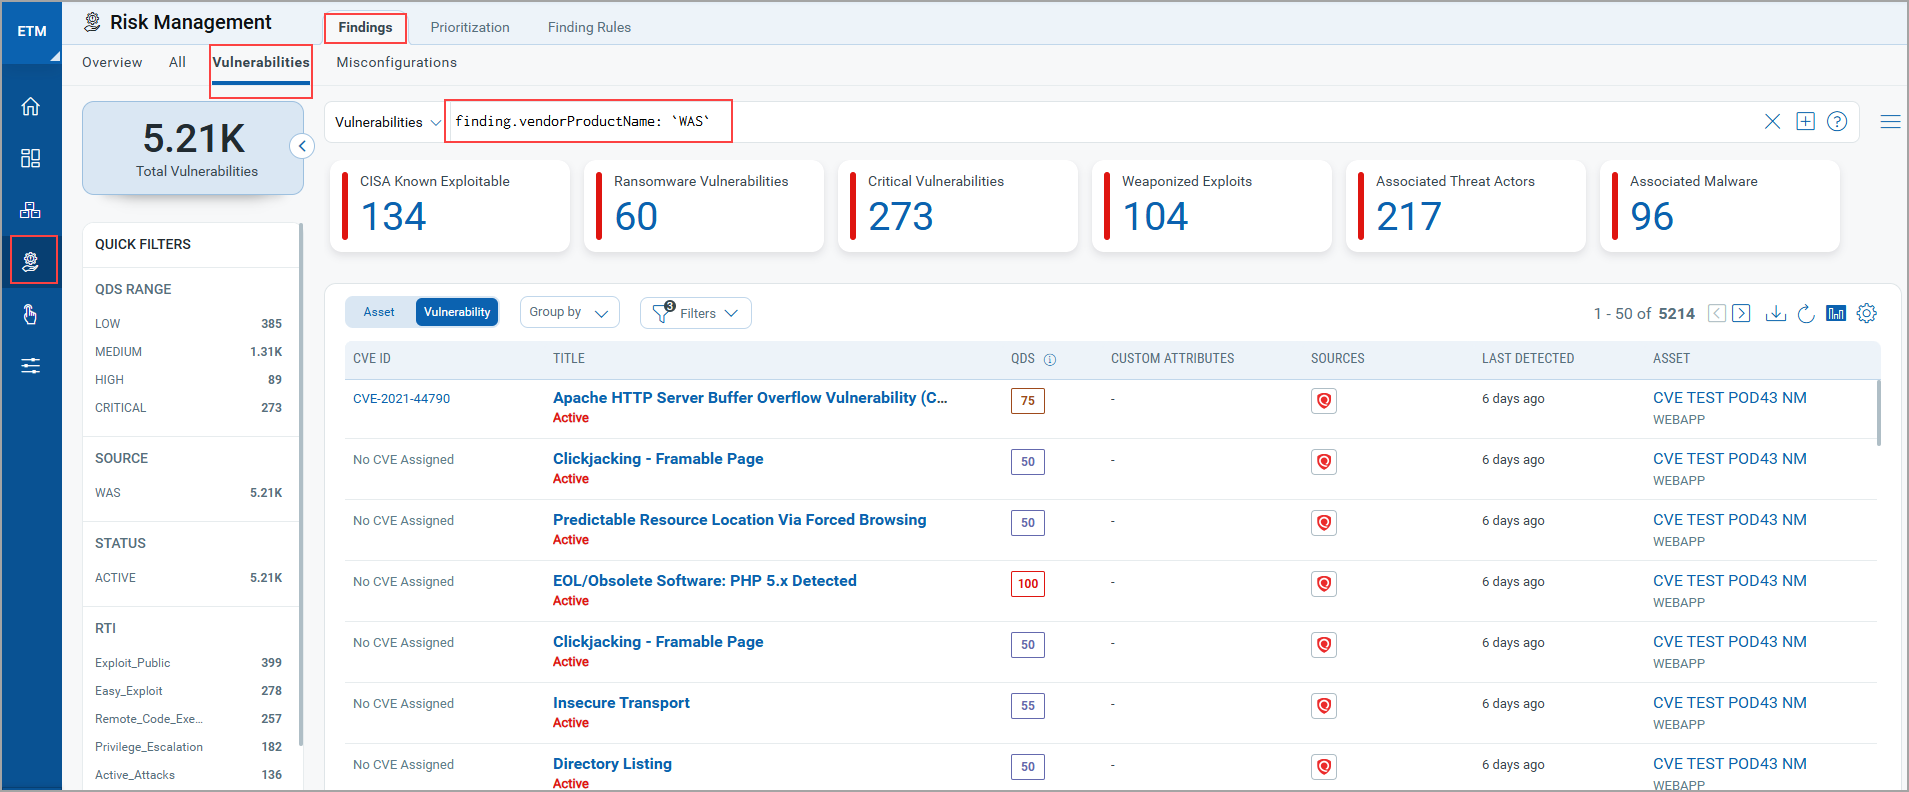
- Navigate to Risk Management > Findings > Vulnerabilities to access the consolidated view of security posture findings.
- To filter for WAS findings only, use the following QQL query:
finding.vendorProductName:WAS - To see the details of a vulnerability, select it and click View Details from the Quick Actions menu. The details open in the tabs described below.
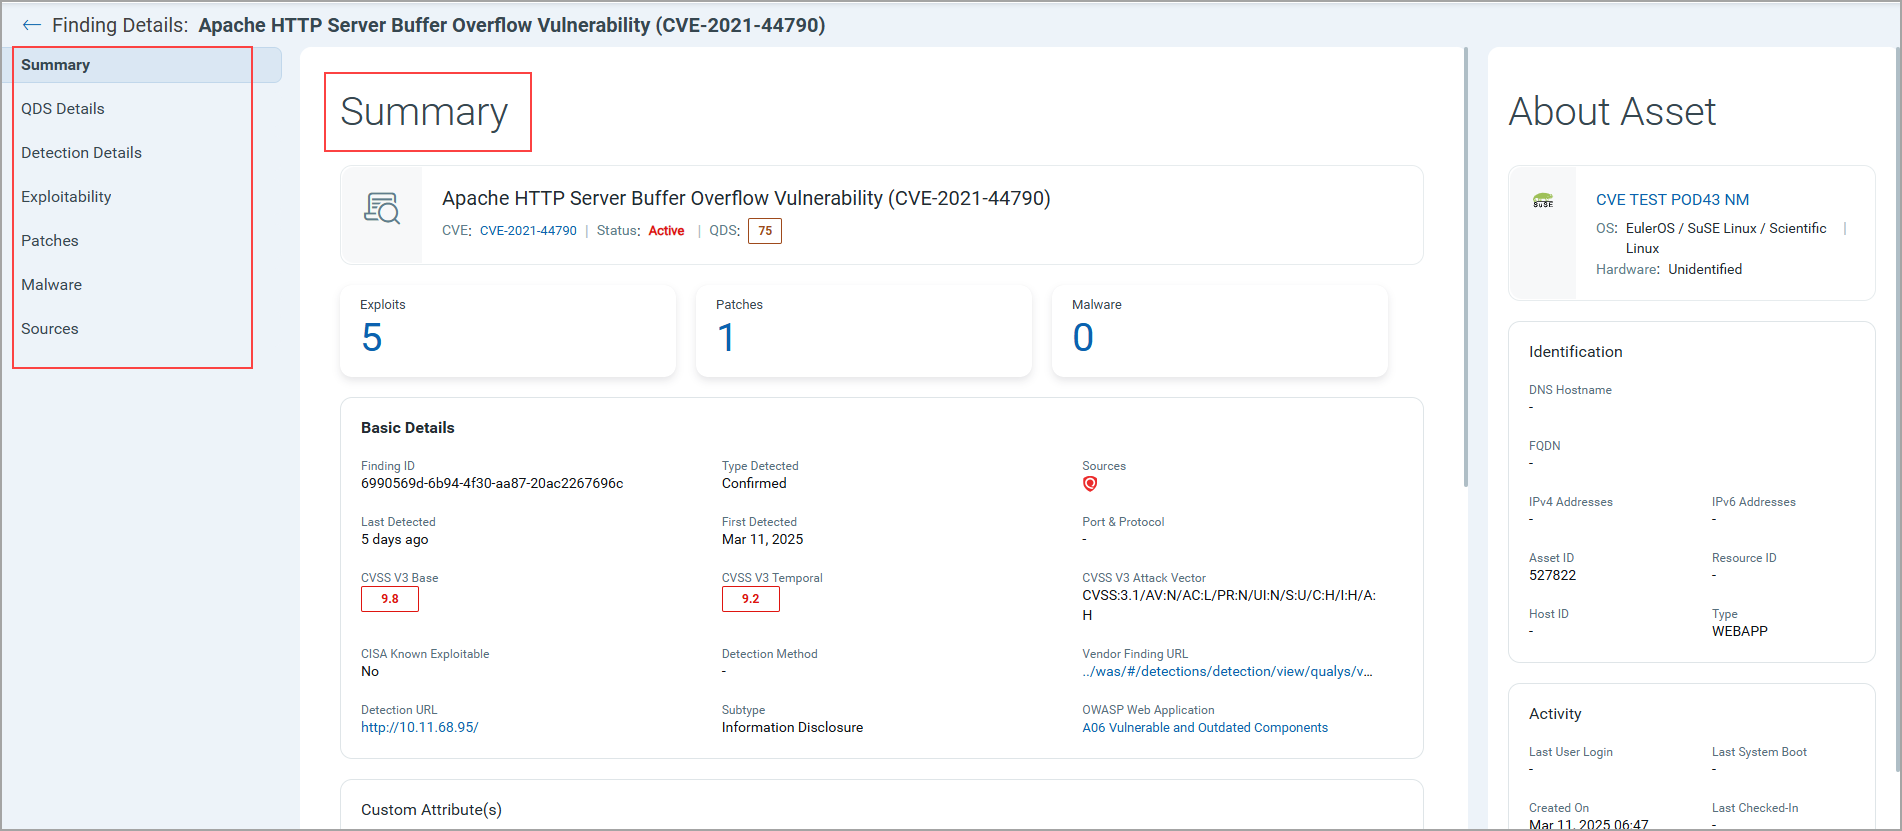
Summary
Your starting point for any finding. The Summary page collects Basic Details, Description, and Asset Information such as Identification and Activity. Basic Details include the Finding ID, the Type Detected, and whether the finding has been Confirmed. You also see Sources, the first-detected and last-detected dates, and the Port and Protocol used.
For CVSS metrics, you can find the CVSS V3 Base, CVSS V3 Temporal, and CVSS V3 Attack Vector.
QDS Details
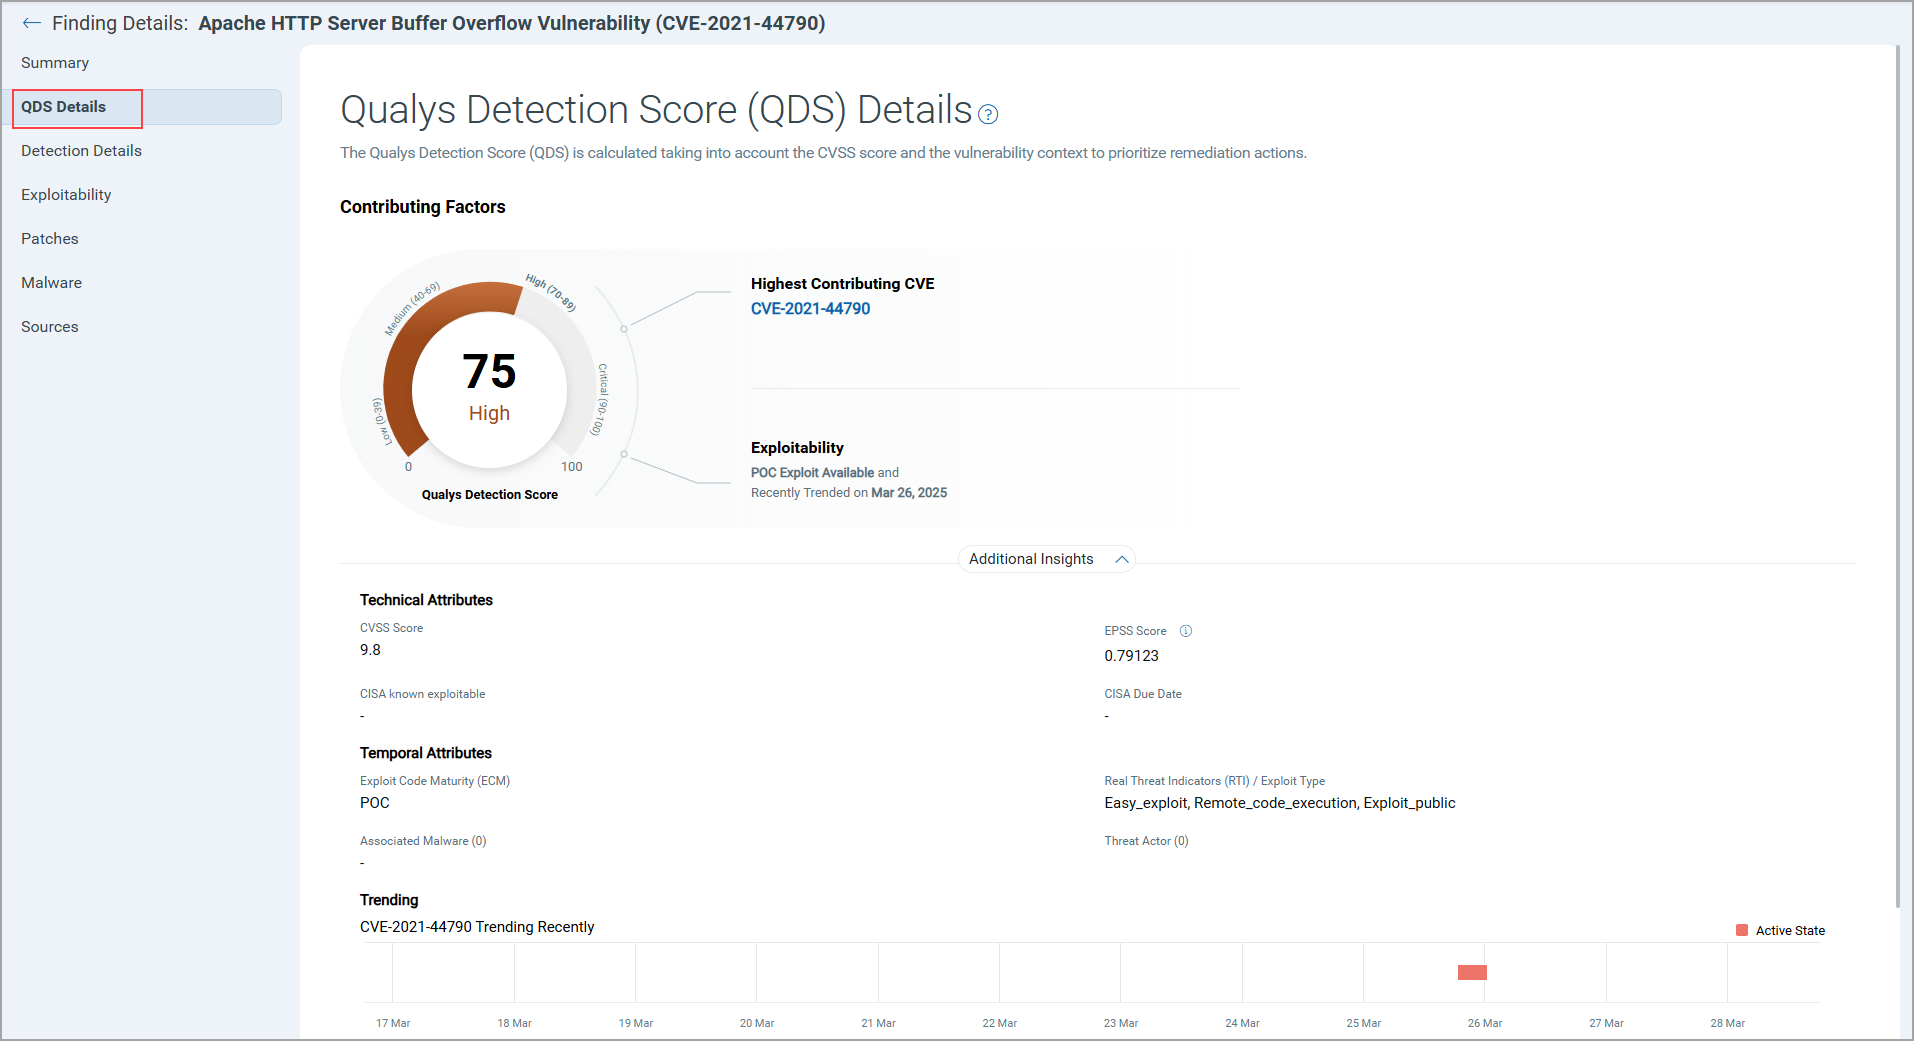
Explains why the finding scored the way it did. The Qualys Detection Score (QDS) Details tab shows the Contributing Factors behind the score, plus Additional Insights such as Technical Attributes, Temporal Attributes, Trending, and Remediation.
Detection Details
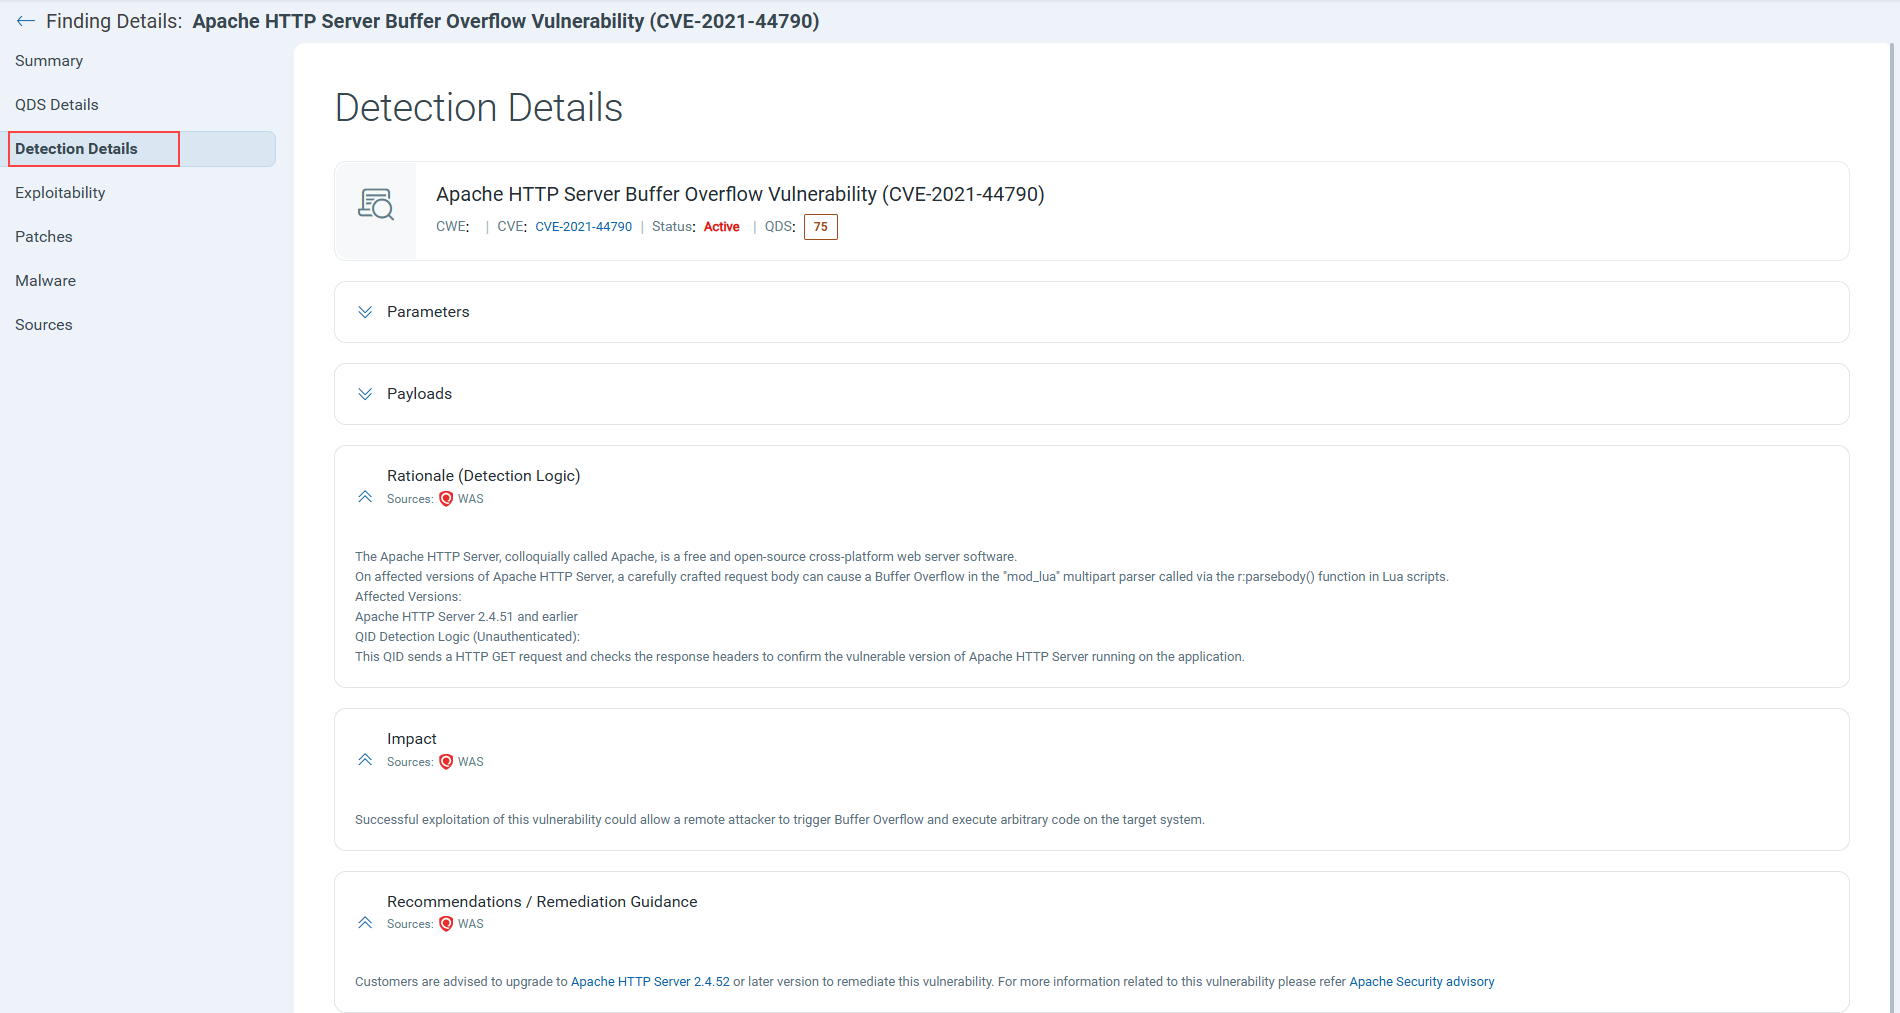
Shows how the vulnerability was proven and what to do about it: Parameters, Payloads, Payload Details, Rationale (detection logic), Impact, and Recommendations / Remediation Guidance.
Exploitability
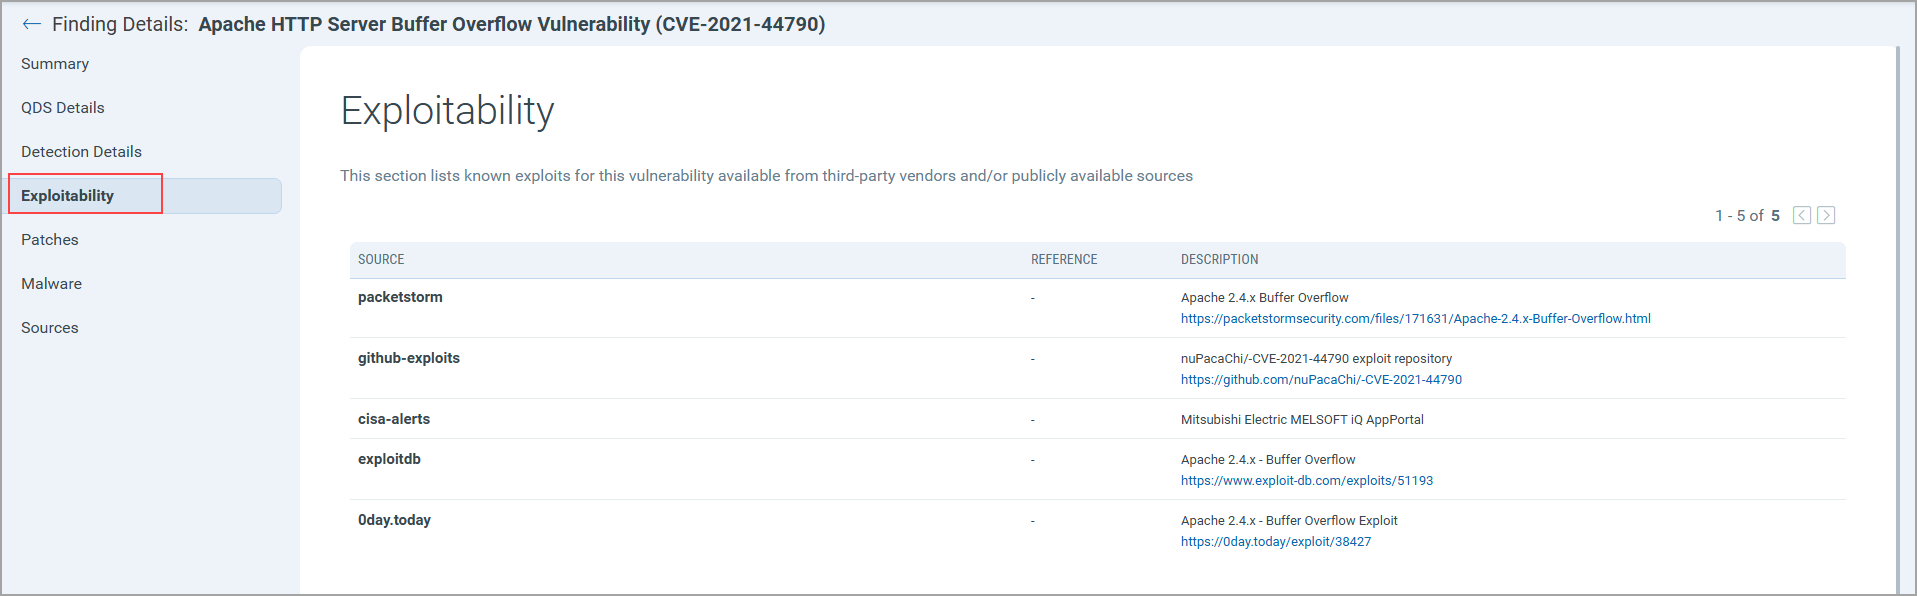
Tells you whether attackers already have a way in. The Exploitability tab lists known exploits for the vulnerability from third-party vendors and publicly available sources.
Patches
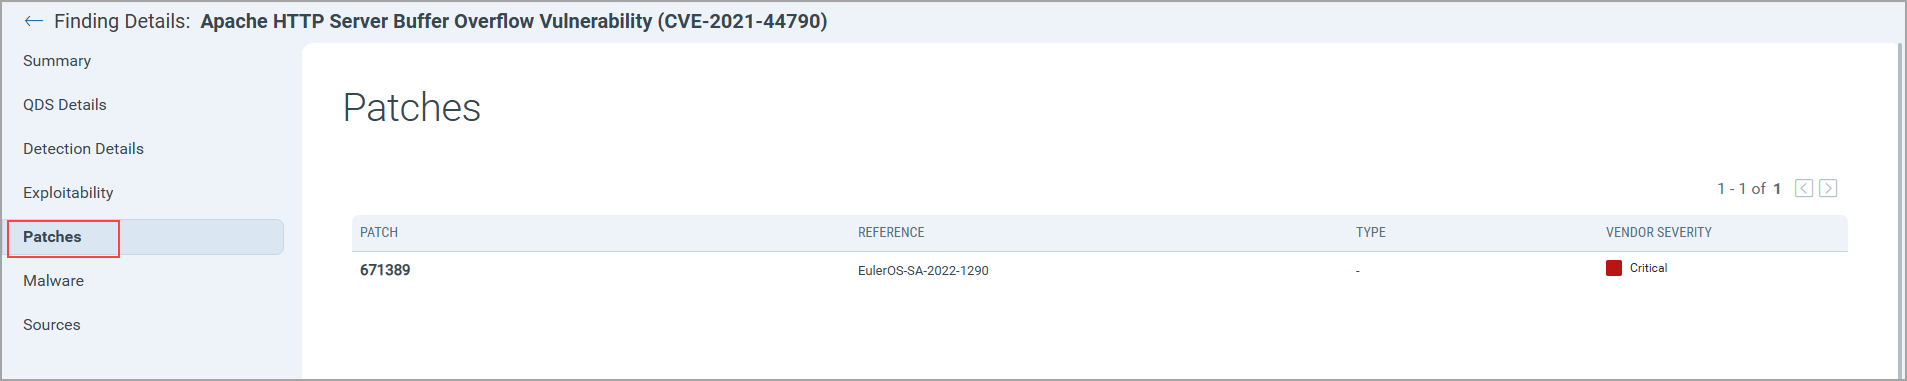
Lists the patches available for the vulnerability, with the patch reference, type, and Vendor Severity.
Malware
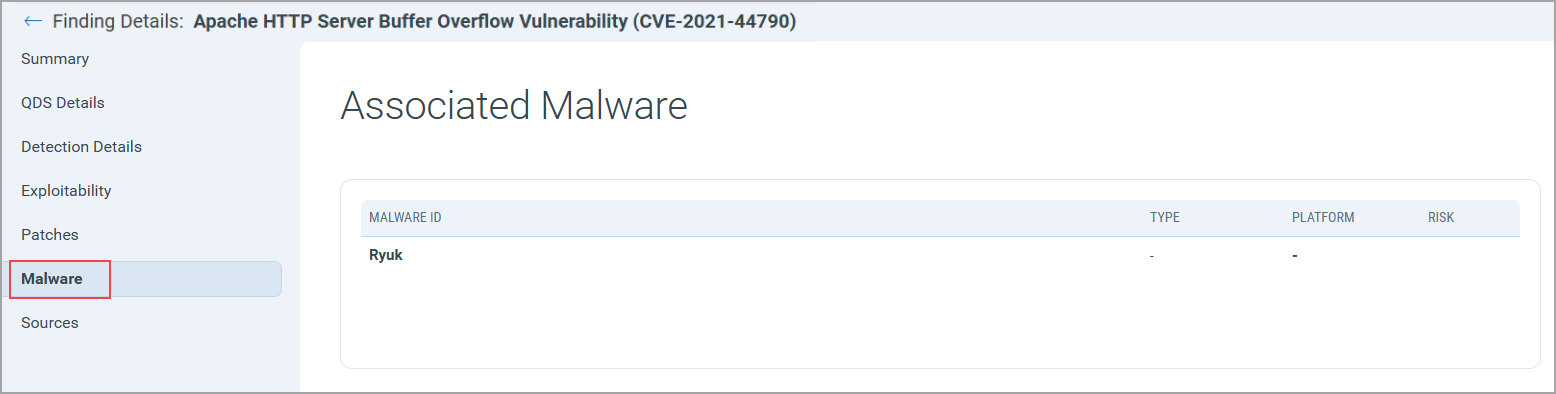
Shows malware known to be associated with the vulnerability, including Malware ID, type, Platform, and Risk.
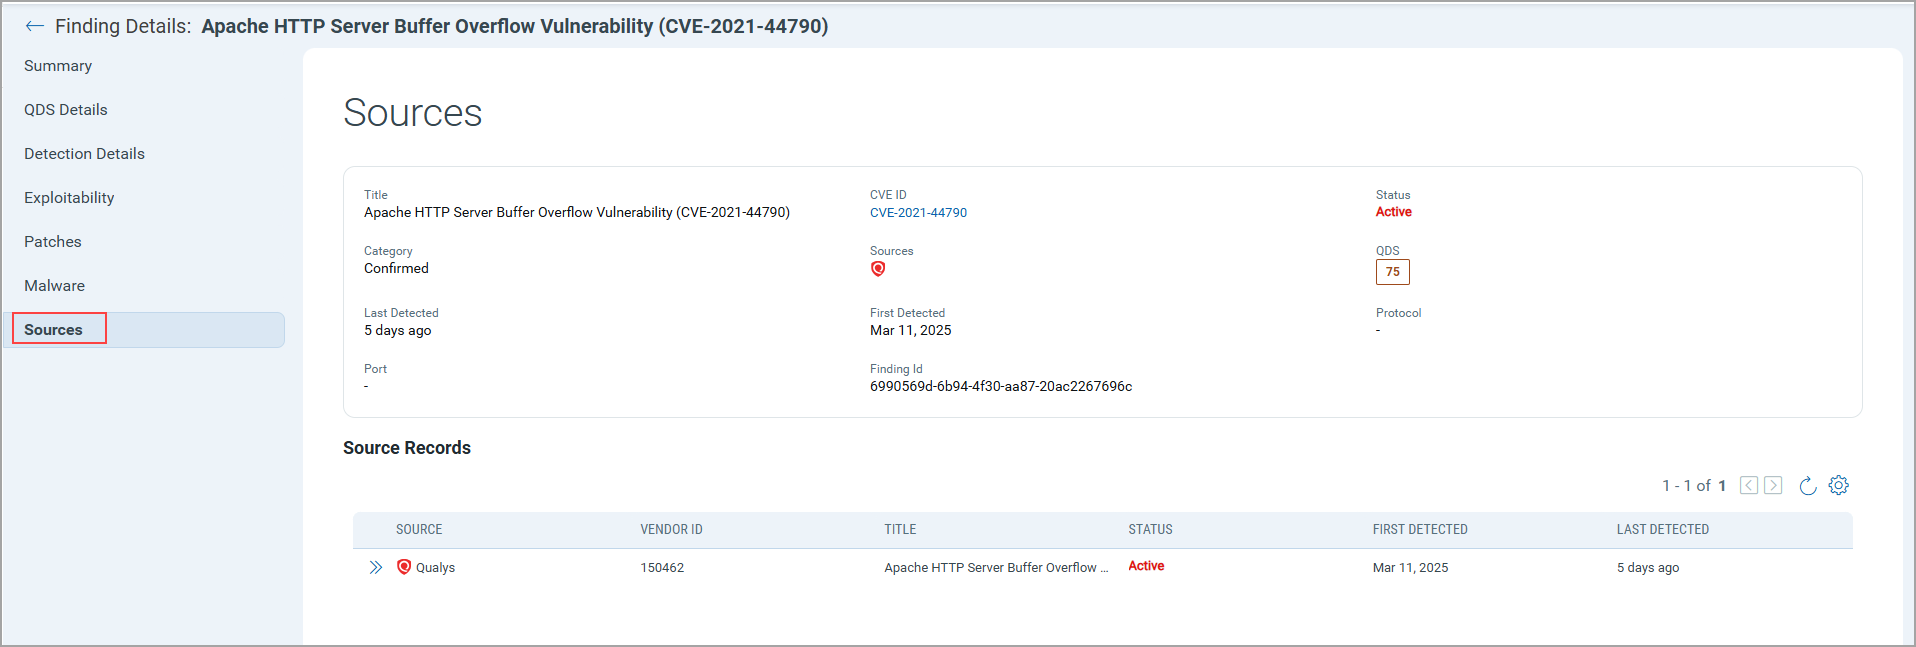
Sources
Traces the finding back to where it came from. The Sources tab shows Title, CVE ID, Status, Category, Sources, Last Detected, First Detected, Port, and Finding ID. Source Records lists the source, vendor ID, Title, Status, first detected, and last detected.