Configure Environment Parameters
You can set the configuration parameters as secrets and variables. Secrets are used to manage the sensitive configuration data and variables are used for non-sensitive configuration data.
To configure the environment parameters for a repository:
- In your repository, click Settings.
- In the left drawer menu, click Secrets and variables > Actions.
- In the Actions secrets and variables pane, click Secrets > New repository secret.
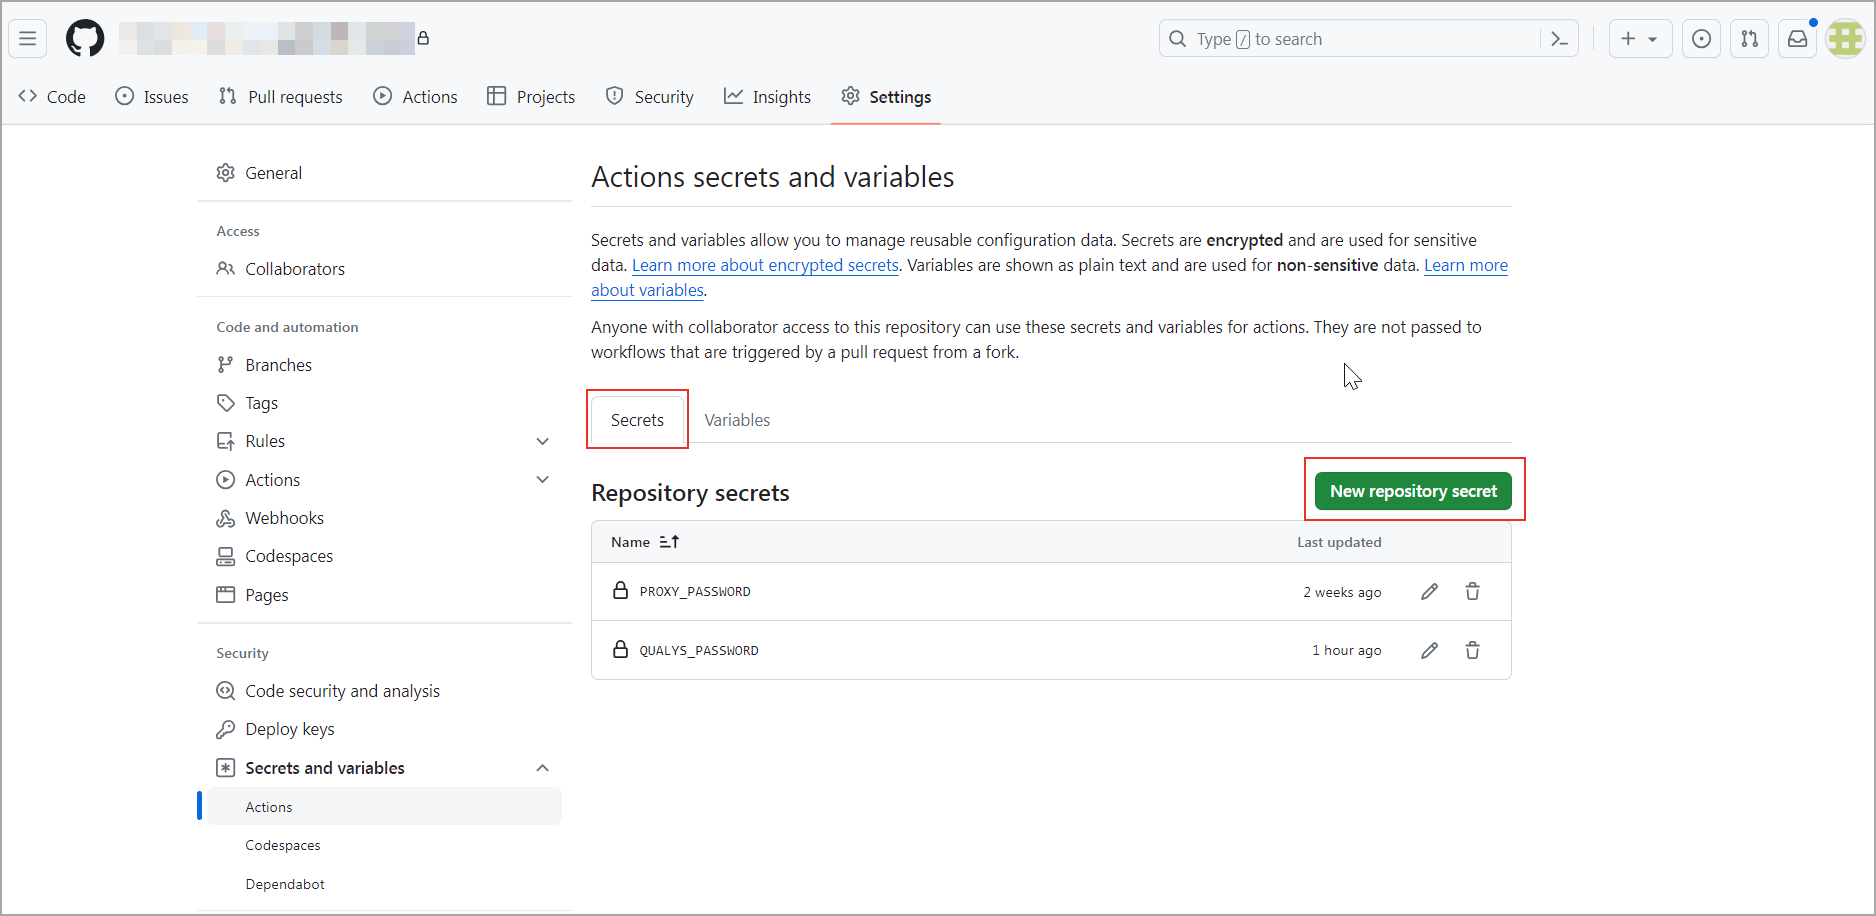
- In the New repository secret pane, enter the required information for secrets and click Add.
-
Switch to the Variables tab.
-
Click New repository variable.

-
On the New repository variable pane, enter the required details for a variable and click Add.
Authentication Type
WAS GitHub Action supports the following three authentication types. You need to enter the authentication type in the AUTH_TYPE variable.
The fields displayed below depend on the selected authentication type.
Basic Authentication
Enter Basic Authentication Details (If Selected)
Provide the following details:
- Username – Enter the Qualys username.
- Password – Enter the corresponding password.
OAuth Authentication
Provide the following details:
- Client ID – Enter the OAuth client ID.
- Client Secret – Enter the OAuth client secret.
API authentication is supported using Qualys-managed tokens via a user-level client. To create a user-level client, see Set up Token-based Authentication from UI.
Identity Provider (IDP) Authentication
Enter Identity Provider (IDP) Details (If Selected)
Provide the following details:
- Client ID – Enter the IDP client ID.
- Client Secret – Enter the IDP client secret.
- Token URL – Enter the URL of your Identity Provider (IDP) token endpoint.
- Scope – Enter the scope to request from your Identity Provider.
- Audience – Enter the audience value configured for your Identity Provider.
To generate an IDP-based authentication token, see API Authentication using IdP Provider Token.
Environment Parameters
Following is the list of environment parameters:
|
Parameter Name |
Description |
Mandatory/ Optional |
Parameter Type |
|---|---|---|---|
|
API_SERVER |
Use the API URL. To get the list of API Server URLs, refer to Platform Identification page. |
Mandatory |
Variable |
|
AUTH_TYPE |
Use this parameter to specify the authentication type. BASIC, OAUTH or IDP are supported. |
Mandatory |
Variable |
|
QUALYS_USERNAME |
Use this parameter to specify the Qualys username for BASIC authentication. |
Conditional Mandatory (Mandatory when |
Variable |
|
QUALYS_PASSWORD |
Use this parameter to specify the Qualys password for BASIC authentication. |
Conditional Mandatory (Mandatory when |
Secret |
|
CLIENT_ID |
Use this parameter to specify the client ID for OAuth and IDP authentication. |
Conditional Mandatory (Mandatory when |
Variable |
|
CLIENT_SECRET |
Use this parameter to specify the client secret for OAUTH and IDP authentication. |
Conditional Mandatory (Mandatory when |
Secret |
|
WEBAPP_ID |
Use the web application ID that you want to scan. |
Mandatory |
Variable |
|
SCAN_NAME |
Enter a name for the scan. The timestamp gets appended automatically. |
Mandatory |
Variable |
|
SCAN_TYPE |
Specify the scan type - VULNERABILITY or DISCOVERY. |
Mandatory |
Variable |
|
AUTH_RECORD |
Use one of the following values: |
Mandatory |
Variable |
|
AUTH_RECORD_ID |
Use the specific AUTH_RECORD_ID. |
Conditional Mandatory (Mandatory when AUTH_RECORD=other) |
Variable |
|
OPTION_PROFILE |
The option profile contains the various scan settings such as the vulnerability types that should be tested (detection scope), scan intensity, error thresholds, and so on. |
Mandatory |
Variable |
|
OPTION_PROFILE_ID |
Use the option profile ID of your choice. |
Conditional Mandatory (Mandatory when OPTION_PROFILE=other) |
Variable |
|
CANCEL_OPTION |
Use one of the following: |
Optional |
Variable |
|
CANCEL_HOURS |
Use the numeric value to specify scan duration in hours. |
Conditional Mandatory (Mandatory when CANCEL_OPTION=true) |
Variable |
|
SEVERITY_CHECK |
Use one of the following values: |
Optional |
Variable |
|
SEVERITY_LEVEL |
Specify the severity level of the vulnerability. You can use any values between 1-5. In Qualys, a severity level of 1 is as considered the least harmful, and a severity level of 5 is considered as most harmful. |
Conditional Mandatory (Mandatory when SEVERITY_CHECK=true) |
Variable |
|
FAIL_ON_SCAN_ERROR |
Use true or false as the parameter value. |
Optional |
Variable |
|
WAIT_FOR_RESULT |
Use one of the following values: |
Optional |
Variable |
|
INTERVAL |
Use the numeric value to set the polling interval in minutes to collect the scan data. For example, 5. |
Optional |
Variable |
|
TIMEOUT |
Use the numeric value to set the timeout duration in minutes to check the scan results. For example, 60. The default value of TIMEOUT is 350 minutes. |
Optional |
Variable |
|
EXCLUDE |
Use the QIDs separated by comma to exclude them from the scan. For example, 1234, 1345. This excludes the two QIDs for vulnerability severity level failure conditions. |
Optional |
Variable |
|
FILE_TYPE |
Specify the file format for the scan report. By default, the scan report is downloaded in the PDF format. |
Optional |
Variable |
| IDP_TOKEN_URL | The token endpoint URL of your Identity Provider. Required when AUTH_TYPE is IDP. |
Conditional Mandatory (Mandatory when |
Variable |
| IDP_SCOPE | Specifies the scope to request from the IDP token endpoint. | Optional | Variable |
| IDP_AUDIENCE | Specifies the audience to request from the IDP token endpoint. | Optional | Variable |
|
ARTIFACT_RETENTION_DAYS |
Number of days (1-90) to retain the |
Optional |
Variable |
|
SEND_MAIL |
Controls the "scan complete" email notification sent by the WAS module. |
Optional |
Variable |
All the parameter values given in the above table are case-sensitive.