Introduction to the Enterprise TruRisk Platform
Qualys delivers its platform as a cloud-native service. The centralized management layer is hosted in the Qualys cloud, eliminating the need for customers to deploy and maintain on-premises management infrastructure. This enables rapid deployment, automatic platform updates, and scalable operation across global environments, while optional agents and scanners can be deployed as required for data collection.
Platform Architecture
The Enterprise TruRisk Platform runs on a multi-tenant, highly available architecture distributed across geographically separated PODs. Each POD is an independent stack that ensures data residency compliance and fault isolation.
For you, this means your data remains in the specific POD; a disruption affecting another customer’s POD has no effect on your environment.
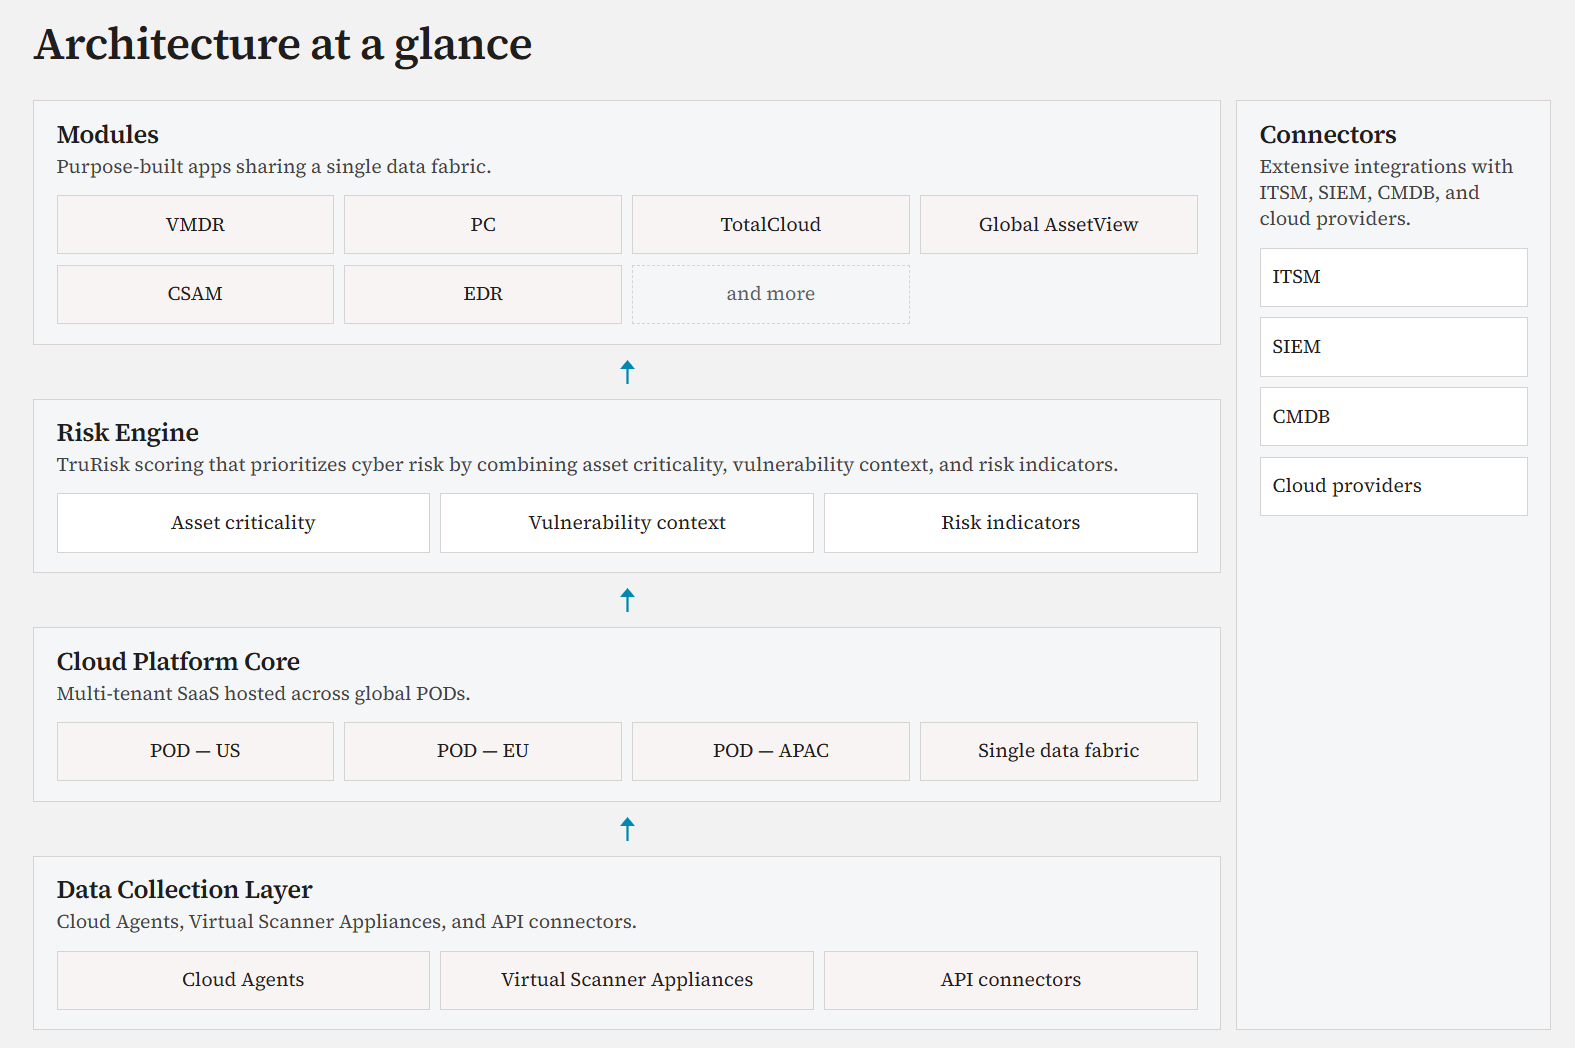
Core Platform Modules Overview
The table below summarizes the key modules relevant to most enterprise deployments.
Module |
Purpose |
| VMDR | Vulnerability Management, Detection, and Response. Identifies, prioritizes, and tracks remediation of vulnerabilities across all asset types. |
| Global AssetView | Unified asset inventory powered by the Qualys Asset Data Platform, consolidating data from agents, scanners, and connectors. Think of this as your inventory hub, a single place, all asset data lands. |
| CSAM | CyberSecurity Asset Management. Discovers unmanaged and shadow IT assets via passive network sensing, and includes External Attack Surface Management (EASM) to monitor internet-facing assets from an attacker's perspective. This is the outside-in view, what someone probing your organization from the internet would see |
| Policy Audit (PA) | Continuously audits system configurations against industry benchmarks (CIS, DISA STIG, PCI-DSS, HIPAA). |
| TotalCloud | Agentless cloud security posture management (CSPM) for AWS, Azure, GCP, and OCI. Inventories cloud resources and flags misconfigurations. |
| Container Security | Scans container images (CI/CD pipeline) and running containers for vulnerabilities and policy violations. |
| TAS | Total AppSec. Crawls and tests web applications for OWASP Top 10 and custom vulnerabilities. |
| EDR | Endpoint Detection and Response. Lightweight, agent-based telemetry for threat hunting and incident response. |
| FIM | File Integrity Monitoring. Tracks changes to critical files and directories for compliance and threat detection. |
TruRisk: The Qualys Risk Engine
TruRisk delivers a contextualized, business-aligned risk score for every asset and vulnerability. Unlike raw CVSS scores, it factors in:
- Asset Criticality Score (ACS): Administrator-defined criticality from 1 (low) to 5 (high).
- Vulnerability Severity Score: CVSS base score enriched by Qualys Threat Research.
- Threat Intelligence: Active exploitation in the wild, exploit maturity, and threat actor activity.
- Business Context: Asset tags, network exposure, and group membership.
The resulting TruRisk score answers the question every security team asks: "What do I fix first?" with precision, not guesswork.